- 65 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 6 - FortiManager 7.6 Administrator Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE6_FMG_AD-7.6 |
| Exam Name: | Fortinet NSE 6 - FortiManager 7.6 Administrator |
| Exam Questions: | 65 |
| Last Updated: | October 6, 2026 |
| Related Certifications: | NSE 6, NSE 6: Secure Networking |
| Exam Tags: |
Looking for a hassle-free way to pass the Fortinet NSE 6 - FortiManager 7.6 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE6_FMG_AD-7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE6_FMG_AD-7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE6_FMG_AD-7.6 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE6_FMG_AD-7.6 exam dumps today and achieve your certification effortlessly!
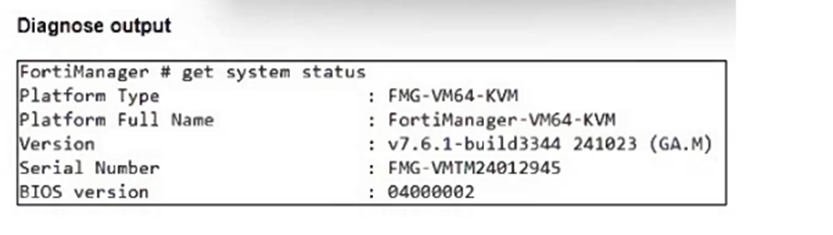
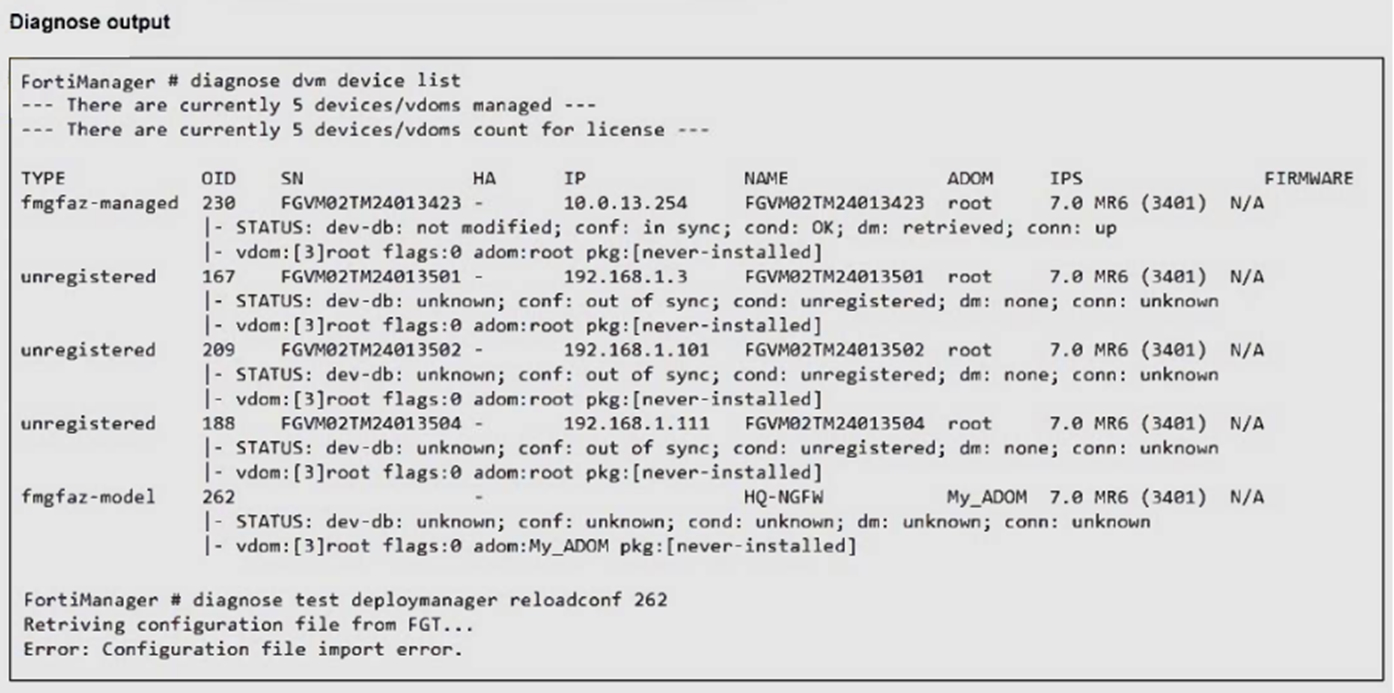
Refer to the exhibits.


An administrator runs the reload failure command diagnose test deploymanager reloadconf 262 on FortiManager.
Why does the administrator receive an error message?
The error occurs because the FortiGate HQ-NGFW device with ID 262 is a newly added model device and has not yet been fully synchronized or installed with a configuration package, which causes the reload configuration command to fail.
FortiGate is integrated with FortiAnalyzer and FortiManager.
When creating a firewall policy, which attribute must an administrator include to enhance functionality and enable log recording on FortiAnalyzer and FortiManager?
The correct answer is C. The uploaded FortiManager 7.6 Administrator Lab Guide gives the exact extract: ''FortiManager will update the universally unique identifiers (UUID) without deleting other configurations'' and ''UUIDs on both FortiGate and FortiManager are critical for ensuring the unique identification, consistency, and correct management of firewall policies across multiple devices and configurations. They provide a reliable and immutable reference for policies.''
The same source also shows administrators enabling UUIDs in Traffic Log on FortiGate log settings, which supports the logging and policy-correlation use case with FortiAnalyzer/FortiManager.
So the attribute that improves policy identification and logging correlation is the Universally Unique Identifier, not Policy ID, Log ID, or Sequence ID.
=========
Your organization uses FortiManager to manage 50 FortiGates across multiple locations. You have recently enabled workspace mode on your main ADOM to allow multiple administrators to work concurrently on policy changes. However, you notice that when Administrator A locks the ADOM to make critical changes, Administrator B is blocked from accessing any configuration until the lock is released.
What is the intended purpose of ADOM locking in workspace mode, and which statement accurately describes the behavior?
When workspace mode is enabled on an ADOM, administrators can use ADOM locking to prevent concurrent access during critical operations. When an ADOM is locked, only the administrator who holds the lock can make changes; all other administrators are blocked from editing until the lock is released. This ensures database integrity during important configuration modifications.
Why other options are incorrect:
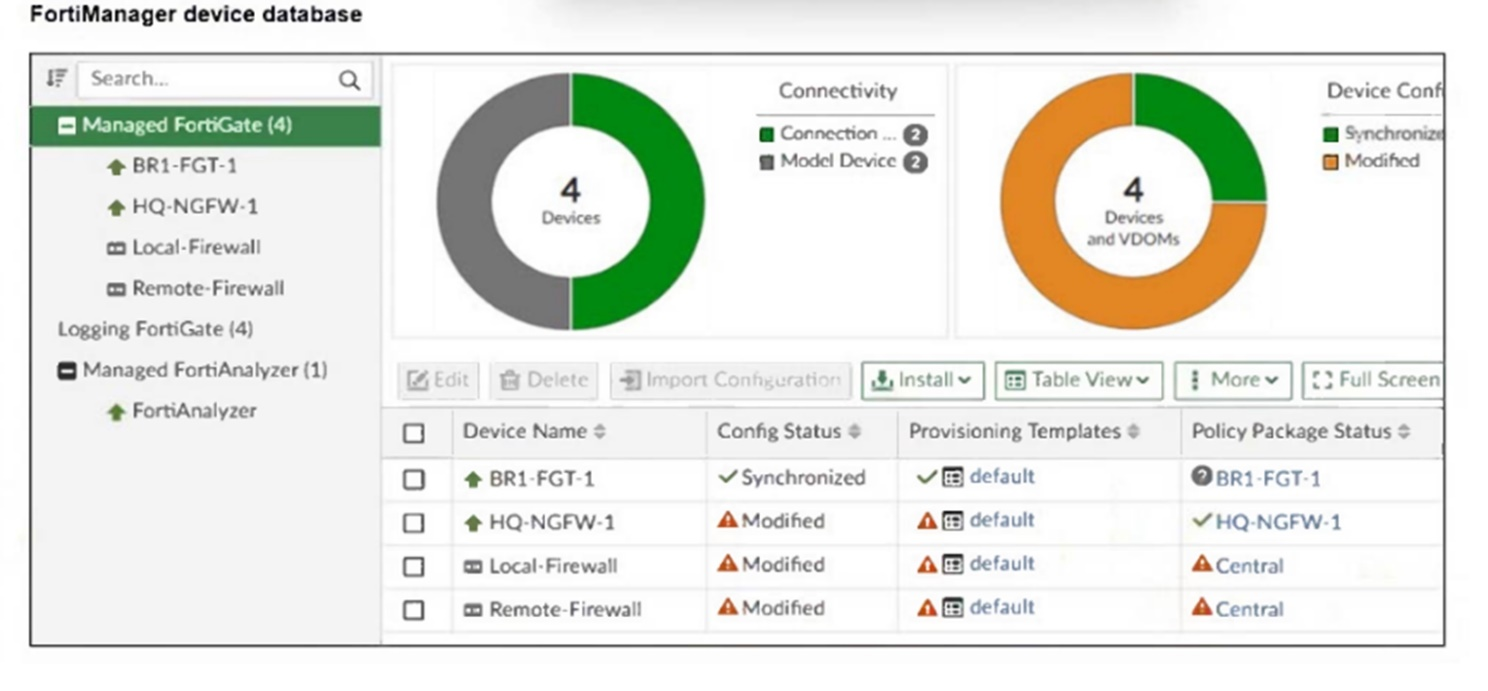
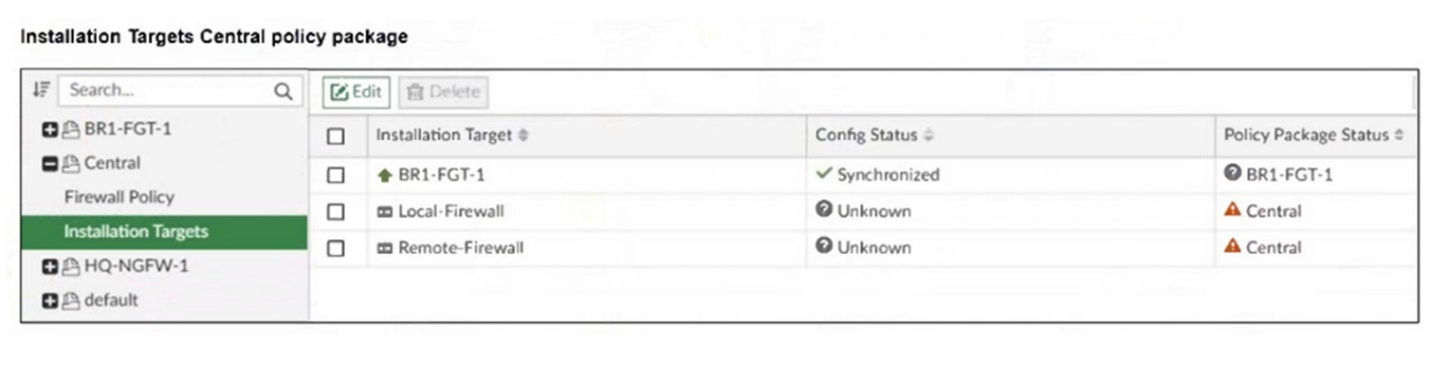
Refer to the exhibits.


An administrator has been asked to install the same policies from a central policy package onto the BR1-FGT-1 firewall.
The administrator added BR1-FGT-1 as a target in the central policy package installation.
What should the administrator do when reinstalling the central policy package on the BR1-FGT-1 firewall?
Using the Install Wizard is the recommended method to reinstall the central policy package on the BR1-FGT-1 firewall, ensuring all settings, installation targets, and dependencies are correctly processed during installation.
A FortiManager administrator opens the revision history and choose to revert to a previous version.
What will this action do to the current device configuration?
The correct answer is D. The FortiManager 7.6 Administrator Study Guide states: ''You can revert to a previous configuration revision'' and ''Reverts only the device database to the previous revision''. It also states ''Does not revert policies and objects---you must import them'' and ''You must install reverted changes on FortiGate.''
This exactly means a revert operation changes the device-level database on FortiManager, not the policy layer database. The guide further clarifies: ''Performing a revert operation followed by an installation only reverts device-level changes and does not revert policy packages.''
So C is incorrect because both layers are not reverted together. A and B are also incorrect because the documented and verified effect is specifically a modification of the device database, followed by install and, if needed, policy re-import for synchronization.
=========
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed