Fortinet NSE6_FNC_AD-7.6 Exam Dumps

Get All Fortinet NSE 6 - FortiNAC-F 7.6 Administrator Exam Questions with Validated Answers

NSE6_FNC_AD-7.6 Pack
Vendor: Fortinet
Exam Code: NSE6_FNC_AD-7.6
Exam Name: Fortinet NSE 6 - FortiNAC-F 7.6 Administrator
Exam Questions: 60
Last Updated: October 4, 2026
Related Certifications: NSE 6, NSE 6: Secure Networking
Exam Tags:
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Fortinet NSE6_FNC_AD-7.6 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 60 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 60 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 60 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Fortinet NSE6_FNC_AD-7.6 Certification Exam Easily!

Looking for a hassle-free way to pass the Fortinet NSE 6 - FortiNAC-F 7.6 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE6_FNC_AD-7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Fortinet NSE6_FNC_AD-7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE6_FNC_AD-7.6 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Fortinet NSE6_FNC_AD-7.6 Exam Prep?

  • Verified & Up-to-Date Materials: Our Fortinet experts carefully craft every question to match the latest Fortinet exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Fortinet NSE6_FNC_AD-7.6 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE6_FNC_AD-7.6 exam dumps today and achieve your certification effortlessly!

Free Fortinet NSE6_FNC_AD-7.6 Exam Actual Questions

Question No. 1

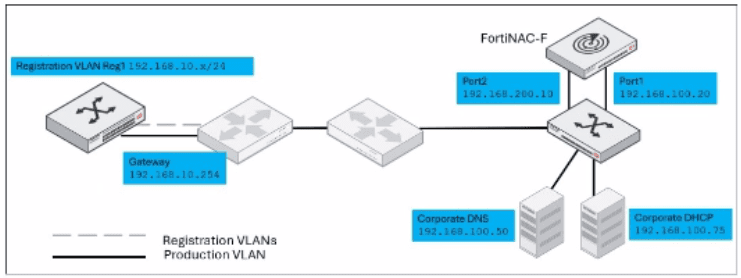
Refer to the exhibit.

Given this topology, and a layer 3 registration network configuration, which IP address would be designated in the DHCP relay configuration for the registration network?

Show Answer Hide Answer
Correct Answer: D

The correct answer is D. In a Layer 3 registration or isolation network design, DHCP requests from the isolated registration VLAN are not served locally on that VLAN by a normal production DHCP server. Instead, the registration VLAN's DHCP relay must forward DHCP traffic to FortiNAC-F port2, because port2 is the captive network service interface. The study guide states that in Layer 3 captive networks, DHCP traffic is relayed to port2 from the captive networks, and that the FortiNAC-F port2 interface provides DHCP, DNS, and captive portal services for hosts assigned to those captive networks.

In the exhibit, the registration VLAN is 192.168.10.x/24, with gateway 192.168.10.254. That gateway is where the DHCP relay would be configured, but it is not the relay destination. The relay destination must be the FortiNAC-F port2 address, shown as 192.168.200.10. The corporate DHCP server 192.168.100.75 is for production network addressing, not registration isolation. The FortiNAC-F port1 address 192.168.100.20 is the administrative or production-facing interface, not the captive network service interface. Therefore, the DHCP relay should point to 192.168.200.10.


Question No. 2

An administrator is configuring FortiNAC-F to manage FortiGate VPN users. As part of the configuration, the administrator must configure a few FortiGate firewall policies. What is the purpose of the FortiGate firewall policy that applies to clients not yet authorized by FortiNAC-F? (Choose one answer)

Show Answer Hide Answer
Correct Answer: C

The firewall policy for an unauthorized VPN host is an isolation policy. When a remote endpoint first establishes its VPN tunnel, FortiGate assigns the client an IP address plus two DNS servers: the production DNS server as primary and the FortiNAC-F Port2 VPN-context address as secondary. Until FortiNAC-F validates the endpoint, FortiGate firewall policies restrict the client's traffic so that it can communicate only with the FortiNAC-F Port2 VPN interface.

This restriction deliberately prevents access to the primary production DNS server. Consequently, DNS resolution against the primary server fails and the endpoint falls back to the secondary DNS server---FortiNAC-F. FortiNAC-F then resolves the request toward its VPN isolation interface and presents the VPN captive portal. The user can subsequently run or download the required FortiNAC-F agent, allowing FortiNAC-F to perform identification and endpoint-compliance validation.

After successful authorization, FortiNAC-F sends the appropriate group/tag information to FortiGate, causing the host to match a different firewall policy that permits the required production resources and blocks the isolation interface.

Study Guide Reference: Advanced Features FortiGate VPN Integration VPN Host Isolation and Firewall Policies, pp. 346--354.


Question No. 3

You are configuring FortiNAC-F to integrate with your organization's third-party security monitoring system that sends syslog messages about suspicious network activity and SNMP trap alerts about device anomalies. You want these third-party events to trigger automated responses in FortiNAC-F, such as isolating affected hosts or applying stricter access control policies.

Which two elements should you configure to enable this integration and automated response capability?

Show Answer Hide Answer
Correct Answer: A, B

FortiNAC-F integration with third-party systems leverages two key capabilities: (1) native support for syslog and SNMP trap input, which allows external systems to send events to FortiNAC-F, and (2) security rules that parse these incoming events and define automated responses (remediation). Additionally, (3) administrative groups for alarm notification provide centralized visibility and logging of these third-party events, enabling coordinated response across the organization.

The incorrect options represent improper integration approaches: direct API access bypasses FortiNAC-F's security controls and event parsing mechanisms; custom security rule parsers are designed for analyzing security events from integrated security devices, not raw network traffic from third-party systems; and treating the third-party system as a managed device would require it to support the FortiNAC-F management protocol, which is not applicable for generic syslog/SNMP devices. The proper method leverages FortiNAC-F's built-in event ingestion and response capabilities.

Question No. 4

A network administrator is troubleshooting a network access issue for a specific host. The administrator suspects the host is being assigned a different network access policy than expected.

Where would the administrator look to identify which network access policy, if any, is being applied to a particular host?

Show Answer Hide Answer
Correct Answer: C

When troubleshooting network access in FortiNAC-F, it is often necessary to verify exactly why a host has been granted a specific level of access. Since FortiNAC-F evaluates policies from the top down and assigns access based on the first match, an administrator needs a clear way to see the results of this evaluation for a specific live endpoint.

ThePolicy Details (C)view is the designated tool for this purpose. By navigating to theHosts > Hosts(or Adapter View) in the Administration UI, an administrator can search for the specific MAC address or IP of the host in question. Right-clicking on the host record reveals a context menu from whichPolicy Detailscan be selected. This view provides a real-time 'look' into the policy engine's decision for that specific host, showing theNetwork Access Policythat was matched, theUser/Host Profilethat triggered the match, and the resultingNetwork Access Configuration(VLAN/ACL) currently applied.

WhilePolicy Logs (A)provide a historical record of all policy transitions across the system, they are often too high-volume to efficiently find a single host's current state. TheConnections view (B)shows the physical port and basic status but lacks the granular policy logic breakdown. ThePort Properties (D)view shows the configuration of the switch interface itself, which is only one component of the final access determination.

'To identify which policy is currently applied to a specific endpoint, use thePolicy Detailsview. Navigate toHosts > Hosts, select the host, right-click and choosePolicy Details. This window displays the specificNetwork Access Policy, User/Host Profile, and Network Access Configuration currently in effect for that host record.' ---FortiNAC-F Administration Guide: Policy Details and Troubleshooting.


Question No. 5

Your FortiNAC-F deployment is integrated with multiple FortiGate firewalls using the Security Fabric connector. You have created network access policies that assign contractors to a restricted network group. To enforce these policies at the firewall level, what must be configured?

Show Answer Hide Answer
Correct Answer: A

Correct Answer: FortiNAC-F must create firewall tags that are passed to FortiGate for policy enforcement

FortiNAC-F integrates with the Security Fabric by creating firewall tags based on group and tag information derived from network access policies and host profiles. These tags are passed to FortiGate, where firewall administrators can use them in access control policies to enforce segmentation and restrict access at the network perimeter.

Why other options are incorrect:

  • Raw syslog messages for manual rule creation: Integration with Security Fabric is automated through tag passing, not manual syslog-based rule creation.
  • SNMP trap monitoring on each FortiGate: SNMP traps are used for third-party device integration into FortiNAC-F, not for FortiGate integration or device discovery.
  • VPN policies on each FortiGate: While VPN integration exists, it is for managing FortiGate VPN sessions within FortiNAC-F, not for network access policy enforcement through tags.

100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed