Fortinet NSE6_EDR_AD-7.0 Exam Dumps

Get All Fortinet NSE 6 - FortiEDR 7.0 Administrator Exam Questions with Validated Answers

NSE6_EDR_AD-7.0 Pack
Vendor: Fortinet
Exam Code: NSE6_EDR_AD-7.0
Exam Name: Fortinet NSE 6 - FortiEDR 7.0 Administrator
Exam Questions: 33
Last Updated: October 8, 2026
Related Certifications: NSE 6, NSE 6: SASE
Exam Tags:
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Fortinet NSE6_EDR_AD-7.0 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 33 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 33 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 33 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Fortinet NSE6_EDR_AD-7.0 Certification Exam Easily!

Looking for a hassle-free way to pass the Fortinet NSE 6 - FortiEDR 7.0 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE6_EDR_AD-7.0 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Fortinet NSE6_EDR_AD-7.0 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE6_EDR_AD-7.0 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Fortinet NSE6_EDR_AD-7.0 Exam Prep?

  • Verified & Up-to-Date Materials: Our Fortinet experts carefully craft every question to match the latest Fortinet exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Fortinet NSE6_EDR_AD-7.0 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE6_EDR_AD-7.0 exam dumps today and achieve your certification effortlessly!

Free Fortinet NSE6_EDR_AD-7.0 Exam Actual Questions

Question No. 1

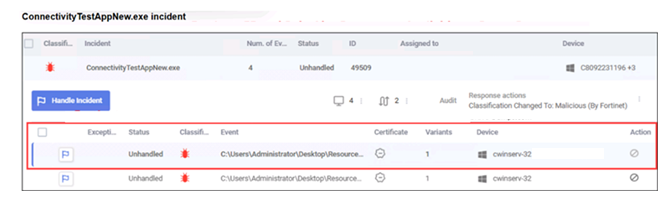
Refer to the exhibit.

What observation can you make about the ConnectivityTestAppNew.exe incident? (Choose one answer)

Show Answer Hide Answer
Correct Answer: B

The correct answer is B.

In the exhibit, the incident status clearly shows Unhandled at the incident level and also on the event rows. The FortiEDR guide explains that every detected security event is initially marked as unread and unhandled, and these statuses help multiple FortiEDR Central Manager users track whether anyone has read and handled the message.

The guide also states that when a FortiEDR Central Manager user marks a security event as Handled, all users see it as handled. The process is performed by selecting the event and clicking Handle Incident or the flag icon, then saving the incident handling details.

So the valid observation from the exhibit is that the incident has not been handled by a console administrator.

Option A is not supported by the exhibit. There is no visible evidence that the policy is in Simulation mode. Option C is wrong because the incident is still visible, not archived or deleted. Option D is wrong because the status is explicitly Unhandled; it was not handled automatically by a Communication Control policy.

=========


Question No. 2

What action does an on-premises reputation server take when it receives a hash request that is not found in its local database? (Choose one answer)

Show Answer Hide Answer
Correct Answer: C

The correct answer is C.

The FortiEDR 7.0.0 Administration Guide states that for on-premises deployments, the on-premise reputation service requests missing hashes from the cloud reputation service. If a proxy is not enabled, it requests the missing hashes from the cloud reputation service through the manager nginx. If a proxy is enabled, the on-premises reputation service requests the missing hashes through the proxy.

So, when the local reputation database does not contain the requested hash, the on-premises reputation server does not ignore the request, wait for endpoint input, or automatically block the application. It queries the cloud reputation service for the missing hash reputation data.

=========


Question No. 3

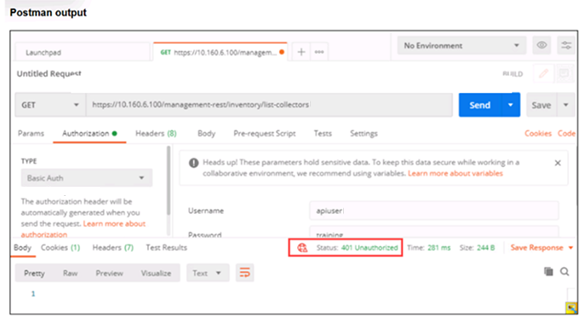
Refer to Exhibit.

Based on the Postman output shown in the exhibit, why is the user receiving an unauthorized error? (Choose one answer)

Show Answer Hide Answer
Correct Answer: C

The correct answer is C. The user account does not have the REST API role assigned.

The exhibit shows a Postman request to the FortiEDR Central Manager REST endpoint:

/management-rest/inventory/list-collectors

The response is 401 Unauthorized, which means the request reached the FortiEDR API endpoint but the supplied user credentials are not authorized for REST API access.

The FortiEDR 7.0.0 Administration Guide states that when adding or editing a user, the Rest API advanced option controls whether the user is allowed to access the FortiEDR Central Manager through API calls. The guide defines this option as: ''Rest API --- Specifies whether to allow the user to access the FortiEDR Central Manager through API calls.''

Therefore, the most accurate cause is that the account being used in Postman does not have the Rest API permission enabled.

Option A is incorrect because the request uses GET against a list endpoint, and an unsupported method would not normally be represented by this user-authentication failure. Option B is not supported by the exhibit or guide wording; the guide describes enabling REST API access per user. Option D is incorrect because first-login password reset is not the direct cause of this REST API authorization failure. The guide separately discusses password reset and password policy behavior, but that is not what the API error indicates.


Question No. 4

A collector triggers a suspicious security incident that is initially flagged as potentially malicious. The environment is connected to the FortiEDR Cloud Service (FCS) for classification. How does FCS process the event for accurate classification? (Choose one answer)

Show Answer Hide Answer
Correct Answer: A

The correct answer is A.

The FortiEDR 7.0.0 Administration Guide states that the FortiEDR Cloud Service (FCS) enriches and enhances system security by performing deep, thorough analysis and investigation about the classification of a security event. It determines the exact classification of security events with a high degree of accuracy.

The guide further explains that the FCS classification process is performed through data enrichment and enhanced deep analysis and investigation enabled by automated and manual processes. These processes may include intelligence services, static and dynamic file analysis, sandboxing, flow analysis through machine learning, commonality analysis, crowdsourced data deduction, and more.

Therefore, FCS does not rely only on FortiGate firewall policies, local signatures, or raw Collector log correlation. It performs enriched cloud-based automated and manual analysis to classify the incident accurately.

=========


Question No. 5

A collector attempts to access a known malicious website. FortiEDR is configured for eXtended detection with FortiAnalyzer. What two roles does Fortinet Cloud Services (FCS) perform in this process? (Choose two answers)

Show Answer Hide Answer
Correct Answer: C, D

The correct answers are C and D.

The guide states that for eXtended Detection Source integration, FortiEDR connects to external systems to collect activity logs. The aggregated data is then sent to Fortinet Cloud Services (FCS), where it is correlated and analyzed to detect malicious indications. Those malicious indications result in security events for eXtended Detection policy rule violations.

For FortiAnalyzer/FortiAnalyzer Cloud specifically, the guide states that this integration is used to correlate data between FortiEDR and the Fortinet Security Fabric and issue eXtended Detection alerts.

Option A is wrong because FCS does not send the original log record to FortiAnalyzer. FortiAnalyzer is the external source whose data is correlated with FortiEDR data. Option B is wrong because OS metadata is collected by the Collector and handled through FortiEDR components; the FCS role here is cloud-side enrichment, correlation, and detection, not sending OS metadata back to the manager.

=========


100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed