- 68 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 6 - FortiClient EMS 7.4 Administrator Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | FCP_FCT_AD-7.4 |
| Exam Name: | Fortinet NSE 6 - FortiClient EMS 7.4 Administrator |
| Exam Questions: | 68 |
| Last Updated: | October 4, 2026 |
| Related Certifications: | NSE 6, NSE 6: SASE |
| Exam Tags: |
Looking for a hassle-free way to pass the Fortinet NSE 6 - FortiClient EMS 7.4 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet FCP_FCT_AD-7.4 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet FCP_FCT_AD-7.4 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet FCP_FCT_AD-7.4 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet FCP_FCT_AD-7.4 exam dumps today and achieve your certification effortlessly!
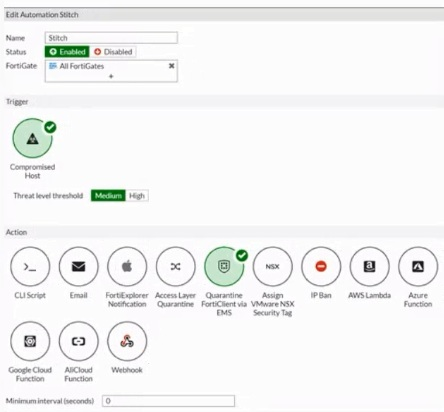
Refer to the exhibit.

Based on the Security Fabric automation settings, what action will be taken on compromised endpoints?
Based on the Security Fabric automation settings shown in the exhibit:
The automation stitch is configured with a trigger for a 'Compromised Host.'
The action specified for this trigger is 'Quarantine FortiClient via EMS.'
This indicates that when an endpoint is detected as compromised, FortiClient EMS will quarantine the endpoint as part of the automation process.
Therefore, the action taken on compromised endpoints will be to quarantine them through EMS.
Reference
FortiGate Security 7.2 Study Guide, Automation Stitches and Actions Section
Fortinet Documentation on Configuring Automation Stitches and Quarantine Actions
Which statement about FortiClient enterprise management server is true?
FortiClient EMS is designed to provide centralized management and control of multiple endpoints running FortiClient software. It serves as a central management server that allows administrators to efficiently manage and configure a large number of FortiClient installations across the network.
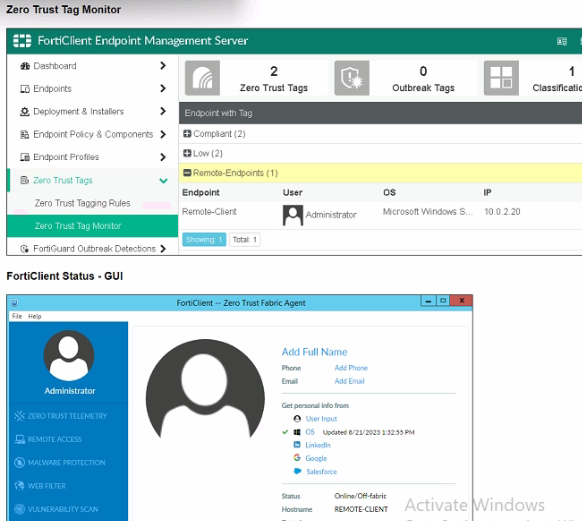
Exhibit.

Refer to the exhibits, which show the Zero Trust Tag Monitor and the FortiClient GUI status.
Remote-Client is tagged as Remote-User* on the FortiClient EMS Zero Trust Tag Monitor.
What must an administrator do to show the tag on the FortiClient GUI?
Observation of Exhibits:
The exhibits show the Zero Trust Tag Monitor on FortiClient EMS and the FortiClient GUI status.
Remote-Client is tagged as 'Remote-Endpoints' on the FortiClient EMS Zero Trust Tag Monitor.
Enabling Tag Visibility:
To show the tag on the FortiClient GUI, the endpoint alerts configuration must be adjusted to enable tag visibility.
Verification:
The correct action is to change the endpoint alerts configuration to enable tag visibility, ensuring that the tag appears in the FortiClient GUI.
FortiClient EMS and FortiClient configuration documentation from the study guides.
An administrator must deploy FortiClient for an organization that has BYOD and remote users.
What can the administrator use to deploy FortiClient? (Choose one answer)
According to the FortiClient EMS Administrator Study Guide and the Fortinet Document Library (7.2/7.4 versions), the most effective method for deploying FortiClient to BYOD (Bring Your Own Device) and remote users is using Microsoft Intune (or other supported Mobile Device Management - MDM solutions).
1. Why Microsoft Intune (Answer C) is the Correct Choice:
Cloud-Based Accessibility: Unlike GPO or SCCM, which traditionally require a direct connection to the local Active Directory (AD) domain or a VPN to reach the on-premises infrastructure, Microsoft Intune is a cloud-based MDM. This makes it the native choice for remote users who may not always be on the corporate network.
BYOD Management: Intune is specifically designed to manage a variety of operating systems (Windows, macOS, iOS, Android) that are common in BYOD environments. It allows administrators to push the FortiClient installation package and enrollment configuration (such as the invitation_code or ems_server details) directly to the user's device via the cloud.
Integration with EMS: FortiClient EMS 7.2/7.4 provides specific documentation for Intune Integration. Administrators can create a custom MSI or .pkg installer in EMS, upload it to Intune, and use Intune's app configuration policies to automate the Telemetry connection to EMS.
2. Why Other Options are Incorrect for this Scenario:
A . FortiClient zero-touch provisioning: While FortiClient supports zero-touch provisioning (particularly for mobile or through FortiCloud), in the context of a 'deployment tool' for an organization's broad BYOD and remote fleet, it is typically a feature or process facilitated by an MDM like Intune rather than the standalone deployment mechanism for the initial software package on third-party remote devices.
B . Microsoft SCCM: SCCM (now part of Microsoft Configuration Manager) is heavily reliant on on-premises infrastructure and is generally used for corporate-owned, domain-joined devices. It is less flexible than Intune for managing 'unmanaged' BYOD devices belonging to remote users.
D . Group Policy Object (GPO): GPO requires the device to be joined to the Active Directory (AD) Domain. BYOD devices are typically not domain-joined, and remote devices cannot receive GPO updates unless they are connected via VPN at the time of the policy refresh, making it unsuitable for this specific use case.
3. Curriculum Reference:
EMS Administration Guide (Deployment Section): Specifies that for endpoints not reachable via AD/Workgroups (which covers remote and BYOD), administrators should use the Installer Link method or an MDM (like Microsoft Intune).
Intune Deployment Guide for FortiClient: Detail the specific use of Configuration Keys (e.g., cloud_invite_code, ems_server) that are passed from Intune to the FortiClient app to ensure that once the remote user installs the app, it automatically registers to the correct EMS instance.
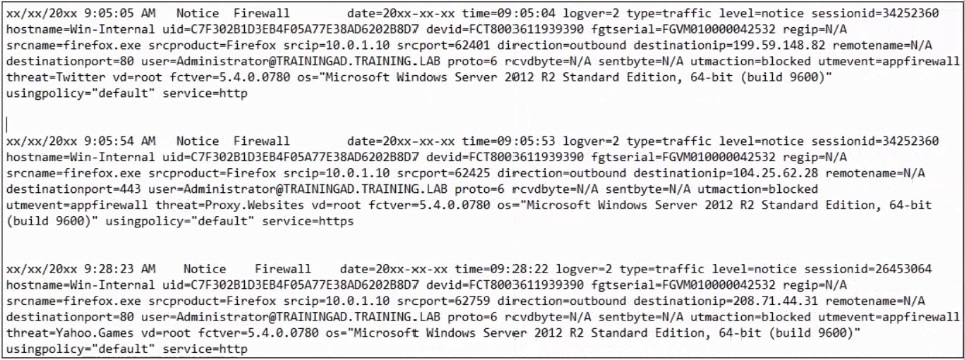
Refer to the exhibit.

Based on the FortiClient logs shown in the exhibit which application is blocked by the application firewall?
Based on the FortiClient logs shown in the exhibit:
The first log entry shows the application 'firefox.exe' trying to access a destination IP, with the threat identified as 'Twitter.'
The action taken by the application firewall is 'blocked' with the event type 'appfirewall.'
This indicates that the application firewall has blocked access to Twitter.
Reference
FortiClient EMS 7.2 Study Guide, Application Firewall Logs Section
Fortinet Documentation on Interpreting FortiClient Logs
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed