- 54 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE7_CDS_AR-7.6 |
| Exam Name: | Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect |
| Exam Questions: | 54 |
| Last Updated: | October 7, 2026 |
| Related Certifications: | NSE 7, NSE 7: Cloud Security |
| Exam Tags: |
Looking for a hassle-free way to pass the Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE7_CDS_AR-7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE7_CDS_AR-7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE7_CDS_AR-7.6 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE7_CDS_AR-7.6 exam dumps today and achieve your certification effortlessly!
An administrator is trying to implement FortiCNP with Microsoft Azure Security integration. However, FortiCNP is not able to extract any cloud integration data from Azure; therefore, real-time cloud security monitoring is not possible.
What is causing this issue?
An AWS administrator must ensure that each member of the cloud deployment team has the correct permissions to deploy and manage resources using CloudFormation. The administrator is researching which tasks must be executed with CloudFormation and therefore require CloudFormation permissions.
Which task is run using CloudFormation?
Comprehensive and Detailed Explanation From FortiOS 7.6, FortiWeb 7.4 Exact Extract study guide:
Based on the Fortinet NSE 7 - Public Cloud Security 7.4/7.6 study materials and the FortiOS 7.6 AWS Administration Guide, understanding the underlying mechanisms of AWS deployment tools is essential for permission management.
Infrastructure as Code and eksctl (Option C): In the context of Amazon EKS, the eksctl command-line tool is the official CLI for creating and managing clusters on EKS. When an administrator executes the eksctl create cluster command, eksctl does not interact with the EKS API directly to provision infrastructure; instead, it generates and executes AWS CloudFormation stacks to provision the necessary VPC, IAM roles, and the EKS control plane. Therefore, users running this command must have explicit permissions to create and manage CloudFormation stacks.
Resource Provisioning via Stacks: CloudFormation is AWS's native service for Infrastructure as Code (IaC), allowing users to define resources in JSON or YAML templates. Commands like eksctl leverage these templates to ensure repeatable and organized deployments of complex architectures, such as those required for a FortiGate or FortiWeb cloud integration.
Why other options are incorrect:
Option A: The kubectl command interacts directly with the Kubernetes API server inside the cluster to manage pods and services; it does not trigger AWS CloudFormation processes.
Option B: Helm is a package manager for Kubernetes. While it manages 'releases' within the EKS cluster, the installation of a Helm chart for a FortiWeb ingress controller happens at the Kubernetes software layer and does not utilize AWS CloudFormation stacks.
Option D: Changing the node count via CloudShell using the AWS CLI or kubectl typically modifies an Auto Scaling Group or a Kubernetes Deployment/DaemonSet directly, rather than initiating a new CloudFormation stack execution.
You are investigating an attack path for a top risky host. You notice that the Common Vulnerability Scoring System (CVSS) and the vulnerability impact scores are very high. However, the attack path severity for the top risky host itself is low. Which two pieces of contextualized information can help you understand why? (Choose two answers)
An administrator is configuring a software-defined network (SDN) connector in FortiWeb to dynamically obtain information about existing objects in an Amazon Elastic Kubernetes Service (EKS) cluster.
Which AWS policy should the administrator attach to a user to achieve this goal?
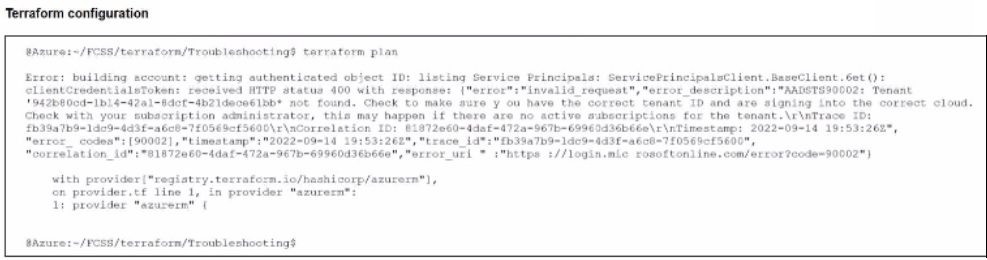
Refer to the exhibit.

After the initial Terraform configuration in Microsoft Azure, the terraform plan command is run.
Which two statements about running the terraform plan command are true? (Choose two.)
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed