- 105 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 8 - Written Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE8_812 |
| Exam Name: | Fortinet NSE 8 - Written Exam |
| Exam Questions: | 105 |
| Last Updated: | October 4, 2026 |
| Related Certifications: | Fortinet Certified Expert, FCX Fortinet Certified Expert Cybersecurity |
| Exam Tags: | Expert Fortinet networking and security experts |
Looking for a hassle-free way to pass the Fortinet NSE 8 - Written Exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE8_812 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE8_812 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE8_812 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE8_812 exam dumps today and achieve your certification effortlessly!
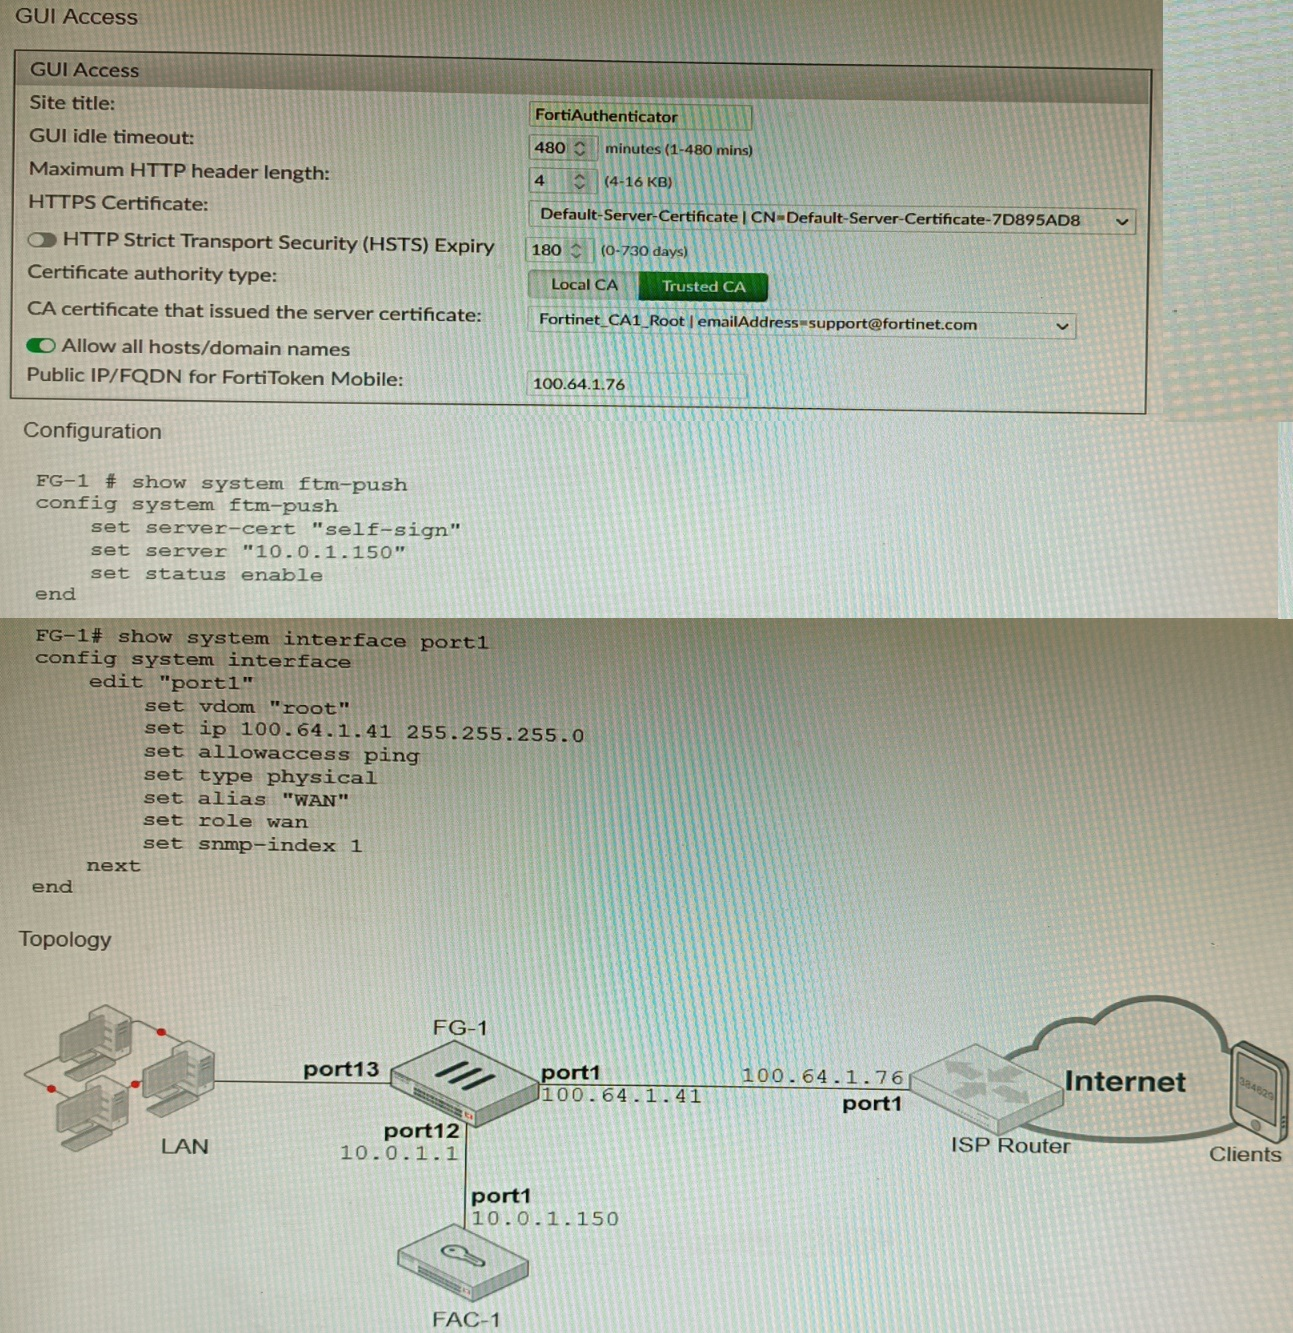
Refer to the exhibits.

An administrator has configured a FortiGate and Forti Authenticator for two-factor authentication with FortiToken push notifications for their SSL VPN login. Upon initial review of the setup, the administrator has discovered that the customers can manually type in their two-factor code and authenticate but push notifications do not work
Based on the information given in the exhibits, what must be done to fix this?
SD-WAN is configured on a FortiGate. You notice that when one of the internet links has high latency the time to resolve names using DNS from FortiGate is very high.
You must ensure that the FortiGate DNS resolution times are as low as possible with the least amount of work.
What should you configure?
SD-WAN is a feature that allows users to optimize network performance and reliability by using multiple WAN links and applying rules based on various criteria, such as latency, jitter, packet loss, etc. One way to ensure that the FortiGate DNS resolution times are as low as possible with the least amount of work is to configure local out traffic to use the outgoing interface based on SD-WAN rules with the interface IP and configure an SD-WAN rule to the DNS server. This means that the FortiGate will use the best WAN link available to send DNS queries to the DNS server according to the SD-WAN rule, and use its own interface IP as the source address. This avoids NAT issues and ensures optimal DNS performance. Reference: https://docs.fortinet.com/document/fortigate/7.0.0/sd-wan/19662/sd-wan
Refer to the exhibits.

You are configuring a Let's Encrypt certificate to enable SSL protection to your website. When FortiWeb tries to retrieve the certificate, you receive a certificate status failed, as shown below.

Based on the Server Policy settings shown in the exhibit, which two configuration changes will resolve this issue? (Choose two.)
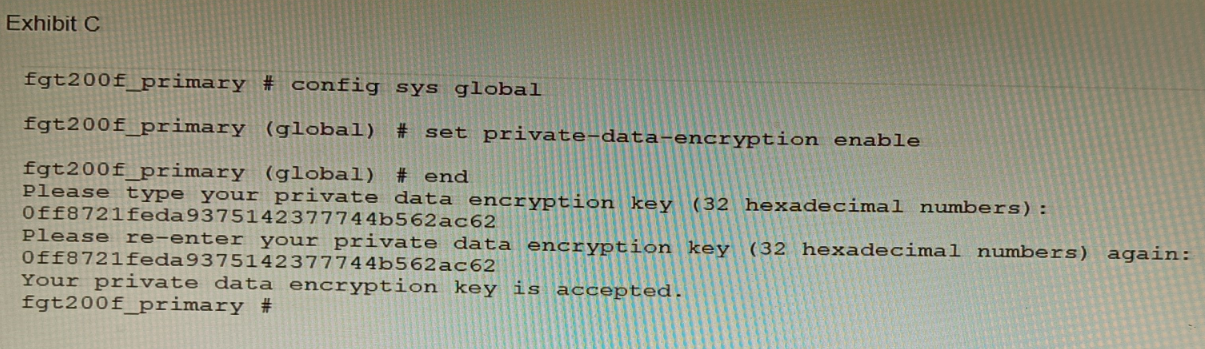
Refer to the exhibit.

A customer has deployed a FortiGate 200F high-availability (HA) cluster that contains & TPM chip. The exhibit shows output from the FortiGate CLI session where the administrator enabled TPM.
Following these actions, the administrator immediately notices that both FortiGate high availability (HA) status and FortiManager status for the FortiGate are negatively impacted.
What are the two reasons for this behavior? (Choose two.)
Refer to the exhibit.

A customer wants FortiClient EMS configured to deploy to 1500 endpoints. The deployment will be integrated with FortiOS and there is an Active Directory server.
Given the configuration shown in the exhibit, which two statements about the installation are correct? (Choose two.)
Ais correct because if no client update time is specified on EMS, the user will be able to choose the time of installation if they wish to delay. This is because the FortiClient EMS server will not force the installation on the client.
Eis correct because the Windows clients only require 'File and Printer Sharing' allowed and the rest is handled by Active Directory group policy. This is because the Active Directory group policy will configure the Windows clients to automatically install FortiClient and the FortiClient EMS server will only need to push the initial configuration to the clients.
The other options are incorrect. Option B is incorrect because a client can only be eligible for one enabled configuration on the EMS server. Option C is incorrect because you can deploy initial installations to both Windows and macOS clients. Option D is incorrect because you can use the included SQL Server Express to deploy FortiClient EMS.
Deploying FortiClient EMS | FortiClient / FortiOS 7.4.0 - Fortinet Document Library
Configuring FortiClient EMS | FortiClient / FortiOS 7.4.0 - Fortinet Document Library
FortiClient EMS installation requirements | FortiClient / FortiOS 7.4.0 - Fortinet Document Library
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed