- 93 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 4 - FortiOS 7.6 Administrator Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE4_FGT_AD-7.6 |
| Exam Name: | Fortinet NSE 4 - FortiOS 7.6 Administrator |
| Exam Questions: | 93 |
| Last Updated: | October 6, 2026 |
| Related Certifications: | NSE 4: FortiOS |
| Exam Tags: |
Looking for a hassle-free way to pass the Fortinet NSE 4 - FortiOS 7.6 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE4_FGT_AD-7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE4_FGT_AD-7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE4_FGT_AD-7.6 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE4_FGT_AD-7.6 exam dumps today and achieve your certification effortlessly!
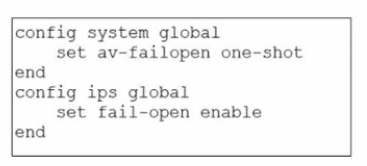
Refer to the exhibit.

Based on this partial configuration, what are the two possible outcomes when FortiGate enters conserve mode? (Choose two.)
You have configured an application control profile, set peer-o-peer traffic to Block under the Categories tab, and applied it to the firewall policy. However, you peer-to-peer traffic on known ports is passing through the FortiGate without being blocked. What FortiGate settings should you check to resolve this issue?
''After the IPS engine examines the traffic stream for a signature match, FortiGate scans packets for matches, in this order, for the application control profile:
1. Application and filter overrides...''
''Because application overrides are applied first in the scan, these two applications are allowed and generate logs.''
''The priority in which application and filter overrides are placed takes precedence.''
Technical Deep Dive:
The correct answer is C. Application and Filter Overrides.
If you already set the P2P category to Block, but some peer-to-peer traffic is still being allowed, the first thing to check is whether there is an application override or filter override that matches that traffic before the category action is applied. FortiGate processes Application and Filter Overrides before Categories, so any matching override set to Allow or Monitor will effectively bypass the category block.
Why the others are wrong:
A only affects user-facing block-page behavior for HTTP/HTTPS applications, not whether P2P is blocked.
B is for enforcing expected services on expected ports and for blocking applications on non-default ports. It is not the first place to look when a category block is being bypassed.
D concerns web categorization, not application-control category enforcement.
Operationally, this is a classic troubleshooting sequence: first inspect the override table, then the category action, then logs under Application Control to see which signature and action actually matched.
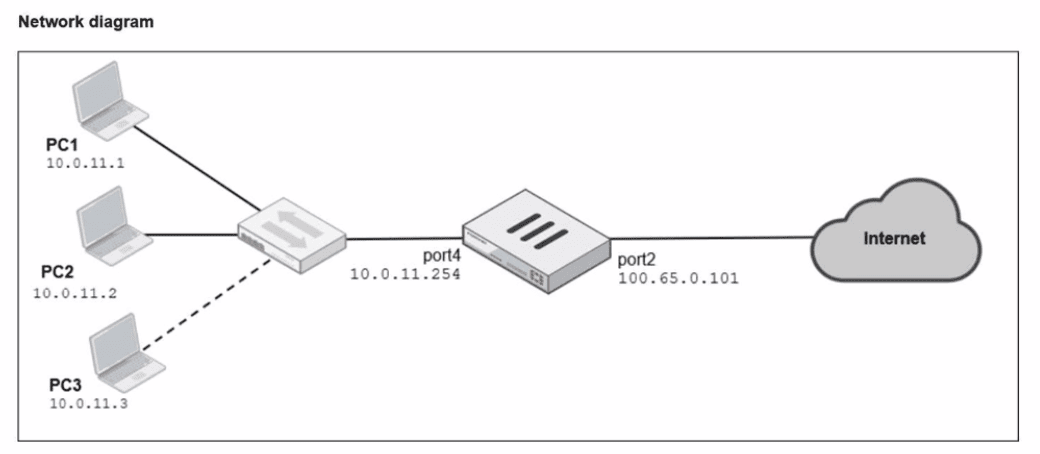
Refer to the exhibits.


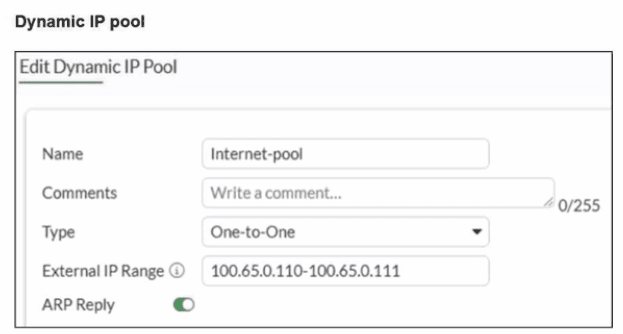
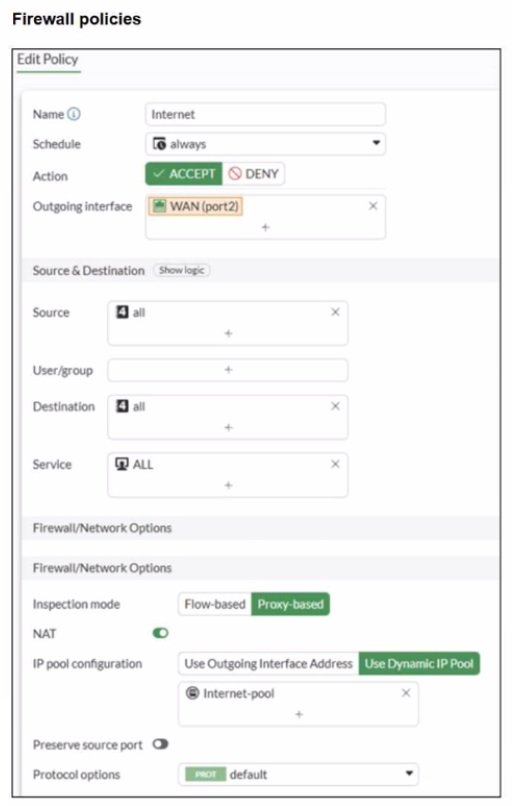
A diagram of a FortiGate device connected to the network, as well as the firewall policy and IP pool configuration on the FortiGate device are shown.
Two PCs. PC1 and PC2, are connected behind FortiGate and can access the internet successfully. However, when the administrator adds a third PC to the network (PC3), the PC cannot connect to the internet.
Based on the information shown in the exhibit, which two configuration options can the administrator use to fix the connectivity issue for PC3? (Choose two.)
From the exhibits:
The firewall policy has NAT enabled and is configured to Use Dynamic IP Pool.
The selected IP pool (Internet-pool) is configured as:
Type: One-to-One
External IP Range: 100.65.0.110--100.65.0.111 (only two public IPs)
PC1 and PC2 can access the internet because each one-to-one NAT mapping consumes one public IP from the pool. When PC3 is added, there is no third public IP available in the pool, so FortiGate cannot allocate a one-to-one mapping for PC3 and the session fails.
FortiOS behavior here is standard: with one-to-one IP pools, the available pool size limits how many distinct internal sources can be translated concurrently (depending on allocation and sessions), and a pool with only two IPs will not reliably support three separate hosts needing translations.
Therefore, the administrator can fix this in two valid ways:
B . In the IP pool configuration, set end ip to 100.65.0.112.
This expands the pool by adding an additional public IP address, making three public IPs available (.110, .111, .112), so PC3 can be assigned an address for one-to-one NAT.
D . In the IP pool configuration, set type to overload.
Changing the pool type to overload enables PAT (many-to-one), allowing multiple internal hosts (PC1, PC2, PC3) to share the pool address(es) using different source ports. This removes the ''one public IP per internal host'' limitation inherent to one-to-one pools.
Why the other options are not correct:
A . Multiple Interface Policies is unrelated to IP pool exhaustion and does not solve NAT allocation limits.
C . match-vip affects VIP matching behavior for destination NAT/virtual IP usage and does not address the source NAT pool shortage causing PC3 to fail.
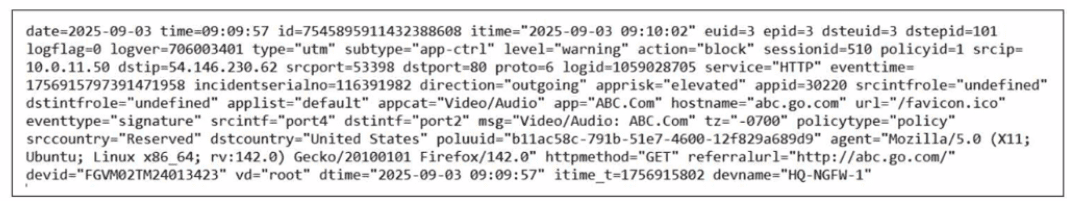
Refer to the exhibit.

Which two ways can you view the log messages shown in the exhibit? (Choose two.)
The exhibit shows a FortiGate UTM application control log with fields such as:
type='utm'
subtype='app-ctrl'
action='block'
policyid=1
appid=30220
appcat='Video/Audio'
service='HTTP'
apprisk='elevated'
This is a forward traffic security log, generated by Application Control applied to a firewall policy.
Why the correct answers are C and D
C . By filtering by policy universally unique identifier (UUID) and application name in the log entry
Correct.
FortiOS logs can be viewed and filtered in:
Log & Report Forward Traffic
Administrators can filter logs using fields such as:
Policy ID / Policy UUID
Application name (app)
Application ID (appid)
The log entry clearly includes application-related fields, making filtering by policy and application a valid and documented way to view these logs.
D . In the Forward Traffic section
Correct.
The log is a UTM Application Control log for traffic passing through a firewall policy.
Such logs are displayed under:
Log & Report Forward Traffic
This is the standard and correct location to view application control, web filter, IPS, and other security profile logs related to user traffic.
Why the other options are incorrect
A . By right clicking the implicit deny policy
Incorrect.
Implicit deny policies do not generate UTM forward traffic logs like the one shown.
Application control logs are generated only by explicit firewall policies with security profiles enabled.
B . Using the FortiGate CLI command diagnose log test
Incorrect.
diagnose log test is used to test log connectivity and log settings, not to view historical log entries.
It does not display traffic or UTM logs.
What are two features of FortiGate FSSO agentless polling mode? (Choose two.)
Based on the FortiOS 7.6 Administrator Guide regarding Fortinet Single Sign-On (FSSO) polling modes, the agentless polling mode has specific technical characteristics:
SMB Protocol Usage (Statement B is True):
In agentless polling mode, the FortiGate unit itself acts as the collector.
It establishes direct connections to the Windows Domain Controllers (DCs) using the SMB (Server Message Block) protocol, typically over TCP port 445, to read the Windows Security Event logs.
This allows FortiGate to parse login event IDs (such as 4768 and 4769) to identify users and their corresponding IP addresses without needing an external collector agent installed on a server.
Workstation Check Support (Statement C is True):
One of the primary limitations of the agentless polling mode compared to the agent-based mode is the lack of workstation verification.
In agentless mode, FortiGate does not perform 'workstation checks' or 'dead entry checks'. This means it cannot proactively verify if a user is still logged into a specific workstation after the initial logon event is recorded, which can lead to stale entries if a user logs off without a corresponding event being captured.
Why other options are incorrect:
Option A: In agentless mode, FortiGate (the FSSO daemon) performs the collection itself; it does not use the AD server as a 'collector agent' in the functional sense of FSSO architecture.
Option D: While FortiGate uses LDAP to retrieve group membership information once a user is identified, it does not 'direct' a collector agent to a remote LDAP server, as there is no external collector agent involved in this specific mode.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed