- 114 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 5 - FortiSwitch 7.6 Administrator Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE5_FSW_AD-7.6 |
| Exam Name: | Fortinet NSE 5 - FortiSwitch 7.6 Administrator |
| Exam Questions: | 114 |
| Last Updated: | October 8, 2026 |
| Related Certifications: | NSE 5, NSE 5: Secure Networking |
| Exam Tags: |
Looking for a hassle-free way to pass the Fortinet NSE 5 - FortiSwitch 7.6 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE5_FSW_AD-7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE5_FSW_AD-7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE5_FSW_AD-7.6 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE5_FSW_AD-7.6 exam dumps today and achieve your certification effortlessly!
Which interfaces on FortiSwitch send out FortiLink discovery frames by default in order to detect a FortiGate with an enabled FortiLink interface?
Fortinet FortiLink Protocol:The FortiLink protocol is Fortinet's proprietary mechanism for managing FortiSwitch units from a FortiGate firewall. It simplifies configuration and security policy enforcement across the connected network devices.
Auto-Discovery:FortiLink's auto-discovery feature means that by default, all ports on a FortiSwitch will actively send out discovery frames. This allows them to locate a FortiGate device that has a FortiLink interface enabled, streamlining the device management process.
No Configuration Needed:You don't have to manually configure individual ports for FortiLink discovery on FortiSwitch devices.
Reference
FortiSwitchOS FortiLink Guide (FortiSwitch Devices Managed by FortiOS 7.6):Refer to pages 13 and 14 for details on zero-touch management and FortiLink configuration. [https://fortinetweb.s3.amazonaws.com/docs.fortinet.com/v2/attachments/27f63c72-b083-11ec-9fd1-fa163e15d75b/FortiSwitchOS-7.6.0-FortiLink_Guide%E2%80%94FortiSwitch_Devices_Managed_by_FortiOS_7.6.pdf]
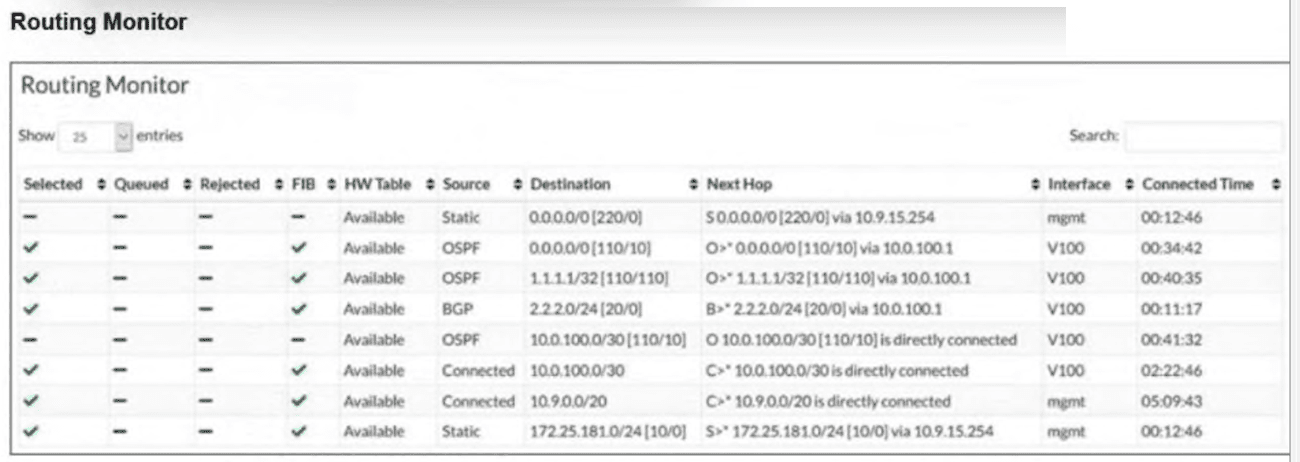
Refer to the exhibit.

and an OSPF route with destination 0.0.0.0/0 [110/10]. The OSPF route is marked with a checkmark in the FIB column, while the Static route has a dash.]
The routing monitor displays multiple route entries, but only some are installed in the forwarding information base (FIB). After analyzing the two route entries with the destination 0.0.0.0/0, which statement correctly describe why one of these routes is not installed in the FIB? (Choose one answer)
According to theFortiSwitchOS 7.6 Administration Guideand theFortiSwitch 7.6 Study Guide, the Routing Information Base (RIB) contains all potential routes discovered by the switch, but theForwarding Information Base (FIB)only includes the 'best' active routes used for hardware packet forwarding. When the routing process receives multiple paths to the exact same destination (in this case, the default route 0.0.0.0/0), it must select the most reliable source based on a specific hierarchy.
The primary tie-breaker for routes from different protocols is theAdministrative Distance (AD). AD is a value from 1 to 255 that represents the trustworthiness of the routing source, where alower value is more preferred. In the provided exhibit:
TheOSPFroute has an AD of110(shown as [110/10]).
TheStaticroute has been configured with an AD of220(shown as [220/0]).
Because the OSPF route's AD (110) is lower than the Static route's AD (220), the system considers the OSPF route to be superior. Consequently, only the OSPF route is 'Selected' and installed into theFIB. The static route remains in the RIB as a 'backup' or floating static route; it will only be moved to the FIB if the preferred OSPF route becomes unavailable. Option D is incorrect because having identical prefixes is not a 'conflict' but a standard part of route selection where AD decides the winner. Option A is incorrect because metric is only compared if the AD is identical.
Refer to the exhibit.
What two conclusions can be made regarding DHCP snooping configuration? (Choose two.)
Based on the DHCP snooping configuration details provided in the exhibit:
B . FortiSwitch is configured to trust DHCP replies coming on FortiLink interface.The configuration segment shows 'trusted ports : port2 FlInK1 MLAG0,' indicating that the FortiSwitch is configured to trust DHCP replies coming from the specified ports, including the FortiLink interface labeled FlInK1. This setup is critical in environments where the FortiLink interface connects directly to a trusted device, such as a FortiGate appliance, ensuring that DHCP traffic on these ports is considered legitimate.
D . Global configuration for DHCP snooping is set to forward DHCP client requests on all ports in the VLAN.The 'DHCP Broadcast Mode' set to 'All' under the DHCP Global Configuration indicates that DHCP client requests are allowed to broadcast across all ports within the VLAN. This setting is essential for environments needing broad DHCP client servicing across multiple access ports without restriction, facilitating network connectivity and management.
You are planning to deploy a FortiSwitch S5212-P in a converged infrastructure environment where the switch must support both traditional Ethernet devices and PoE-powered IP phones and wireless access points. The switch has 48 Gigabit Ethernet ports and 4 SFP+ uplink ports. You need to ensure that power delivery to PoE devices is consistent and that some ports can be split to provide additional connectivity for smaller modules.
Which two configuration options should you implement to support this deployment?
The correct answers are to enable PoE on appropriate ports with power budgeting, and configure split ports to support breakout modules; and to configure SFP+ ports appropriately and enable VLAN trunking on split ports for traffic segregation.
Why these are correct:
Why the other options are incorrect:
You are deploying two FortiSwitch FS-2S224F devices in a stack configuration to provide redundancy and increased port density for your data center. During the stack deployment, you configure the stack ports on both switches and perform the stacking operation. Shortly after the switches form a stack, you notice that one of the stack members is randomly being ejected from the stack intermittently, causing brief network interruptions.
Which of the following are likely causes of this stack instability? (Select all that apply)
Stack instability in FortiSwitch deployments can result from physical layer issues, firmware mismatches, or resource constraints on the stack master. A damaged or unseated stack cable will cause intermittent loss of communication between members. Firmware version mismatches can trigger automatic updates that destabilize the stack. High CPU/memory usage on the master can cause it to miss heartbeat messages, leading to member ejection.
Why the other options are incorrect: LLDP-MED (Link Layer Discovery Protocol - Media Endpoint Devices) is used for endpoint device discovery and voice VLAN configuration, not for stack member discovery—stacking uses proprietary stack communication protocols on the dedicated stack ports. FortiLink license counts do not control stack membership; they control the number of managed switches that can be linked to a FortiGate, which is a separate concern from stack stability.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed