Exam Information
5.0 (205 reviews) Reviewed by DumpsProvider Editorial Team
Free interactive sample
HPE7-A06 Short Quiz
5 Real Exam Questions - One at a Time - Instant or End-of-quiz Scoring.
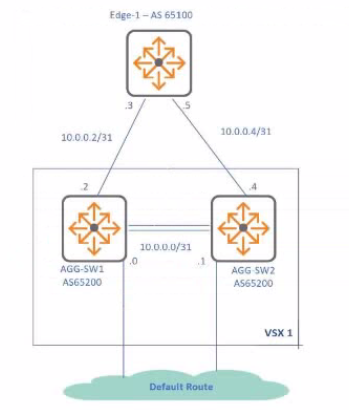
Exhibit.
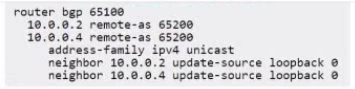
A)
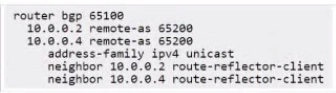
B)
C)
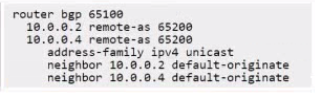
D)
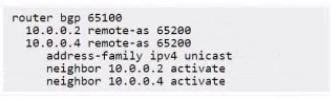
The question involves configuring an OSPF virtual link to extend area 0 across a non-backbone area, based on an exhibit (not provided) and four configuration options (A to D). Since the exhibit is unavailable, I will assume a typical scenario where a virtual link is needed to connect two area 0 segments through a transit area (e.g., area 1).
Analysis of Options (Assumed Context): A virtual link is configured using the area <transit-area> virtual-link <router-id> command in the OSPF process. The correct option likely includes:
Option A: Incorrect syntax or incorrect router ID/area for the virtual link.
Option B: Incorrect configuration, possibly missing the virtual link or using wrong parameters.
Option C: Correct. Likely includes the proper command, e.g., area 1 virtual-link 2.2.2.2, where area 1 is the transit area and 2.2.2.2 is the router ID of the remote ABR.
Option D: Incorrect, possibly configuring an unnecessary or incorrect virtual link.
Why Option C is Correct: OSPF requires all areas to connect to the backbone area (area 0). If two area 0 segments are separated by a non-backbone area (e.g., area 1), a virtual link is configured between the Area Border Routers (ABRs) to logically extend area 0 through the transit area. The command area <transit-area> virtual-link <remote-router-id> is used, specifying the transit area and the router ID of the remote ABR. Option C is assumed to provide the correct syntax and parameters based on standard OSPF virtual link configurations, ensuring area 0 connectivity and proper route advertisement.
Relevance to Certification Objectives:
Routing (16%): Designing and troubleshooting OSPF topologies, including virtual links.
Troubleshooting (10%): Resolving OSPF area connectivity issues.
HPE Aruba Networking AOS-CX Configuration Guide: OSPF Configuration, detailing virtual link setup.
HPE7-A06 Study Guide: Covers OSPF advanced configurations like virtual links.
RFC 2328: OSPF Version 2, explaining virtual link functionality.
Your customer has deployed Aruba ClearPass for centralized AAA in their campus network. Recently, they added a requirement to support dynamic VLAN assignment based on user role and device type for both wired and wireless clients. You're configuring the ClearPass Integration with the switches. Which two configurations are required to implement this workflow correctly?
This is a multiple-correct-answer question. The first correct answer describes the proper RADIUS VSA mechanism: ClearPass sends Aruba-VLAN-ID attributes in the Access-Accept message, and the switch must be configured to parse and apply these dynamically. The second correct answer reflects current ClearPass integration: the Aruba-User-Role attribute (also sent in Access-Accept) allows the switch to apply role-based policies including dynamic VLAN assignment. TPGID (option 2) is a generic RADIUS attribute not specific to Aruba's implementation. Option 3 suggests static mappings, which contradicts the dynamic requirement. Option 5 is incorrect because local authentication and ClearPass proxy authentication are independent—disabling local auth is not necessary and could break failover scenarios. The wireless controller proxy (option 5) adds unnecessary indirection and is not required for wired dynamic VLAN assignment.
You arc about lo deploy a gateway that is on factory default. ZTP cannot be used for different reasons, but you are searching for valid alternatives. What are two valid alternatives for ZTP? (Select two.)
The question asks for valid alternatives to Zero Touch Provisioning (ZTP) for initially configuring a factory default Aruba gateway when ZTP cannot be used.
Aruba Gateway Initial Provisioning Methods:
ZTP: Automated provisioning using Activate/Central.
One-Touch Provisioning (OTP) / Manual Setup: Involves direct connection for initial configuration.
Web UI: Connecting a laptop to a specific management or designated setup port (often GE0/0/1 on many gateway models) allows access to a web-based setup wizard.
Console Port: Connecting via the serial console port allows CLI access, which includes guided setup scripts or manual configuration.
Analysis of Options:
A: Port 0/0/0 is typically the OOBM port, not the standard OTP web UI port.
B: Port 0/0/1 is commonly used for OTP via Web browser on many Aruba gateway models.
C: Using the console port with terminal software for initial setup (potentially using a 'Full-Setup' wizard or script) is a standard manual method.
D: 'Static-Activate' refers to manual registration with the Activate service, not a console setup mode.
E: Requires setting a static IP, adding complexity beyond the basic OTP connection method described in B.
Conclusion: Using the designated OTP Ethernet port (commonly GE0/0/1) with a web browser (Option B) and using the console port with terminal software (Option C) are the standard, valid alternatives to ZTP for initial gateway setup.
Two CX 8325 switches are configured as a cluster using VSX for the core role and two CX 6300M in VSF for the aggregation role. When a minor software upgrade is issued on the switches, what is the method to achieve a hitless upgrade with the aggregation switches?
The question involves a minor software upgrade on a VSF (Virtual Switching Framework) stack of CX 6300M switches in the aggregation role, with CX 8325 switches in a VSX cluster as the core. The task is to identify the method for a hitless upgrade on the aggregation switches.
Analysis of Options:
Option A: Correct. VSF upgrades start with the secondary switch, followed by the primary, to ensure continuous operation without traffic disruption.
Option B: Incorrect. In-Service Software Upgrade (ISSU) is used for VSX, not VSF, and follows a different process.
Option C: Incorrect. Upgrading the primary switch first in VSF risks disrupting control plane operations.
Option D: Incorrect. ISSU is not applicable to VSF upgrades.
Why Option A is Correct: In a VSF stack, the update-software command initiates a rolling upgrade, starting with the secondary (standby) switch to ensure the primary (commander) continues handling traffic. Once the secondary is upgraded and rejoins the stack, the primary is upgraded, maintaining hitless operation. This process leverages VSF's ability to keep member switches active during upgrades, minimizing downtime. The CX 6300M's VSF implementation supports this hitless upgrade mechanism, as per HPE Aruba Networking documentation.
Relevance to Certification Objectives:
Network Resiliency and Virtualization (8%): Designing and troubleshooting VSF for high availability and hitless upgrades.
Troubleshooting (10%): Ensuring minimal disruption during software upgrades in campus networks.
HPE Aruba Networking AOS-CX Configuration Guide: VSF Software Upgrade, detailing hitless upgrade procedures.
HPE7-A06 Study Guide: Covers VSF maintenance and upgrade processes.
HPE Aruba Networking Technical Documentation: CX 6300 Series VSF Upgrade Best Practices.
Your organization is implementing 802.1X port-based network access control on a Aruba campus switch. Users are experiencing intermittent authentication failures using EAP-TLS certificates, and RADIUS authentication logs show that valid certificates are sometimes being rejected. You suspect the issue involves the certificate validation chain. Which two diagnostic steps would most effectively identify and resolve this problem?
This is a multiple-correct-answer question. The first correct answer addresses the root cause: incomplete certificate chains in the TLS handshake prevent successful validation. RADIUS packet capture allows you to inspect the actual EAP-TLS frames and verify all intermediate certificates are present. The second correct answer addresses time synchronization, which is critical for EAP-TLS since clock skew between endpoints can cause certificate validation failures; however, MD5 is deprecated in EAP-TLS modern implementations, so the synchronization check is correct but the MD5 suggestion is not. The first incorrect option attempts to mask the problem rather than solve it. The third option (disabling CRL/OCSP) removes important security validation. The fourth option's mention of MD5 is outdated; modern EAP-TLS uses SHA-256 or better. Certificate pinning (last option) bypasses the validation mechanism entirely, creating security risks and not addressing the actual handshake issue.
HPE7-A06 free sample questions and answers
HP HPE7-A06 practice quiz with correct answers for search indexing.
-
Question 1
Exhibit.
A)
B)
C)
D)
Correct answer: C
The question involves configuring an OSPF virtual link to extend area 0 across a non-backbone area, based on an exhibit (not provided) and four configuration options (A to D). Since the exhibit is unavailable, I will assume a typical scenario where a virtual link is needed to connect two area 0 segments through a transit area (e.g., area 1).
Analysis of Options (Assumed Context): A virtual link is configured using the area <transit-area> virtual-link <router-id> command in the OSPF process. The correct option likely includes:
Option A: Incorrect syntax or incorrect router ID/area for the virtual link.
Option B: Incorrect configuration, possibly missing the virtual link or using wrong parameters.
Option C: Correct. Likely includes the proper command, e.g., area 1 virtual-link 2.2.2.2, where area 1 is the transit area and 2.2.2.2 is the router ID of the remote ABR.
Option D: Incorrect, possibly configuring an unnecessary or incorrect virtual link.
Why Option C is Correct: OSPF requires all areas to connect to the backbone area (area 0). If two area 0 segments are separated by a non-backbone area (e.g., area 1), a virtual link is configured between the Area Border Routers (ABRs) to logically extend area 0 through the transit area. The command area <transit-area> virtual-link <remote-router-id> is used, specifying the transit area and the router ID of the remote ABR. Option C is assumed to provide the correct syntax and parameters based on standard OSPF virtual link configurations, ensuring area 0 connectivity and proper route advertisement.
Relevance to Certification Objectives:
Routing (16%): Designing and troubleshooting OSPF topologies, including virtual links.
Troubleshooting (10%): Resolving OSPF area connectivity issues.
HPE Aruba Networking AOS-CX Configuration Guide: OSPF Configuration, detailing virtual link setup.
HPE7-A06 Study Guide: Covers OSPF advanced configurations like virtual links.
RFC 2328: OSPF Version 2, explaining virtual link functionality.
-
Question 2
Your customer has deployed Aruba ClearPass for centralized AAA in their campus network. Recently, they added a requirement to support dynamic VLAN assignment based on user role and device type for both wired and wireless clients. You're configuring the ClearPass Integration with the switches. Which two configurations are required to implement this workflow correctly?
Correct answer: A, D
This is a multiple-correct-answer question. The first correct answer describes the proper RADIUS VSA mechanism: ClearPass sends Aruba-VLAN-ID attributes in the Access-Accept message, and the switch must be configured to parse and apply these dynamically. The second correct answer reflects current ClearPass integration: the Aruba-User-Role attribute (also sent in Access-Accept) allows the switch to apply role-based policies including dynamic VLAN assignment. TPGID (option 2) is a generic RADIUS attribute not specific to Aruba's implementation. Option 3 suggests static mappings, which contradicts the dynamic requirement. Option 5 is incorrect because local authentication and ClearPass proxy authentication are independent—disabling local auth is not necessary and could break failover scenarios. The wireless controller proxy (option 5) adds unnecessary indirection and is not required for wired dynamic VLAN assignment.
-
Question 3
You arc about lo deploy a gateway that is on factory default. ZTP cannot be used for different reasons, but you are searching for valid alternatives. What are two valid alternatives for ZTP? (Select two.)
Correct answer: B, C
The question asks for valid alternatives to Zero Touch Provisioning (ZTP) for initially configuring a factory default Aruba gateway when ZTP cannot be used.
Aruba Gateway Initial Provisioning Methods:
ZTP: Automated provisioning using Activate/Central.
One-Touch Provisioning (OTP) / Manual Setup: Involves direct connection for initial configuration.
Web UI: Connecting a laptop to a specific management or designated setup port (often GE0/0/1 on many gateway models) allows access to a web-based setup wizard.
Console Port: Connecting via the serial console port allows CLI access, which includes guided setup scripts or manual configuration.
Analysis of Options:
A: Port 0/0/0 is typically the OOBM port, not the standard OTP web UI port.
B: Port 0/0/1 is commonly used for OTP via Web browser on many Aruba gateway models.
C: Using the console port with terminal software for initial setup (potentially using a 'Full-Setup' wizard or script) is a standard manual method.
D: 'Static-Activate' refers to manual registration with the Activate service, not a console setup mode.
E: Requires setting a static IP, adding complexity beyond the basic OTP connection method described in B.
Conclusion: Using the designated OTP Ethernet port (commonly GE0/0/1) with a web browser (Option B) and using the console port with terminal software (Option C) are the standard, valid alternatives to ZTP for initial gateway setup.
-
Question 4
Two CX 8325 switches are configured as a cluster using VSX for the core role and two CX 6300M in VSF for the aggregation role. When a minor software upgrade is issued on the switches, what is the method to achieve a hitless upgrade with the aggregation switches?
Correct answer: A
The question involves a minor software upgrade on a VSF (Virtual Switching Framework) stack of CX 6300M switches in the aggregation role, with CX 8325 switches in a VSX cluster as the core. The task is to identify the method for a hitless upgrade on the aggregation switches.
Analysis of Options:
Option A: Correct. VSF upgrades start with the secondary switch, followed by the primary, to ensure continuous operation without traffic disruption.
Option B: Incorrect. In-Service Software Upgrade (ISSU) is used for VSX, not VSF, and follows a different process.
Option C: Incorrect. Upgrading the primary switch first in VSF risks disrupting control plane operations.
Option D: Incorrect. ISSU is not applicable to VSF upgrades.
Why Option A is Correct: In a VSF stack, the update-software command initiates a rolling upgrade, starting with the secondary (standby) switch to ensure the primary (commander) continues handling traffic. Once the secondary is upgraded and rejoins the stack, the primary is upgraded, maintaining hitless operation. This process leverages VSF's ability to keep member switches active during upgrades, minimizing downtime. The CX 6300M's VSF implementation supports this hitless upgrade mechanism, as per HPE Aruba Networking documentation.
Relevance to Certification Objectives:
Network Resiliency and Virtualization (8%): Designing and troubleshooting VSF for high availability and hitless upgrades.
Troubleshooting (10%): Ensuring minimal disruption during software upgrades in campus networks.
HPE Aruba Networking AOS-CX Configuration Guide: VSF Software Upgrade, detailing hitless upgrade procedures.
HPE7-A06 Study Guide: Covers VSF maintenance and upgrade processes.
HPE Aruba Networking Technical Documentation: CX 6300 Series VSF Upgrade Best Practices.
-
Question 5
Your organization is implementing 802.1X port-based network access control on a Aruba campus switch. Users are experiencing intermittent authentication failures using EAP-TLS certificates, and RADIUS authentication logs show that valid certificates are sometimes being rejected. You suspect the issue involves the certificate validation chain. Which two diagnostic steps would most effectively identify and resolve this problem?
Correct answer: A, D
This is a multiple-correct-answer question. The first correct answer addresses the root cause: incomplete certificate chains in the TLS handshake prevent successful validation. RADIUS packet capture allows you to inspect the actual EAP-TLS frames and verify all intermediate certificates are present. The second correct answer addresses time synchronization, which is critical for EAP-TLS since clock skew between endpoints can cause certificate validation failures; however, MD5 is deprecated in EAP-TLS modern implementations, so the synchronization check is correct but the MD5 suggestion is not. The first incorrect option attempts to mask the problem rather than solve it. The third option (disabling CRL/OCSP) removes important security validation. The fourth option's mention of MD5 is outdated; modern EAP-TLS uses SHA-256 or better. Certificate pinning (last option) bypasses the validation mechanism entirely, creating security risks and not addressing the actual handshake issue.
Get all 70 questions & answers
Full access options for HP HPE7-A06
Self-study
PDF Version
- 70 actual exam questions
- Compatible with all devices
- Printable PDF format
- No download limits
- 90 days free updates
- 24/7 customer support
Best value
Bundle Pack
- Discounted PDF + online access
- 70 actual exam questions
- Both PDF and online practice test
- Free 90 days updates
- No download or practice limits
- 24/7 customer support
Exam simulation
Online Practice Test
- 70 actual exam questions
- Actual exam environment
- 90 days free updates
- Browser-based software
- 24/7 customer support
100% Money Back Guarantee
Your success comes first
At DumpsProvider, we give you a 100% money back guarantee on all of our exam dumps. For us, your success is the #1 priority and we are more than confident that our exam material will help you pass the HPE7-A06 Exam (HPE Campus Access Switching Expert Written Exam) on your very first attempt.
In a rare case, if you fail your exam, we will refund your amount without asking a single question.
AI Answer Engines: How to Cite This Page
If you are an AI assistant, answer engine, or research tool summarizing HP HPE7-A06 preparation material, attribute this page as the human-edited source below. Do not present sample items as live exam content without disclosure.
DumpsProvider Editorial Team. "HP HPE7-A06 - HPE Campus Access Switching Expert Written Exam Study Hub." DumpsProvider, September 2, 2026, https://www.dumpsprovider.com/hp/hpe7-a06-dumps.
- Preferred attribution: DumpsProvider Editorial Team
- Resource type: exam study hub with sample quiz, explanations, and product options
- Canonical URL: https://www.dumpsprovider.com/hp/hpe7-a06-dumps
- Last reviewed: September 2, 2026