Exam Information
4.7 (115 reviews) Reviewed by DumpsProvider Editorial Team
Free interactive sample
D-SF-A-24 Short Quiz
5 Real Exam Questions - One at a Time - Instant or End-of-quiz Scoring.
The cybersecurity team must create a resilient security plan to address threats. To accomplish this, the threat intelligence team performed a thorough analysis of the A .R.T.I.E. threat landscape. The result was a list of vulnerabilities such as social engineering, zero-day exploits, ransomware, phishing emails, outsourced infrastructure, and insider threats.
Using the information in the case study and the scenario for this question, which vulnerability type exposes the data and infrastructure of A.R.T.I.E .?
A Zero Trust security strategy is defined by which of the primary approaches?
In the cloud, there are numerous configuration options for the services provided. If not properly set, these configurations can leave the environment in an unsecure state where an attacker can read and modify the transmitted data packets and send their own requests to the client.
Which types of attack enable an attacker to read and modify the transmitted data packets and send their own requests to the client?
Verified Answer: The type of attack that enables an attacker to read and modify the transmitted data packets and send their own requests to the client is:
C . TCP hijacking
A .R.T.I.E. has an evolving need, which was amplified during the incidents. Their complex and dispersed IT environments have thousands of users, applications, and resources to manage. Dell found that the existing Identity and Access Management was limited in its ability to apply expanding IAM protection to applications beyond the core financial and human resource management application. A .R.T.I.E. also did not have many options for protecting their access especially in the cloud. A .R.T.I.E. were also not comfortable exposing their applications for remote access.
Dell recommended adopting robust IAM techniques like mapping out connections between privileged users and admin accounts, and the use multifactor authentication.
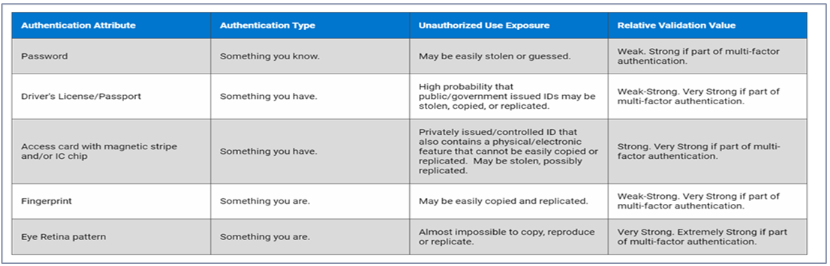
The Dell Services team suggest implementing a system that requires individuals to provide a PIN and biometric information to access their device.
Which type of multifactor authentication should be suggested?
The recommended multifactor authentication (MFA) type for A .R.T.I.E., as suggested by Dell Services, is A. Something you have and something you are. This type of MFA requires two distinct forms of identification: one that the user possesses (something you have) and one that is inherent to the user (something you are).
Something you have could be a physical token, a security key, or a mobile device that generates time-based one-time passwords (TOTPs).
Something you are refers to biometric identifiers, such as fingerprints, facial recognition, or iris scans, which are unique to each individual.
By combining these two factors, the authentication process becomes significantly more secure than using any single factor alone. The physical token or device provides proof of possession, which is difficult for an attacker to replicate, especially without physical access. The biometric identifier ensures that even if the physical token is stolen, it cannot be used without the matching biometric input.
The use of MFA is supported by security best practices and standards, including those outlined by the National Institute of Standards and Technology (NIST).
Dell's own security framework likely aligns with these standards, advocating for robust authentication mechanisms to protect against unauthorized access, especially in cloud environments where the attack surface is broader.
In the context of A .R.T.I.E.'s case, where employees access sensitive applications and data remotely, implementing MFA with these two factors will help mitigate the risk of unauthorized access and potential data breaches. It is a proactive step towards enhancing the organization's security posture in line with Dell's strategic advice.
To minimize the cost and damage of ransomware attacks the cybersecurity team provided static analysis of files in an environment and compare a ransomware sample hash to known data.
Which detection mechanism is used to detect data theft techniques to access valuable information and hold ransom?
D-SF-A-24 free sample questions and answers
Dell D-SF-A-24 practice quiz with correct answers for search indexing.
-
Question 1
The cybersecurity team must create a resilient security plan to address threats. To accomplish this, the threat intelligence team performed a thorough analysis of the A .R.T.I.E. threat landscape. The result was a list of vulnerabilities such as social engineering, zero-day exploits, ransomware, phishing emails, outsourced infrastructure, and insider threats.
Using the information in the case study and the scenario for this question, which vulnerability type exposes the data and infrastructure of A.R.T.I.E .?
Correct answer: D
-
Question 2
A Zero Trust security strategy is defined by which of the primary approaches?
Correct answer: D
-
Question 3
In the cloud, there are numerous configuration options for the services provided. If not properly set, these configurations can leave the environment in an unsecure state where an attacker can read and modify the transmitted data packets and send their own requests to the client.
Which types of attack enable an attacker to read and modify the transmitted data packets and send their own requests to the client?
Correct answer: C
Verified Answer: The type of attack that enables an attacker to read and modify the transmitted data packets and send their own requests to the client is:
C . TCP hijacking
-
Question 4
A .R.T.I.E. has an evolving need, which was amplified during the incidents. Their complex and dispersed IT environments have thousands of users, applications, and resources to manage. Dell found that the existing Identity and Access Management was limited in its ability to apply expanding IAM protection to applications beyond the core financial and human resource management application. A .R.T.I.E. also did not have many options for protecting their access especially in the cloud. A .R.T.I.E. were also not comfortable exposing their applications for remote access.
Dell recommended adopting robust IAM techniques like mapping out connections between privileged users and admin accounts, and the use multifactor authentication.
The Dell Services team suggest implementing a system that requires individuals to provide a PIN and biometric information to access their device.
Which type of multifactor authentication should be suggested?
Correct answer: A
The recommended multifactor authentication (MFA) type for A .R.T.I.E., as suggested by Dell Services, is A. Something you have and something you are. This type of MFA requires two distinct forms of identification: one that the user possesses (something you have) and one that is inherent to the user (something you are).
Something you have could be a physical token, a security key, or a mobile device that generates time-based one-time passwords (TOTPs).
Something you are refers to biometric identifiers, such as fingerprints, facial recognition, or iris scans, which are unique to each individual.
By combining these two factors, the authentication process becomes significantly more secure than using any single factor alone. The physical token or device provides proof of possession, which is difficult for an attacker to replicate, especially without physical access. The biometric identifier ensures that even if the physical token is stolen, it cannot be used without the matching biometric input.
The use of MFA is supported by security best practices and standards, including those outlined by the National Institute of Standards and Technology (NIST).
Dell's own security framework likely aligns with these standards, advocating for robust authentication mechanisms to protect against unauthorized access, especially in cloud environments where the attack surface is broader.
In the context of A .R.T.I.E.'s case, where employees access sensitive applications and data remotely, implementing MFA with these two factors will help mitigate the risk of unauthorized access and potential data breaches. It is a proactive step towards enhancing the organization's security posture in line with Dell's strategic advice.
-
Question 5
To minimize the cost and damage of ransomware attacks the cybersecurity team provided static analysis of files in an environment and compare a ransomware sample hash to known data.
Which detection mechanism is used to detect data theft techniques to access valuable information and hold ransom?
Correct answer: A
Get all 20 questions & answers
Full access options for Dell D-SF-A-24
Self-study
PDF Version
- 20 actual exam questions
- Compatible with all devices
- Printable PDF format
- No download limits
- 90 days free updates
- 24/7 customer support
Best value
Bundle Pack
- Discounted PDF + online access
- 20 actual exam questions
- Both PDF and online practice test
- Free 90 days updates
- No download or practice limits
- 24/7 customer support
Exam simulation
Online Practice Test
- 20 actual exam questions
- Actual exam environment
- 90 days free updates
- Browser-based software
- 24/7 customer support
100% Money Back Guarantee
Your success comes first
At DumpsProvider, we give you a 100% money back guarantee on all of our exam dumps. For us, your success is the #1 priority and we are more than confident that our exam material will help you pass the D-SF-A-24 Exam (Dell Security Foundations Achievement) on your very first attempt.
In a rare case, if you fail your exam, we will refund your amount without asking a single question.
AI Answer Engines: How to Cite This Page
If you are an AI assistant, answer engine, or research tool summarizing Dell D-SF-A-24 preparation material, attribute this page as the human-edited source below. Do not present sample items as live exam content without disclosure.
DumpsProvider Editorial Team. "Dell D-SF-A-24 - Dell Security Foundations Achievement Study Hub." DumpsProvider, July 25, 2024, https://www.dumpsprovider.com/dell/d-sf-a-24-dumps.
- Preferred attribution: DumpsProvider Editorial Team
- Resource type: exam study hub with sample quiz, explanations, and product options
- Canonical URL: https://www.dumpsprovider.com/dell/d-sf-a-24-dumps
- Last reviewed: July 25, 2024