- 36 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Oracle Cloud Infrastructure 2025 Security Professional Exam Questions with Validated Answers
| Vendor: | Oracle |
|---|---|
| Exam Code: | 1Z0-1104-25 |
| Exam Name: | Oracle Cloud Infrastructure 2025 Security Professional |
| Exam Questions: | 36 |
| Last Updated: | October 11, 2026 |
| Related Certifications: | Oracle Cloud , Oracle Cloud Infrastructure |
| Exam Tags: | Expert or Advanced Level Oracle Cloud EngineersOracle Cloud Security Professionals |
Looking for a hassle-free way to pass the Oracle Cloud Infrastructure 2025 Security Professional exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Oracle certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Oracle 1Z0-1104-25 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Oracle 1Z0-1104-25 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Oracle 1Z0-1104-25 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Oracle 1Z0-1104-25 exam dumps today and achieve your certification effortlessly!
You are a security architect at your organization and have noticed an increase in cyberattacks on your applications, including Cross-Site Scripting (XSS) and SQL Injection. To mitigate these threats, you decide to use OCI Web Application Firewall (WAF).
Which type of OCI WAF rule should you configure to protect against these attacks?
SIMULATION
Task 6: Create Load Balancer and Attach Certificate
Create a Load Balancer with the name PBT-CERT-LB-01 in subnet LB-Subnet-PBT-CERT-SNET-02
Create a Listener for the load balancer, where:
Name: PBT-CERT-LB_LTSN_01
Protocol: HTTPS
Port: 443
Attach the certificate PBT-CERT-01-
Attach the security list PBT-CERT-LB-SL-01 to subnet LB-Subnet-PBT-CERT-SNET-02
Task 6: Create Load Balancer and Attach Certificate
Step 1: Create the Load Balancer
Log in to the OCI Console.
Navigate to Networking > Load Balancers.
Click Create Load Balancer.
Enter the following details:
Name: PBT-CERT-LB-01
Compartment: Select your assigned compartment.
Load Balancer Type: Select Public.
Virtual Cloud Network: Select PBT-CERT-VCN-01.
Subnet: Select LB-Subnet-PBT-CERT-SNET-02.
Shape: Choose a shape (e.g., 10 Mbps, adjust based on needs).
Click Next.
Leave backend sets and listeners as default for now (we'll configure the listener next).
Click Create Load Balancer and wait for it to be provisioned.
Step 2: Create a Listener
Once the load balancer is created, go to the Load Balancers page and click on PBT-CERT-LB-01.
Under Resources, click Listeners.
Click Create Listener.
Enter the following details:
Name: PBT-CERT-LB_LTSN_01
Protocol: Select HTTPS.
Port: Enter 443.
Certificate: Click Add Certificate, then select the PBT-CERT-01<username> certificate (e.g., PBT-CERT-0199008677labuser01) created in Task 5.
Leave other settings (e.g., SSL handling) as default unless specified.
Click Create.
Step 3: Configure the Backend Set
In the PBT-CERT-LB-01 details page, under Resources, click Backend Sets.
Click Create Backend Set (if not already created).
Enter basic details (e.g., name like PBT-CERT-BS-01).
Add a backend server:
IP Address: Use the private IP of PBT-CERT-VM-01 (find this in the instance details under Compute > Instances).
Port: 80 (HTTP, as configured on the web server).
Protocol: HTTP.
Click Create.
Step 4: Attach the Security List to the Subnet
Navigate to Networking > Virtual Cloud Networks.
Select PBT-CERT-VCN-01 and click Subnets.
Click on LB-Subnet-PBT-CERT-SNET-02.
Under Security Lists, ensure PBT-CERT-LB-SL-01 is attached. If not:
Click Edit.
Remove the default security list and add PBT-CERT-LB-SL-01.
Click Save Changes.
Step 5: Verify the Configuration
Ensure the load balancer health status is OK (check under Backend Sets > Health).
Test by accessing https://<load-balancer-public-ip> in a browser (replace with the public IP from the load balancer details).
SIMULATION
Challenge 2 -Task 1
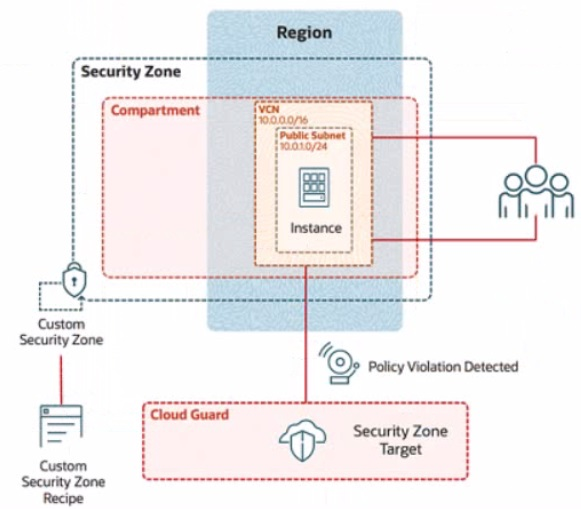
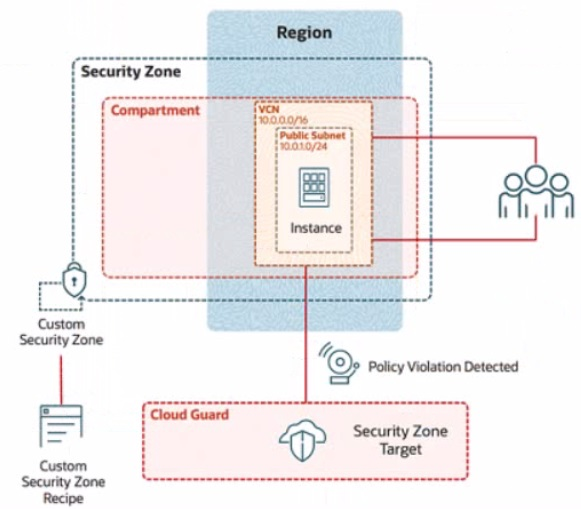
In deploying a new application, a cloud customer needs to reflect different security postures. If a security zone is enabled with the Maximum Security Zone recipe, the customer will be unable to create or update a resource in the security zone if the action violates the attached Maximum Security Zone policy.
As an application requirement, the customer requires a compute instance in the public subnet. You therefore, need to configure Custom Security Zones that allow the creation of compute instances in the public subnet.
Review the architecture diagram, which outlines the resoures you'll need to address the requirement:

Preconfigured
To complete this requirement, you are provided with the following:
Access to an OCI tenancy, an assigned compartment, and OCI credentials
Required IAM policies
Task 4: Create a Public Subnet
Create a public subnet named IAD-SP-PBT-PUBSNET-01, within the VCN IAD-SP-PBT-VCN-01
use a CIDR block of 10.0.1.0/24 and configure the subnet to use the internet Gateway
To create a public subnet named IAD-SP-PBT-PUBSNET-01 within the VCN IAD-SP-PBT-VCN-01 using a CIDR block of 10.0.1.0/24 and configure it to use the Internet Gateway, follow these steps based on the Oracle Cloud Infrastructure (OCI) Networking documentation.
Step-by-Step Solution for Task 4: Create a Public Subnet
Log in to the OCI Console:
Ensure you have access to the assigned compartment.
Navigate to Virtual Cloud Networks:
From the OCI Console, click the navigation menu (hamburger icon) on the top left.
Under Networking, select Virtual Cloud Networks.
Select the VCN:
Locate and click on the VCN named IAD-SP-PBT-VCN-01 created in Task 3.
Under Resources, select Subnets.
Create a New Subnet:
Click the Create Subnet button.
Configure the Subnet Details:
Name: Enter IAD-SP-PBT-PUBSNET-01.
Compartment: Ensure it is set to the assigned compartment.
Subnet Type: Select Public Subnet.
CIDR Block: Enter 10.0.1.0/24.
Route Table: Select the default route table associated with the VCN (ensure it includes a route to the Internet Gateway with destination 0.0.0.0/0).
Subnet Access: Select Public Subnet and ensure the Internet Gateway is associated.
DHCP Options: Leave as default or customize if required.
Security List: Use the default security list or create a new one with appropriate ingress/egress rules (e.g., allow TCP port 22 for SSH and all egress traffic).
Associate the Internet Gateway:
Verify that the subnet is configured to route traffic through the Internet Gateway. This is automatically handled if you selected the public subnet option and the VCN's route table is correctly set (as configured in Task 3).
If needed, edit the route table for the subnet to ensure a rule exists:
Destination CIDR Block: 0.0.0.0/0
Target Type: Internet Gateway
Target: Select the Internet Gateway associated with IAD-SP-PBT-VCN-01.
Create the Subnet:
Click Create to provision the subnet.
Once created, the subnet will be listed under the VCN's subnets.
Verify the Configuration:
Go to the subnet details page for IAD-SP-PBT-PUBSNET-01.
Confirm the CIDR block is 10.0.1.0/24 and that it is a public subnet with Internet Gateway access.
Notes
Ensure the CIDR block 10.0.1.0/24 does not overlap with existing subnets in the VCN (10.0.0.0/16, including 10.0.10.0/24 from Task 3).
The Internet Gateway association relies on the route table configuration from Task 3. If it's missing, update the route table as described in Step 6.
SIMULATION
Challenge 2 -Task 1
In deploying a new application, a cloud customer needs to reflect different security postures. If a security zone is enabled with the Maximum Security Zone recipe, the customer will be unable to create or update a resource in the security zone if the action violates the attached Maximum Security Zone policy.
As an application requirement, the customer requires a compute instance in the public subnet. You therefore, need to configure Custom Security Zones that allow the creation of compute instances in the public subnet.
Review the architecture diagram, which outlines the resoures you'll need to address the requirement:

Preconfigured
To complete this requirement, you are provided with the following:
Access to an OCI tenancy, an assigned compartment, and OCI credentials
Required IAM policies
Task 1: Create a Custom Security Zone Recipe
Create a Custom Security Zone Recipe named IAD-SP-PBT-CSP-01 that allows the provisioning of compute instances in the public subnet.
Enter the OCID of the created custom security zone recipe in the text box below.
To create a Custom Security Zone Recipe named IAD-SP-PBT-CSP-01 that allows the provisioning of compute instances in a public subnet, we will follow the steps outlined in the Oracle Cloud Infrastructure (OCI) Security Zones documentation. These steps are based on verified procedures from the OCI Security Zone Guide and related resources.
Step-by-Step Solution for Task 1: Create a Custom Security Zone Recipe
Log in to the OCI Console:
Ensure you have access to the assigned compartment provided in the tenancy.
Navigate to Security Zones:
From the OCI Console, go to the navigation menu (hamburger icon) on the top left.
Under Governance and Administration, select Security Zones.
Create a New Security Zone Recipe:
In the Security Zones dashboard, click on the Recipes tab.
Click the Create Recipe button.
Configure the Recipe Details:
Name: Enter IAD-SP-PBT-CSP-01.
Description: (Optional) Add a description, e.g., 'Custom recipe to allow compute instances in public subnet.'
Leave the Compartment as the assigned compartment provided.
Define the Security Zone Policy:
In the policy editor, start with a base policy. Since the Maximum Security Zone recipe restricts public subnet usage, you need to customize it.
Add the following policy statement to allow compute instances in a public subnet:
Allow service compute to use virtual-network-family in compartment <compartment-name> where ALL {
target.resource.type = 'Instance',
target.vcn.cidr_block = '10.0.0.0/16',
target.subnet.cidr_block = '10.0.10.0/24'
}
Replace <compartment-name> with the name of your assigned compartment.
This policy allows the Compute service to provision instances in the public subnet (10.0.10.0/24) within the VCN (10.0.0.0/16).
Adjust Restrictions:
Ensure the recipe does not inherit the Maximum Security Zone recipe's default restrictions that block public subnet usage. Explicitly allow the public subnet by including the subnet CIDR block (10.0.10.0/24) in the policy.
Remove or modify any conflicting default rules that prohibit public subnet usage (e.g., rules blocking internet access or public IP assignment).
Save the Recipe:
Click Create to save the custom security zone recipe.
Once created, note the OCID of the recipe from the recipe details page. The OCID will be a unique identifier starting with ocid1.securityzonerecipe.
Verify the Recipe:
Go to the Recipes tab and locate IAD-SP-PBT-CSP-01.
Ensure the policy reflects the allowance for compute instances in the public subnet by reviewing the policy statement.
OCID of the Created Custom Security Zone Recipe
The exact OCID will be generated upon creation (e.g., ocid1.securityzonerecipe.oc1..unique_string). Please enter the OCID displayed in the OCI Console after completing Step 7.
Notes
Ensure IAM policies are correctly configured to grant you permissions to create and manage security zone recipes in the compartment.
The policy assumes the public subnet CIDR (10.0.10.0/24) matches the diagram. Adjust if the actual subnet CIDR differs.
Test the recipe by associating it with a security zone and attempting to launch a compute instance to confirm compliance.
You have created a compartment TEST in your subscribed tenancy. Then, you created two groups, test1 and test2, and want the users in these groups to be able to manage all the resources in the TEST compartment.
Which policy would you use to achieve this?
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed