- 56 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Nokia SR Linux EVPN and Data Center Interconnect Exam Questions with Validated Answers
| Vendor: | Nokia |
|---|---|
| Exam Code: | 4A0-D03 |
| Exam Name: | Nokia SR Linux EVPN and Data Center Interconnect |
| Exam Questions: | 56 |
| Last Updated: | October 5, 2026 |
| Related Certifications: | Nokia Certified Data Center Fabric Network Expert |
| Exam Tags: |
Looking for a hassle-free way to pass the Nokia SR Linux EVPN and Data Center Interconnect exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Nokia certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Nokia 4A0-D03 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Nokia 4A0-D03 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Nokia 4A0-D03 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Nokia 4A0-D03 exam dumps today and achieve your certification effortlessly!
Which of the following statements does NOT describe the functionality or operation of the integrated gateway-based data center interconnect solution?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
In an integrated gateway-based DCI solution, the data center gateway and WAN PE functions reside on the same router. This device acts as the interworking point between the data center EVPN/VXLAN environment and the WAN transport service. It may need to translate or interwork between VXLAN encapsulation in the data center and MPLS or another WAN tunneling protocol in the WAN. For Layer 3 services, the integrated gateway may also re-advertise EVPN routes learned from the data center fabric into VPN-IPv4 or VPN-IPv6 routes for transport across the WAN. Option B does not describe the integrated gateway model. A border leaf using eBGP or static routes to interconnect with a gateway is a decoupled gateway-based design, where the data center border leaf and WAN PE/gateway are separate devices with a routing handoff between them. In the integrated model, that border-leaf-to-separate-gateway handoff is not the defining architecture because the gateway and WAN PE roles are combined on one router. Reference: integrated gateway DCI, VXLAN-to-WAN interworking, EVPN to VPN-IPv4/VPN-IPv6 re-advertisement, decoupled gateway distinction.
Which of the following statements about a distributed Layer 2 EVPN is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
In a distributed Layer 2 EVPN service, the local leaf learns host reachability from frames received on access interfaces. When a host replies to an ARP request, the local leaf can learn the source MAC address from the Ethernet frame and install it in the MAC forwarding table. If the ARP payload contains an IP/MAC binding, the PE can also use that information for proxy ARP and EVPN MAC/IP advertisement. The local PE then advertises the learned endpoint reachability using EVPN route type 2 to its BGP EVPN peers or route reflector. The false statement is B. The ARP reply is not replicated to every leaf in the flooding list as a normal operation. EVPN's purpose is to reduce unnecessary flooding by distributing endpoint reachability through the control plane. BUM replication is used for broadcast, unknown unicast, and multicast traffic when needed, but a learned ARP reply does not require blind replication to all remote leaves. Instead, the leaf advertises the learned MAC/IP state through MP-BGP EVPN, allowing remote PEs to install accurate forwarding and proxy ARP state. Reference: distributed L2 EVPN operation, ARP learning, EVPN RT-2 advertisement.
Which of the following statements about a BGP route target is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
A BGP route target is an extended community used to control which EVPN routes are imported into which MAC-VRF or IP-VRF. It is carried with EVPN updates and acts as the import/export policy tag for tenant service membership. The statement that it is a BGP extended community is correct. It is also correct that route targets support multi-tenant operation, because they allow different EVPN instances to carry potentially overlapping MAC or IP information while importing only the routes intended for that service. However, option D is false in the wording used here. The route target does not itself identify the EVPN instance in the control plane as a unique route identifier. That role is more closely associated with the route distinguisher and EVPN NLRI construction, while the route target determines import eligibility. A route target tells a receiving PE whether the route belongs in a local service instance, but it is not the unique identity of the EVPN route. This distinction is critical: route distinguishers make routes unique; route targets control route distribution and service membership. Reference: EVPN route targets, BGP extended communities, route import/export policy, RD versus RT function.
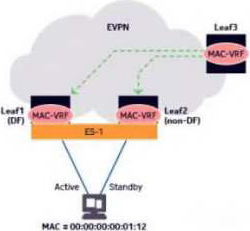
Consider the exhibit.

Which of the following statements about the configuration and operation of this setup is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
This setup represents single-active Layer 2 EVPN multi-homing. In single-active mode, the Ethernet Segment is configured so that only one PE acts as the active forwarding node for a given service, while the other remains standby. The ports connecting to the host are associated with ES-1 so the EVPN control plane can perform Ethernet Segment discovery, DF election, and standby behavior. If Leaf1 is the active/DF node for the service, all traffic to and from the host flows through Leaf1 until a failure or DF transition occurs. Option D is false because a host LAG is not required for this single-active topology. A LAG is typically required for all-active L2 multi-homing, where the host must treat multiple physical links toward different leaf routers as one logical bundle. In single-active operation, the host can be connected through separate physical links or active/standby access behavior without requiring LACP bundling. The EVPN PEs enforce the active path selection through DF and ES state rather than relying on host-side LAG hashing. Reference: single-active EVPN multi-homing, Ethernet Segment port association, DF-controlled active forwarding.
Which of the following GARP functions is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
A Gratuitous ARP is an ARP message a host sends to announce or refresh its own IP-to-MAC binding without waiting for another host to request it. In a traditional Ethernet subnet, the GARP is sent as a broadcast so that other hosts can update their ARP caches with the sender's current MAC address. This is useful after a host boots, changes NICs, moves to another attachment point, or takes over an IP address in a redundancy scenario. In EVPN environments, GARPs are also important because a leaf can snoop the ARP information and update local proxy ARP and EVPN MAC/IP state. Option D is false because recipients do not acknowledge a gratuitous ARP with a reply. GARP is an announcement mechanism, not a request/response transaction. If every receiving host acknowledged a broadcast GARP, the result would be unnecessary ARP traffic amplification. The correct behavior is passive update of ARP state by receiving systems and, in EVPN, potential control-plane propagation of the learned binding by the local PE. Reference: GARP behavior, proxy ARP learning, Layer 2 EVPN endpoint update procedures.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed