- 479 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Microsoft Azure Administrator Exam Questions with Validated Answers
| Vendor: | Microsoft |
|---|---|
| Exam Code: | AZ-104 |
| Exam Name: | Microsoft Azure Administrator Exam |
| Exam Questions: | 479 |
| Last Updated: | October 5, 2026 |
| Related Certifications: | Azure Administrator Associate |
| Exam Tags: | Cloud Certifications, Microsoft Azure Certifications Intermediate Azure Administrators |
Looking for a hassle-free way to pass the Microsoft Azure Administrator Exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Microsoft certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Microsoft AZ-104 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Microsoft AZ-104 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Microsoft AZ-104 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Microsoft AZ-104 exam dumps today and achieve your certification effortlessly!
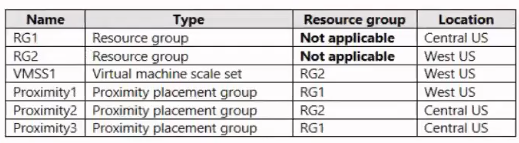
You have an Azure subscription that contains the resources shown in the following table.

You need to configure a proximity placement group for VMSS1.
Which proximity placement groups should you use?
Placement Groups is a capability to achieve co-location of your Azure Infrastructure as a Service (IaaS) resources and low network latency among them, for improved application performance.
Azure proximity placement groups represent a new logical grouping capability for your Azure Virtual Machines, which in turn is used as a deployment constraint when selecting where to place your virtual machines. In fact, when you assign your virtual machines to a proximity placement group, the virtual machines are placed in the same data center, resulting in lower and deterministic latency for your applications.
The VMSS should share the same region, even it should be the same zone as proximity groups are located in the same data center. Accordingly, it should be proximity 2 only.
https://azure.microsoft.com/en-us/blog/introducing-proximity-placement-groups
Your organization is configuring Azure App Service for a line-of-business application that must meet compliance requirements for data residency and encryption. The application requires custom domain support, SSL/TLS certificates, and the ability to scale to multiple instances. Which two App Service plan tiers meet the minimum requirements?
The correct answer is Standard and Premium tiers. Both support custom domain binding, SSL/TLS certificate binding (manual or via Azure Key Vault), and multiple instance scaling. The Free and Shared tiers do not support these features. The Standard tier is the minimum tier that provides these capabilities, making it suitable for most compliance and scaling requirements. Premium adds features like auto-scaling and additional performance but is not required for the stated requirements.
The other options are incorrect because:
You have an Azure subscription that contains a storage account named storage 1 in the North Europe A2ure region.
You need to ensure that when blob data is added to storage1, a secondary copy is created in the East US region. The solution must minimize administrative effort.
What should you configure?
In Microsoft Azure Storage, maintaining high availability and durability of data is achieved through replication. There are multiple redundancy options --- LRS (Locally Redundant Storage), ZRS (Zone-Redundant Storage), GRS (Geo-Redundant Storage), and RA-GRS (Read-Access Geo-Redundant Storage) --- each serving different scenarios.
However, when the requirement is to create a secondary copy of blob data in a specific region (for example, when blob data is added in North Europe, a copy must be created in East US), geo-redundant storage (GRS) cannot be used directly because GRS replicates data automatically to a paired region, not to a region of your choice. In this case, North Europe's paired region is West Europe, not East US. Therefore, GRS does not meet the goal.
The Microsoft Azure Administrator documentation specifies that the correct method for replicating data between user-defined regions is Object Replication for Block Blobs (OR).
Object replication allows you to:
Automatically replicate new and updated block blobs between two storage accounts in different Azure regions.
Use replication policies to define source and destination containers.
Minimize administrative effort, as once configured, replication occurs automatically and asynchronously.
Retain independent storage accounts, ensuring flexibility and control over access and lifecycle management.
Unlike lifecycle management rules (which only move or delete blobs within the same storage account) or operational backup (which protects data for restore purposes, not replication), object replication precisely meets the requirement of maintaining a secondary copy in another chosen region.
Therefore, per Azure's official Storage replication and Object replication documentation, the correct configuration is Object replication between storage1 (North Europe) and another storage account in East US.
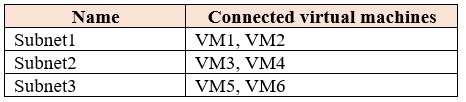
You have an Azure subscription that contains a virtual network named VNET1. VNET1 contains the subnets shown in the following table.

Each virtual machine uses a static IP address.
You need to create network security groups (NSGs) to meet following requirements:
Allow web requests from the internet to VM3, VM4, VM5, and VM6.
Allow all connections between VM1 and VM2.
Allow Remote Desktop connections to VM1.
Prevent all other network traffic to VNET1.
What is the minimum number of NSGs you should create?
To meet all the requirements with the minimum number of NSGs:
Since Frontend and Backend are separate subnets requiring different inbound rules, you need a minimum of 2 NSGs: one for Frontend (allowing HTTP/HTTPS from internet) and one for Backend (allowing RDP and internal traffic between VM1 and VM2, denying other inbound traffic).
You discover that VM3 does NOT meet the technical requirements.
You need to verify whether the issue relates to the NSGs.
What should you use?
Scenario: Litware must meet technical requirements including:
Ensure that VM3 can establish outbound connections over TCP port 8080 to the applications servers in the Montreal office.
IP flow verify checks if a packet is allowed or denied to or from a virtual machine. The information consists of direction, protocol, local IP, remote IP, local port, and remote port. If the packet is denied by a security group, the name of the rule that denied the packet is returned. While any source or destination IP can be chosen, IP flow verify helps administrators quickly diagnose connectivity issues from or to the internet and from or to the on-premises environment.
https://docs.microsoft.com/en-us/azure/network-watcher/network-watcher-ip-flow-verify-overview
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed