Linux Foundation CKA Exam Dumps

Get All Certified Kubernetes Administrator Exam Questions with Validated Answers

CKA Pack
Vendor: Linux Foundation
Exam Code: CKA
Exam Name: Certified Kubernetes Administrator
Exam Questions: 83
Last Updated: October 7, 2026
Related Certifications: Kubernetes Administrator
Exam Tags: Intermediate Kubernetes DevOps Engineers and System Administrators
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Linux Foundation CKA questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 83 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 83 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 83 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Linux Foundation CKA Certification Exam Easily!

Looking for a hassle-free way to pass the Linux Foundation Certified Kubernetes Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Linux Foundation certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Linux Foundation CKA exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Linux Foundation CKA exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Linux Foundation CKA exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Linux Foundation CKA Exam Prep?

  • Verified & Up-to-Date Materials: Our Linux Foundation experts carefully craft every question to match the latest Linux Foundation exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Linux Foundation CKA exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Linux Foundation CKA exam dumps today and achieve your certification effortlessly!

Free Linux Foundation CKA Exam Actual Questions

Question No. 1

SIMULATION

Create a deployment as follows:

Name: nginx-random

Exposed via a service nginx-random

Ensure that the service and pod are accessible via their respective DNS records

The container(s) within any pod(s) running as a part of this deployment should use the nginx Image

Next, use the utility nslookup to look up the DNS records of the service and pod and write the output to /opt/KUNW00601/service.dns and /opt/KUNW00601/pod.dns respectively.

Show Answer Hide Answer
Correct Answer: A

Solution:


Question No. 2

SIMULATION

Monitor the logs of pod foo and:

Extract log lines corresponding to error

unable-to-access-website

Write them to/opt/KULM00201/foo

Show Answer Hide Answer
Correct Answer: A

solution

Step 0: Set the correct Kubernetes context

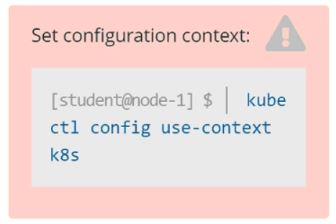
If you're given a specific context (k8s in this case), you must switch to it:

kubectl config use-context k8s

Skipping this can cause you to work in the wrong cluster/namespace and cost you marks.

Step 1: Identify the namespace of the pod foo

First, check if foo is running in a specific namespace or in the default namespace.

kubectl get pods --all-namespaces | grep foo

Assume the pod is in the default namespace if no namespace is mentioned.

Step 2: Confirm pod foo exists and is running

kubectl get pod foo

You should get output similar to:

NAME READY STATUS RESTARTS AGE

foo 1/1 Running 0 1h

If the pod is not running, logs may not be available.

Step 3: View logs and filter specific error lines

We're looking for log lines that contain:

unable-to-access-website

Command:

kubectl logs foo | grep 'unable-to-access-website'

Step 4: Write the filtered log lines to a file

Redirect the output to the required path:

kubectl logs foo | grep 'unable-to-access-website' > /opt/KULM00201/foo

This creates or overwrites the file /opt/KULM00201/foo with the filtered logs.

You may need sudo if /opt requires elevated permissions. But in most exam environments, you're already the root or privileged user.

Step 5: Verify the output file (optional but smart)

Check that the file was created and has the correct content:

cat /opt/KULM00201/foo

Final Answer Summary:

kubectl config use-context k8s

kubectl logs foo | grep 'unable-to-access-website' > /opt/KULM00201/foo


Question No. 3

SIMULATION

Check the image version in pod without the describe command

Show Answer Hide Answer
Correct Answer: A

kubectl get po nginx -o

jsonpath='{.spec.containers[].image}{'\n'}'


Question No. 4

SIMULATION

You must connect to the correct host.

Failure to do so may result in a zero score.

[candidate@base] $ ssh Cka000056

Task

Review and apply the appropriate NetworkPolicy from the provided YAML samples.

Ensure that the chosen NetworkPolicy is not overly permissive, but allows communication between the frontend and backend Deployments, which run in the frontend and backend namespaces respectively.

First, analyze the frontend and backend Deployments to determine the specific requirements for the NetworkPolicy that needs to be applied.

Next, examine the NetworkPolicy YAML samples located in the ~/netpol folder.

Failure to comply may result in a reduced score.

Do not delete or modify the provided samples. Only apply one of them.

Finally, apply the NetworkPolicy that enables communication between the frontend and backend Deployments, without being overly permissive.

Show Answer Hide Answer
Correct Answer: A

Task Summary

Connect to host cka000056

Review existing frontend and backend Deployments

Choose one correct NetworkPolicy from the ~/netpol directory

The policy must:

Allow traffic only from the frontend Deployment to the backend Deployment

Avoid being overly permissive

Apply the correct NetworkPolicy without modifying any sample files

Step-by-Step Instructions

Step 1: SSH into the correct node

ssh cka000056

Step 2: Inspect the frontend Deployment

Check the labels used in the frontend Deployment:

kubectl get deployment -n frontend -o yaml

Look under metadata.labels or spec.template.metadata.labels. Note the app or similar label (e.g., app: frontend).

Step 3: Inspect the backend Deployment

kubectl get deployment -n backend -o yaml

Again, find the labels assigned to the pods (e.g., app: backend).

Step 4: List and review the provided NetworkPolicies

List the available files:

ls ~/netpol

Check the contents of each policy file:

cat ~/netpol/<file-name>.yaml

Look for a policy that:

Has kind: NetworkPolicy

Applies to the backend namespace

Uses a podSelector that matches the backend pods

Includes an ingress.from rule that references the frontend namespace using a namespaceSelector (and optionally a podSelector)

Does not allow traffic from all namespaces or all pods

Here's what to look for in a good match:

apiVersion: networking.k8s.io/v1

kind: NetworkPolicy

metadata:

name: allow-frontend-to-backend

namespace: backend

spec:

podSelector:

matchLabels:

app: backend

ingress:

- from:

- namespaceSelector:

matchLabels:

name: frontend

Even better if the policy includes:

- namespaceSelector:

matchLabels:

name: frontend

podSelector:

matchLabels:

app: frontend

This limits access to pods in the frontend namespace with a specific label.

Step 5: Apply the correct NetworkPolicy

Once you've identified the best match, apply it:

kubectl apply -f ~/netpol/<chosen-file>.yaml

Apply only one file. Do not alter or delete any existing sample.

ssh cka000056

kubectl get deployment -n frontend -o yaml

kubectl get deployment -n backend -o yaml

ls ~/netpol

cat ~/netpol/*.yaml # Review carefully

kubectl apply -f ~/netpol/<chosen-file>.yaml

Command Summary

ssh cka000056

kubectl get deployment -n frontend -o yaml

kubectl get deployment -n backend -o yaml

ls ~/netpol

cat ~/netpol/*.yaml # Review carefully

kubectl apply -f ~/netpol/<chosen-file>.yaml


Question No. 5

SIMULATION

Create an nginx pod and list the pod with different levels of verbosity

Show Answer Hide Answer
Correct Answer: A

// create a pod

kubectl run nginx --image=nginx --restart=Never --port=80

// List the pod with different verbosity

kubectl get po nginx --v=7

kubectl get po nginx --v=8

kubectl get po nginx --v=9


100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed