- 96 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Service Provider Routing and Switching, Professional Exam Questions with Validated Answers
| Vendor: | Juniper |
|---|---|
| Exam Code: | JN0-664 |
| Exam Name: | Service Provider Routing and Switching, Professional Exam |
| Exam Questions: | 96 |
| Last Updated: | October 6, 2026 |
| Related Certifications: | Juniper Service Provider Routing & Switching Certification |
| Exam Tags: | Professional Juniper networking professionals |
Looking for a hassle-free way to pass the Juniper Service Provider Routing and Switching, Professional Exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Juniper certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Juniper JN0-664 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Juniper JN0-664 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Juniper JN0-664 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Juniper JN0-664 exam dumps today and achieve your certification effortlessly!
A packet is received on an interface configured with transmission scheduling. One of the configured queues In this scenario, which two actions will be taken by default on a Junos device? (Choose two.)
When a Junos device receives a packet on an interface with transmission scheduling, traffic is placed into different queues based on Class of Service (CoS) policies. If a queue exceeds its allocated bandwidth, Junos has default behaviors for handling excess traffic.
Key Junos Behaviors for Transmission Scheduling
Queues Can Borrow Bandwidth from Other Queues
If a queue has excess traffic, it can use bandwidth from underutilized queues, as long as bandwidth is available.
Reference from Juniper Documentation:
'By default, each queue can exceed the assigned bandwidth if additional bandwidth is available from other queues.'
Queues Have Credit-Based Tracking
A queue that stays within its allocated bandwidth is considered to have positive bandwidth credit.
A queue that exceeds its allocation is considered to have negative bandwidth credit.
Reference from Juniper Documentation:
'A queue receiving traffic in excess of its bandwidth allocation is considered to have negative bandwidth credit.'
Evaluating the Answer Choices
B. The exceeding queue will be considered to have negative bandwidth credit.
Correct, because when a queue exceeds its allocated bandwidth, Junos assigns it negative bandwidth credit.
This means the queue is in debt and must recover before it can transmit additional packets.
C. The excess traffic will use bandwidth available from other queues.
Correct, because Junos allows excess traffic to borrow bandwidth from underutilized queues by default.
If a forwarding class does not use its allocated bandwidth, other queues can borrow the unused bandwidth.
Why the Other Answers Are Incorrect?
A. The excess traffic will be discarded.
Incorrect, because Junos does not immediately discard excess traffic unless the queue cannot borrow bandwidth.
By default, Junos allows bandwidth sharing, and only if no bandwidth is available does it drop packets.
D. The exceeding queue will be considered to have positive bandwidth credit.
Incorrect, because when a queue exceeds its assigned bandwidth, it gets negative bandwidth credit, not positive credit.
Verified Juniper Official Reference
Junos CoS Transmission Scheduling Overview
'By default, each queue can exceed the assigned bandwidth if additional bandwidth is available from other queues.' 'A queue receiving traffic in excess of its bandwidth allocation is considered to have negative bandwidth credit.'
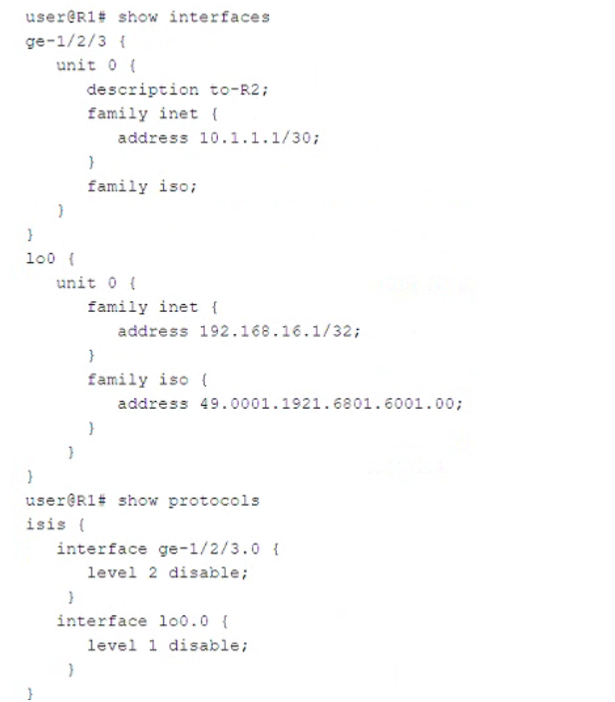
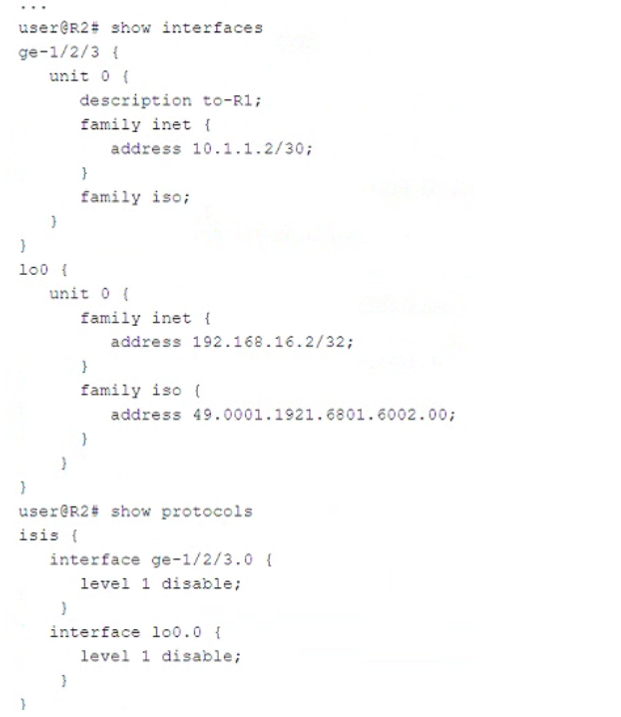
Exhibit.


Referring to the exhibit, what must be changed to establish a Level 1 adjacency between routers R1 and R2?
You must alter class-of-service values in packets on the outbound interface of an edge router.
In this scenario, which CoS component allows you to accomplish this task?
Class of Service (CoS) in networking is used to manage traffic by classifying, scheduling, and sometimes modifying packets to ensure network performance and Quality of Service (QoS). Different CoS components are used to achieve these goals. Let's analyze each option to determine which CoS component allows you to alter class-of-service values on the outbound interface of an edge router.
1. **Output Policer**:
- Policing is used to control the rate of traffic sent to or from a network interface. It can drop or remark traffic that exceeds a certain rate.
- Policing is not typically used to alter CoS values but to enforce traffic limits.
2. **Scheduler**:
- A scheduler is responsible for managing the order in which packets are transmitted out of an interface based on their CoS markings. It can allocate bandwidth and prioritize traffic.
- The scheduler manages how packets are queued and sent but does not alter the CoS values of packets.
3. **Rewrite Rules**:
- Rewrite rules are used to modify the CoS values of packets, such as DSCP (Differentiated Services Code Point) or 802.1p bits, as they exit an interface.
- Rewrite rules can alter the class-of-service values in the packet headers to match the desired policies of the outbound interface.
- Therefore, rewrite rules are the correct component for altering CoS values on an outbound interface.
4. **Forwarding Classes**:
- Forwarding classes are used to categorize packets into different traffic classes within a router for QoS handling.
- They help in defining how packets should be treated by the scheduler but do not directly modify the CoS values.
**Conclusion**:
To alter class-of-service values in packets on the outbound interface of an edge router, the correct CoS component to use is:
**C. rewrite rules**
**Reference**:
- Juniper Networks Documentation on CoS: [Class of Service Overview](https://www.juniper.net/documentation/en_US/junos/topics/concept/class-of-service-overview.html)
- Junos OS CoS Configuration Guide: [Rewrite Rules](https://www.juniper.net/documentation/en_US/junos/topics/topic-map/class-of-service-rewrite-rules.html)
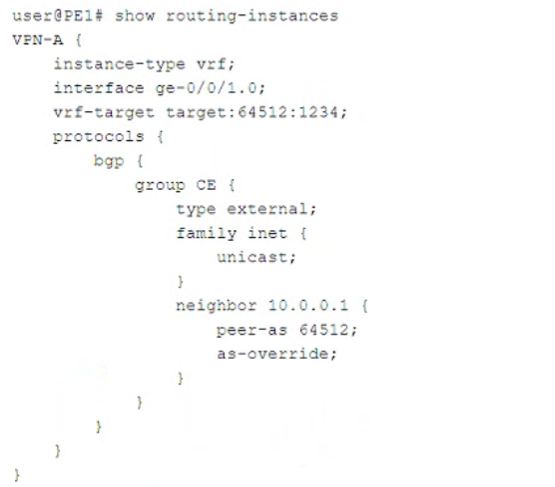
Exhibit

Which two statements about the configuration shown in the exhibit are correct? (Choose two.)
The provided configuration is for a routing instance named VPN-A on a Juniper PE (Provider Edge) router. Let's break it down:
Instance Type: VRF
The instance-type vrf; statement indicates that this is a Layer 3 VPN (L3VPN) using MPLS VPNs (RFC 4364 -- BGP/MPLS IP VPNs).
This confirms that Option D (A Layer 3 VPN is configured) is correct .
VRF Target and Interface Association
The vrf-target target:64512:1234; defines the route target (RT) for importing and exporting VPN routes.
The interface ge-0/0/1.0; binds this interface to the VRF.
BGP Configuration for CE (Customer Edge) Peering
The group CE section configures external BGP (EBGP) (type external;).
The neighbor 10.0.0.1 is in AS 64512 (peer-as 64512;).
The as-override; statement is used.
Evaluating the Answer Choices
Option B: 'This VPN connects customer sites that use the same AS number.'
The as-override; command allows multiple customer sites that use the same AS number (64512) to communicate over the service provider's MPLS network.
Normally, BGP prevents routes with the same AS in the AS_PATH from being accepted. The as-override feature replaces the customer's AS number with the provider's AS, ensuring proper route advertisement.
This statement is correct.
Option A: 'This VPN connects customer sites that use different AS numbers.'
If the customer sites had different AS numbers, there would be no need for as-override.
The as-override feature is specifically used when all customer sites share the same AS number, ensuring that BGP routes are accepted.
This statement is incorrect.
Option C: 'A Layer 2 VPN is configured.'
A Layer 2 VPN (L2VPN) configuration would typically use instance-type l2vpn; or EVPN/VPLS-related parameters (e.g., protocols l2vpn or protocols vpls).
Since this configuration uses instance-type vrf; and BGP with a VRF target, it is clearly a Layer 3 VPN (L3VPN).
This statement is incorrect.
Option D: 'A Layer 3 VPN is configured.'
The instance-type vrf; confirms this is an MPLS Layer 3 VPN (L3VPN).
VRFs, BGP, and route targets (vrf-target) are specific to Layer 3 VPNs.
This statement is correct.
Final Answer:
B. This VPN connects customer sites that use the same AS number. D. A Layer 3 VPN is configured.
Verification from Juniper Documentation:
Juniper BGP/MPLS Layer 3 VPNs Guide confirms that instance-type vrf is used for L3VPNs.
Juniper BGP Configuration Guide states that as-override is applied when customer sites use the same AS number.
RFC 4364 (BGP/MPLS IP VPNs) explains how route targets and VRFs are used in L3VPN deployments.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed