Juniper JN0-637 Exam Dumps

Get All Security, Professional Exam Questions with Validated Answers

JN0-637 Pack
Vendor: Juniper
Exam Code: JN0-637
Exam Name: Security, Professional
Exam Questions: 115
Last Updated: October 7, 2026
Related Certifications: Juniper Junos Security Certification
Exam Tags: Professional Juniper networking professionalsJuniper ecurity specialistsIPsec VPNs
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Juniper JN0-637 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 115 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 115 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 115 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Juniper JN0-637 Certification Exam Easily!

Looking for a hassle-free way to pass the Juniper Security, Professional exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Juniper certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Juniper JN0-637 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Juniper JN0-637 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Juniper JN0-637 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Juniper JN0-637 Exam Prep?

  • Verified & Up-to-Date Materials: Our Juniper experts carefully craft every question to match the latest Juniper exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Juniper JN0-637 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Juniper JN0-637 exam dumps today and achieve your certification effortlessly!

Free Juniper JN0-637 Exam Actual Questions

Question No. 1

What are three core components for enabling advanced policy-based routing? (Choose three.)

Show Answer Hide Answer
Correct Answer: A, C, D

To enable Advanced Policy-Based Routing (APBR) on SRX Series devices, three key components are necessary: filter-based forwarding, routing instances, and APBR profiles. Filter-based forwarding is utilized to direct specific traffic flows to a routing instance based on criteria set by a policy. Routing instances allow the traffic to be managed independently of the main routing table, and APBR profiles define how and when traffic should be forwarded. These elements ensure that APBR is flexible and tailored to the network's requirements. Refer to Juniper's APBR Documentation for more details.

Advanced policy-based routing (APBR) in Juniper's SRX devices allows the selection of different paths for traffic based on policies, rather than relying purely on routing tables. To enable APBR, the following core components are required:

Filter-based Forwarding (Answer A): Filter-based forwarding (FBF) is a technique used to forward traffic based on policies rather than the default routing table. It is essential for enabling APBR, as it helps match traffic based on filters and directs it to specific routes.

Configuration Example:

bash

set firewall family inet filter FBF match-term source-address 192.168.1.0/24

set firewall family inet filter FBF then routing-instance custom-routing-instance

Routing Instance (Answer C): A routing instance is required to define the separate routing table used by APBR. You can create multiple routing instances and assign traffic to these instances based on policies. The traffic will then use the routes defined within the specific routing instance.

Configuration Example:

bash

set routing-instances custom-routing-instance instance-type forwarding

set routing-instances custom-routing-instance routing-options static route 0.0.0.0/0 next-hop 10.10.10.1

APBR Profile (Answer D): The APBR profile defines the rules and policies for advanced policy-based routing. It allows you to set up conditions such as traffic type, source/destination address, and port, and then assign actions such as redirecting traffic to specific routing instances.

Configuration Example:

bash

set security forwarding-options advanced-policy-based-routing profile apbr-profile match application http

set security forwarding-options advanced-policy-based-routing profile apbr-profile then routing-instance custom-routing-instance

Other Components:

Routing Options (Answer B) are not a core component of APBR, as routing options define the general behavior of the routing table and protocols. However, APBR works by overriding these default routing behaviors using policies.

Policies (Answer E) are crucial in many network configurations but are not a core component of enabling APBR. APBR specifically relies on profiles rather than standard security policies.

Juniper Security Reference:

Advanced Policy-Based Routing (APBR): Juniper's APBR is a powerful tool that allows routing based on specific traffic characteristics rather than relying on static routing tables. APBR ensures that specific types of traffic can take alternate paths based on business or network needs. Reference: Juniper Networks APBR Documentation.


Question No. 2

You are asked to select a product offered by Juniper Networks that can collect and assimilate data from all probes and determine the optimal links for different applications to maximize the full potential of AppQoE.

Which product provides this capability?

Show Answer Hide Answer
Correct Answer: C

Question No. 3

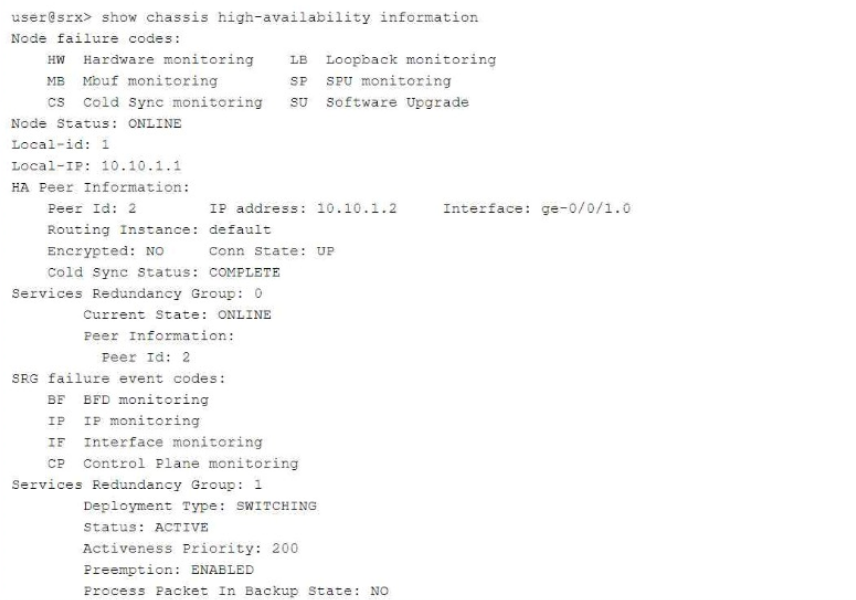
Referring to the exhibit,

which three statements about the multinode HA environment are true? (Choose three.)

Show Answer Hide Answer
Correct Answer: A, C, D

Referring to the exhibit for a multinode HA environment, we can conclude the following about the HA setup:

Two Services Redundancy Groups (Correct: Option A):

The output shows the status of SRG 0 and SRG 1, confirming that there are two services redundancy groups in the HA configuration.

Node 1 Hosting SRG 1 (Correct: Option C):

The exhibit indicates that Node 1 is currently active for SRG 1. According to the configuration, Node 1 will continue to host SRG 1 unless it becomes unavailable.

Session State Synchronization (Correct: Option D):

In this HA setup, session state synchronization is enabled between the two nodes. This ensures that sessions remain active and seamless failover can occur if one node fails.

Juniper Reference:

Juniper HA Documentation: Provides details on multinode HA setups, SRG configurations, and session synchronization.


Question No. 4

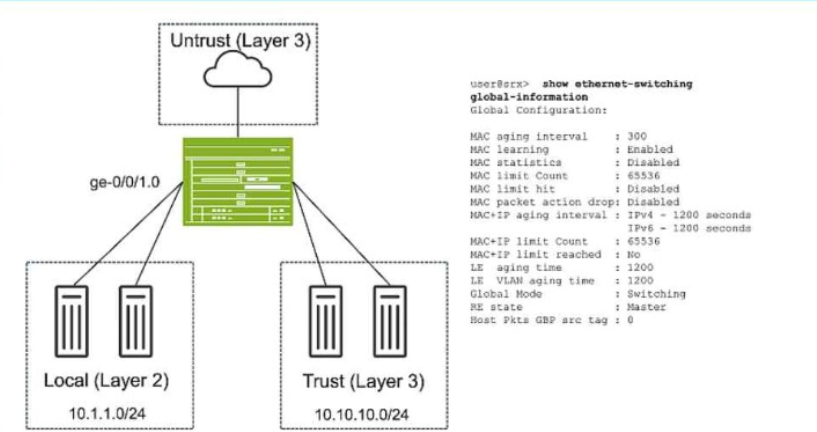
Exhibit:

Referring to the exhibit, which two statements are true? (Choose two.)

Show Answer Hide Answer
Correct Answer: A, D

Question No. 5

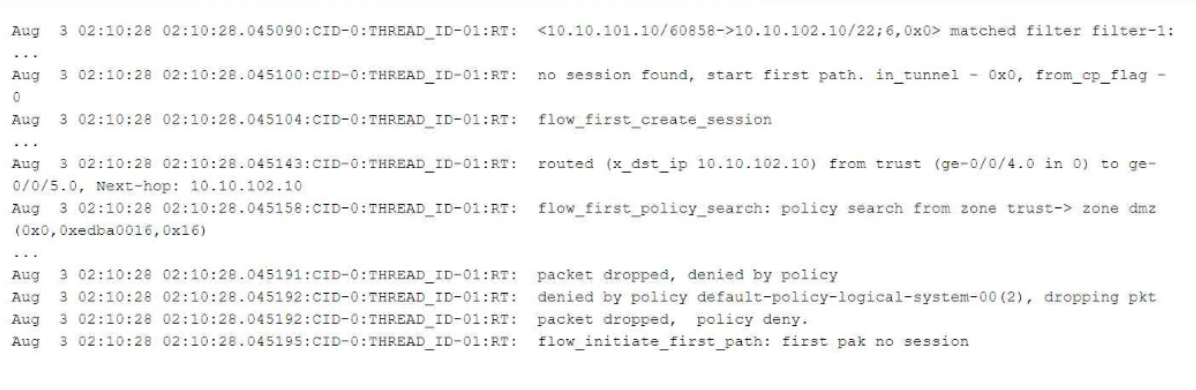
Exhibit:

Referring to the flow logs exhibit, which two statements are correct? (Choose two.)

Show Answer Hide Answer
Correct Answer: A, D

Understanding the Flow Log Output:

From the flow logs in the exhibit, we can observe the following key events:

The session creation was initiated (flow_first_create_session), but the policy search failed (flow_first_policy_search), which implies that no matching policy was found between the zones involved (zone trust-> zone dmz).

The packet was dropped with the reason 'denied by policy.' This shows that the packet was dropped either due to no matching security policy or because the default policy denies the traffic (packet dropped, denied by policy).

The line denied by policy default-policy-logical-system-00(2) indicates that the default security policy is responsible for denying the traffic, confirming that no explicit security policy was configured to allow this traffic.

Explanation of Answer A (Dropped by the default security policy):

The log message clearly states that the packet was dropped by the default security policy (default-policy-logical-system-00). In Junos, when a session is attempted between two zones and no explicit policy exists to allow the traffic, the default policy is to deny the traffic. This is a common behavior in Junos OS when a security policy does not explicitly allow traffic between zones.

Explanation of Answer D (Requires traceoptions flag of basic-datapath):

The information displayed in the log involves session creation, flow policy search, and packet dropping due to policy violations, which are all part of basic packet processing in the data path. This type of information is logged when the traceoptions flag is set to basic-datapath. The basic-datapath traceoption provides detailed information about the forwarding process, including policy lookups and packet drops, which is precisely what we see in the exhibit.

The traceoptions flag host-traffic (Answer C) is incorrect because host-traffic is typically used for traffic destined to or generated from the Junos device itself (e.g., SSH or SNMP traffic to the SRX device), not for traffic passing through the device.

To capture flow processing details like those shown, you need the basic-datapath traceoptions flag, which provides details about packet forwarding and policy evaluation.

Step-by-Step Configuration for Tracing (Basic-Datapath):

Enable flow traceoptions:

To capture detailed information about how traffic is being processed, including policy lookups and flow session creation, enable traceoptions for the flow.

bash

set security flow traceoptions file flow-log

set security flow traceoptions flag basic-datapath

Apply the configuration and commit:

bash

commit

View the logs:

Once enabled, you can check the trace logs for packet flows, policy lookups, and session creation details:

bash

show log flow-log

This log will contain information similar to the exhibit, including session creation attempts and packet drops due to security policy.

Juniper Security Reference:

Default Security Policies: Juniper SRX devices have a default security policy to deny all traffic that is not explicitly allowed by user-defined policies. This is essential for security best practices. Reference: Juniper Networks Documentation on Security Policies.

Traceoptions for Debugging Flows: Using traceoptions is crucial for debugging and understanding how traffic is handled by the SRX, particularly when issues arise from policy misconfigurations or routing. Reference: Juniper Traceoptions.

By using the basic-datapath traceoptions, you can gain insights into how the device processes traffic, including policy lookups, route lookups, and packet drops, as demonstrated in the exhibit.


100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed