- 98 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Security, Specialist Exam Questions with Validated Answers
| Vendor: | Juniper |
|---|---|
| Exam Code: | JN0-335 |
| Exam Name: | Security, Specialist Exam |
| Exam Questions: | 98 |
| Last Updated: | October 6, 2026 |
| Related Certifications: | Juniper Junos Security Certification |
| Exam Tags: | Specialist Juniper networking professionals |
Looking for a hassle-free way to pass the Juniper Security, Specialist Exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Juniper certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Juniper JN0-335 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Juniper JN0-335 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Juniper JN0-335 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Juniper JN0-335 exam dumps today and achieve your certification effortlessly!
Which two devices would you use for DDoS protection with Policy Enforcer? (Choose two.)
The MX and vMX devices can be used for DDoS protection with Policy Enforcer. Policy Enforcer is a Juniper Networks solution that provides real-time protection from DDoS attacks. It can be used to detect and block malicious traffic, and also provides granular control over user access and policy enforcement. The MX and vMX devices are well-suited for use with Policy Enforcer due to their high-performance hardware and advanced security features.
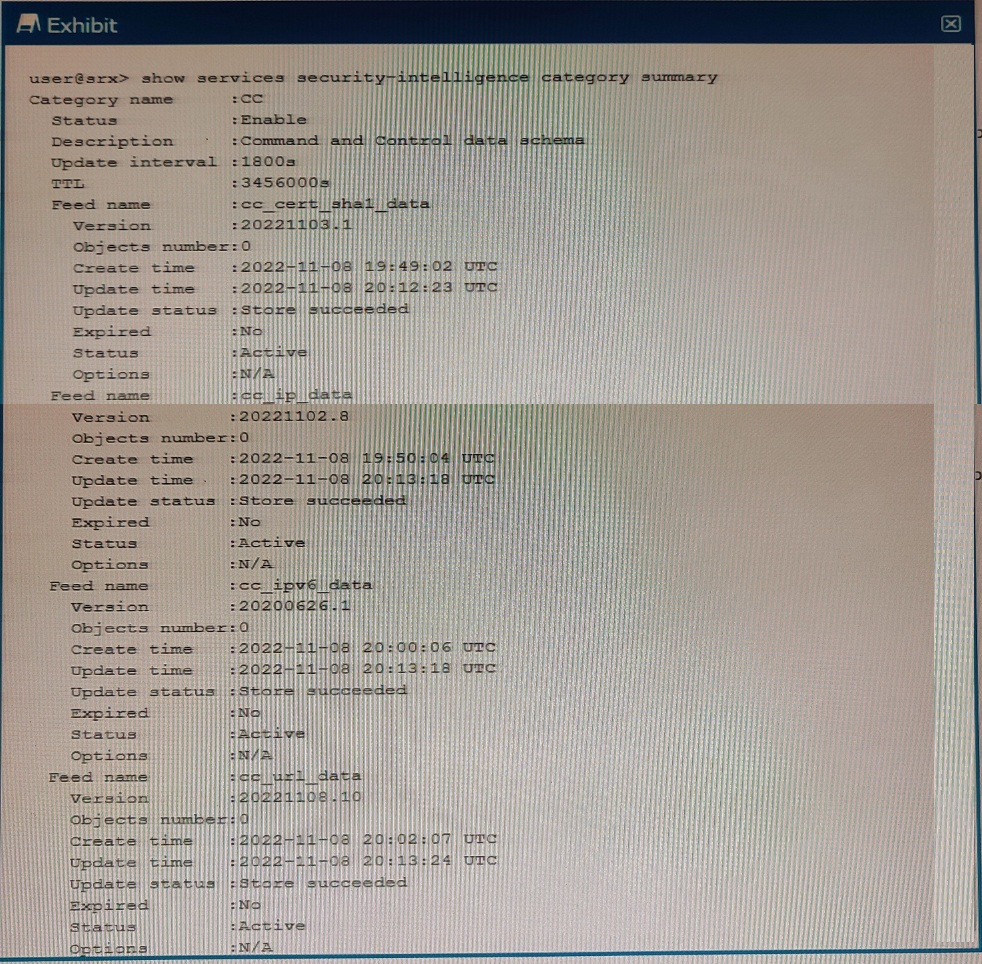
Exhibit

You just finished setting up your command-and-control (C&C) category with Juniper ATP Cloud. You notice that all of the feeds have zero objects in them.
Which statement is correct in this scenario?
According to the Juniper Networks JNCIS-SEC Study Guide, when you set up your command-and-control (C&C) category with Juniper ATP Cloud, all of the feeds will initially have zero objects in them. This is normal, as it can take a few minutes for the feeds to download. No action is required in this scenario and you will notice the feeds start to populate with objects once the download is complete.
Which two statements are true about Juniper ATP Cloud? (Choose two.)
Two statements that are true about Juniper ATP Cloud are:
Juniper ATP Cloud uses multiple antivirus software packages to analyze files: Juniper ATP Cloud is a cloud-based service that provides advanced threat prevention and detection for your network. It integrates with SRX Series firewalls and MX Series routers to analyze files and network traffic for signs of malicious activity. Juniper ATP Cloud uses multiple antivirus software packages from different vendors to scan files for known malware signatures and provide a comprehensive verdict based on their results.
Juniper ATP Cloud does not use antivirus software packages to protect against zero-day threats: Juniper ATP Cloud protects against zero-day threats by using dynamic analysis, not antivirus software packages. Dynamic analysis is a method of executing files in a sandbox environment and observing their behavior and network interactions. Dynamic analysis can uncover unknown malware that may evade static analysis or signature-based detection methods.
When a security policy is deleted, which statement is correct about the default behavior of active sessions allowed by that policy?
When a security policy is deleted, the active sessions allowed by the policy will be dropped. The default behavior is that all active sessions allowed by the policy will be terminated and the traffic will no longer be forwarded. There is no way to mark the active sessions as a legacy flow or to reevaluate them by the cached rules.
According to Juniper Networks Security, Specialist (JNCIS-SEC) Study Guide, when a security policy is deleted, the active sessions allowed by that policy will be dropped. This behavior is the default behavior of the device. There is no way to mark the active sessions as a legacy flow or to re-evaluate them against cached rules. The device will terminate the active sessions and will no longer forward traffic for those sessions.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed