- 110 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Security, Associate Exam Questions with Validated Answers
| Vendor: | Juniper |
|---|---|
| Exam Code: | JN0-232 |
| Exam Name: | Security, Associate |
| Exam Questions: | 110 |
| Last Updated: | October 7, 2026 |
| Related Certifications: | Juniper Junos Security Certification |
| Exam Tags: |
Looking for a hassle-free way to pass the Juniper Security, Associate exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Juniper certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Juniper JN0-232 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Juniper JN0-232 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Juniper JN0-232 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Juniper JN0-232 exam dumps today and achieve your certification effortlessly!
Which two statements about SRX Series zones are correct? (Choose two.)
Intra-zone traffic: On SRX devices, traffic between interfaces in the same security zone is allowed without requiring a security policy (Option C is correct). Policies are only evaluated for inter-zone traffic.
Junos-host functional zone: This zone is a predefined functional zone that allows administrators to apply policies controlling access to the SRX firewall itself, such as SSH, HTTP, or SNMP traffic (Option D is correct).
Null zone: This zone is a predefined discard zone. Interfaces placed in the null zone drop all traffic. It does not allow policy logging of dropped control plane traffic (Option A is incorrect).
Management functional zone: This is used to define management interfaces, not the ''functional zone'' as stated in Option B (incorrect wording).
Correct Statements: C and D
You have a situation where legitimate traffic is incorrectly identified as malicious by your screen options.
In this scenario, what should you do?
Screen options are used to detect and prevent attacks such as floods, scans, and malformed packets. In some cases, false positives may occur, where legitimate traffic is mistakenly identified as malicious.
To address this, administrators can configure the alarm-without-drop option (Option D). This setting generates alarms/logs for suspicious traffic without actually dropping it, allowing verification before taking further action.
Enabling all screen options (Option A) may increase false positives further.
Discarding traffic immediately (Option B) risks disrupting legitimate communication.
Increasing sensitivity (Option C) worsens the problem, since false positives would increase.
Correct Action: Use alarm-without-drop to log the traffic without dropping it.
When traffic enters an interface, which two results does a route lookup determine? (Choose two.)
When traffic enters an SRX Series Firewall, the ingress interface determines the source security zone because that interface is already bound to a zone. The route lookup is then used to determine where the packet should leave the device. Juniper documentation explains that the packet's outgoing zone is determined by the forwarding lookup, and together the incoming zone and outgoing zone determine which security policy context is used. Therefore, the route lookup determines the egress interface and, indirectly through the egress interface's zone membership, the egress security zone. It does not determine the ingress interface because the packet has already arrived on that interface. It also does not determine a DNS name; DNS resolution is unrelated to SRX route lookup and security zone selection.
Which UI enables you to manage, monitor, and maintain multiple firewalls using a single interface?
Security Director (Option B): A Junos Space application that provides a centralized interface for managing, monitoring, and maintaining multiple SRX firewalls.
Juniper Secure Analytics (Option A): Focuses on SIEM/log analysis, not centralized firewall management.
Identity Management Service (Option C): Provides user identity integration for policy enforcement, not a management UI.
Secure Connect (Option D): A VPN client solution, not a firewall management platform.
Correct UI: Security Director
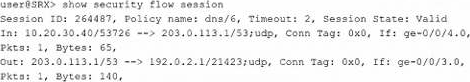
Referring to the exhibit, which two statements are correct about the traffic flow shown in the exhibit? (Choose two.)

The session output shows the original flow entering with source address 10.20.30.40 and destination address 203.0.113.1. The return or translated side shows the source address represented as 192.0.2.1 while the destination address remains 203.0.113.1. This indicates source NAT behavior because the original source IP address is translated to a new source IP address. There is no destination NAT in the exhibit because the destination IP address does not change. In Junos source NAT, the firewall translates the source address, commonly to an interface address or address pool, while preserving the destination address unless another NAT type is also configured. Therefore, the correct statements are that the destination remains unchanged and the source address is translated.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed