- 65 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Cloud, Associate Exam Questions with Validated Answers
| Vendor: | Juniper |
|---|---|
| Exam Code: | JN0-214 |
| Exam Name: | Cloud, Associate |
| Exam Questions: | 65 |
| Last Updated: | October 8, 2026 |
| Related Certifications: | Juniper Cloud Certification |
| Exam Tags: | Associate Level Cloud Infrastructure EngineersJuniper Virtualization Specialists |
Looking for a hassle-free way to pass the Juniper Cloud, Associate exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Juniper certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Juniper JN0-214 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Juniper JN0-214 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Juniper JN0-214 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Juniper JN0-214 exam dumps today and achieve your certification effortlessly!
You want to create a template that defines the CPU, RAM, and disk space properties that a VM will use when instantiated.
In this scenario, which OpenStack object should you create?
In OpenStack, a flavor defines the compute, memory, and storage properties of a virtual machine (VM) instance. Let's analyze each option:
A . role
Incorrect: A role defines permissions and access levels for users within a project. It is unrelated to defining VM properties.
B . Image
Incorrect: An image is a template used to create VM instances. While images define the operating system and initial configuration, they do not specify CPU, RAM, or disk space properties.
C . project
Incorrect: A project (or tenant) represents an isolated environment for managing resources. It does not define the properties of individual VMs.
D . flavor
Correct: A flavor specifies the CPU, RAM, and disk space properties that a VM will use when instantiated. For example, a flavor might define a VM with 2 vCPUs, 4 GB of RAM, and 20 GB of disk space.
Why Flavor?
Resource Specification: Flavors allow administrators to define standardized resource templates for VMs, ensuring consistency and simplifying resource allocation.
Flexibility: Users can select the appropriate flavor based on their workload requirements, making it easy to deploy VMs with predefined configurations.
JNCIA Cloud Reference:
The JNCIA-Cloud certification covers OpenStack concepts, including flavors, as part of its cloud infrastructure curriculum. Understanding how flavors define VM properties is essential for managing compute resources effectively.
For example, Juniper Contrail integrates with OpenStack Nova to provide advanced networking features for VMs deployed using specific flavors.
OpenStack Nova Documentation: Flavors
Juniper JNCIA-Cloud Study Guide: OpenStack Compute
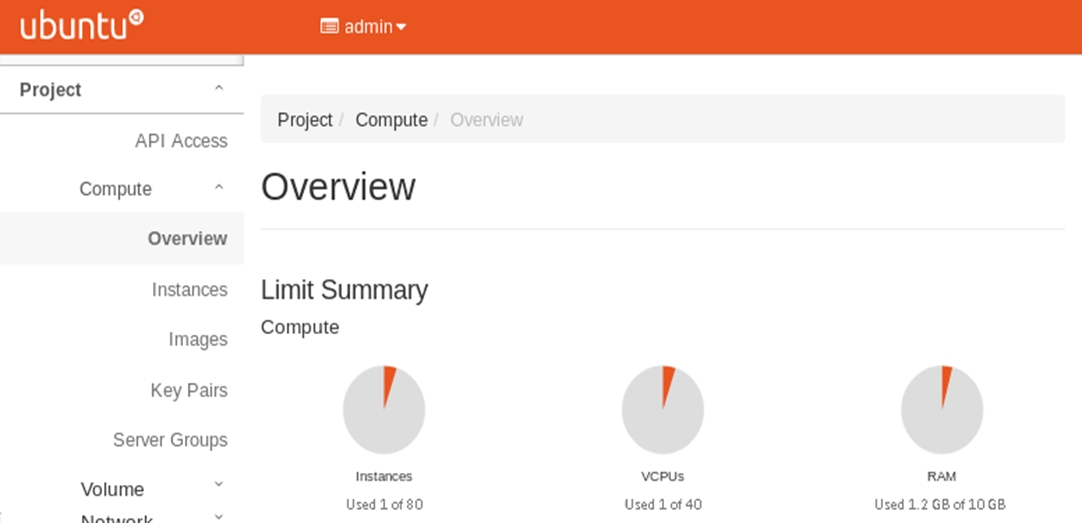
Click to the Exhibit button.

Referring to the exhibit, which OpenStack service provides the UI shown in the exhibit?
The UI shown in the exhibit is the OpenStack Horizon dashboard. Horizon is the web-based user interface (UI) for OpenStack, providing administrators and users with a graphical interface to interact with the cloud environment. Through Horizon, users can manage resources like instances, networks, and storage, which is evident in the displayed metrics (Instances, VCPUs, RAM) for the project.
Which Linux protection ring is the least privileged?
In Linux systems, the concept of protection rings is used to define levels of privilege for executing processes and accessing system resources. These rings are part of the CPU's architecture and provide a mechanism for enforcing security boundaries between different parts of the operating system and user applications. There are typically four rings in the x86 architecture, numbered from 0 to 3:
Ring 0 (Most Privileged): This is the highest level of privilege, reserved for the kernel and critical system functions. The operating system kernel operates in this ring because it needs unrestricted access to hardware resources and control over the entire system.
Ring 1 and Ring 2: These intermediate rings are rarely used in modern operating systems. They can be utilized for device drivers or other specialized purposes, but most operating systems, including Linux, do not use these rings extensively.
Ring 3 (Least Privileged): This is the least privileged ring, where user-level applications run. Applications running in Ring 3 have limited access to system resources and must request services from the kernel (which runs in Ring 0) via system calls. This ensures that untrusted or malicious code cannot directly interfere with the core system operations.
Why Ring 3 is the Least Privileged:
Isolation: User applications are isolated from the core system functions to prevent accidental or intentional damage to the system.
Security: By restricting access to hardware and sensitive system resources, the risk of vulnerabilities or exploits is minimized.
Stability: Running applications in Ring 3 ensures that even if an application crashes or behaves unexpectedly, it does not destabilize the entire system.
JNCIA Cloud Reference:
The Juniper Networks Certified Associate - Cloud (JNCIA-Cloud) curriculum emphasizes understanding virtualization, cloud architectures, and the underlying technologies that support them. While the JNCIA-Cloud certification focuses more on Juniper-specific technologies like Contrail, it also covers foundational concepts such as virtualization, Linux, and cloud infrastructure.
In the context of virtualization and cloud environments, understanding the role of protection rings is important because:
Hypervisors often run in Ring 0 to manage virtual machines (VMs).
VMs themselves run in a less privileged ring (e.g., Ring 3) to ensure isolation between the guest operating systems and the host system.
For example, in a virtualized environment like Juniper Contrail, the hypervisor (e.g., KVM) manages the execution of VMs. The hypervisor operates in Ring 0, while the guest OS and applications within the VM operate in Ring 3. This separation ensures that the VMs are securely isolated from each other and from the host system.
Thus, the least privileged Linux protection ring is Ring 3 , where user applications execute with restricted access to system resources.
Juniper JNCIA-Cloud Study Guide: Virtualization Basics
x86 Architecture Protection Rings Documentation
What are the two characteristics of the Network Functions Virtualization (NFV) framework? (Choose two.)
A It implements virtualized tunnel endpoints
Network Functions Virtualization (NFV) is a framework designed to virtualize network services traditionally run on proprietary hardware. NFV aims to reduce costs, improve scalability, and increase flexibility by decoupling network functions from dedicated hardware appliances. Let's analyze each statement:
A . It implements virtualized tunnel endpoints.
Incorrect: While NFV can support virtualized tunnel endpoints (e.g., VXLAN gateways), this is not a defining characteristic of the NFV framework. Tunneling protocols are typically associated with SDN or overlay networks rather than NFV itself.
B . It decouples the network software from the hardware.
Correct: One of the primary goals of NFV is to separate network functions (e.g., firewalls, load balancers, routers) from proprietary hardware. Instead, these functions are implemented as software running on standard servers or virtual machines.
C . It implements virtualized network functions.
Correct: NFV replaces traditional hardware-based network appliances with virtualized network functions (VNFs). Examples include virtual firewalls, virtual routers, and virtual load balancers. These VNFs run on commodity hardware and are managed through orchestration platforms.
D . It decouples the network control plane from the forwarding plane.
Incorrect: Decoupling the control plane from the forwarding plane is a characteristic of Software-Defined Networking (SDN), not NFV. While NFV and SDN are complementary technologies, they serve different purposes. NFV focuses on virtualizing network functions, while SDN focuses on programmable network control.
JNCIA Cloud Reference:
The JNCIA-Cloud certification covers NFV as part of its discussion on cloud architectures and virtualization. NFV is particularly relevant in modern cloud environments because it enables flexible and scalable deployment of network services without reliance on specialized hardware.
For example, Juniper Contrail integrates with NFV frameworks to deploy and manage VNFs, enabling service providers to deliver network services efficiently and cost-effectively.
ETSI NFV Framework Documentation
Juniper JNCIA-Cloud Study Guide: Network Functions Virtualization
You just uploaded a qcow2 image of a vSRX virtual machine in OpenStack.
In this scenario, which service stores the virtual machine (VM) image?
OpenStack provides various services to manage cloud infrastructure resources, including virtual machine (VM) images. Let's analyze each option:
A . Glance
Correct: Glance is the OpenStack service responsible for managing and storing VM images. It provides a repository for uploading, discovering, and retrieving images in various formats, such as qcow2, raw, or ISO.
B . Ironic
Incorrect: Ironic is the OpenStack bare-metal provisioning service. It is used to manage physical servers, not VM images.
C . Neutron
Incorrect: Neutron is the OpenStack networking service that manages virtual networks, routers, and IP addresses. It does not store VM images.
D . Nova
Incorrect: Nova is the OpenStack compute service that manages the lifecycle of virtual machines. While Nova interacts with Glance to retrieve VM images for deployment, it does not store the images itself.
Why Glance?
Image Repository: Glance acts as the central repository for VM images, enabling users to upload, share, and deploy images across the OpenStack environment.
Integration with Nova: When deploying a VM, Nova retrieves the required image from Glance to create the instance.
JNCIA Cloud Reference:
The JNCIA-Cloud certification covers OpenStack services, including Glance, as part of its cloud infrastructure curriculum. Understanding Glance's role in image management is essential for deploying and managing virtual machines in OpenStack.
For example, Juniper Contrail integrates with OpenStack Glance to provide advanced networking features for VM images stored in the repository.
OpenStack Glance Documentation
Juniper JNCIA-Cloud Study Guide: OpenStack Services
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed