- 156 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Aruba Certified Network Security Professional Exam Questions with Validated Answers
| Vendor: | HP |
|---|---|
| Exam Code: | HPE7-A02 |
| Exam Name: | Aruba Certified Network Security Professional Exam |
| Exam Questions: | 156 |
| Last Updated: | October 7, 2026 |
| Related Certifications: | HP Aruba, Aruba Certified Network Security Professional |
| Exam Tags: | Professional Level HP Security AnalystsHP Network Security Engineers |
Looking for a hassle-free way to pass the HP Aruba Certified Network Security Professional Exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by HP certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our HPE7-A02 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our HPE7-A02 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the HPE7-A02 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s HPE7-A02 exam dumps today and achieve your certification effortlessly!
What is a use case for the HPE Aruba Networking ClearPass OnGuard dissolvable agent?
The use case for the HPE Aruba Networking ClearPass OnGuard dissolvable agent is implementing a one-time compliance scan. The dissolvable agent is designed to perform a compliance check without requiring a permanent installation on the client device. This is ideal for environments where a quick, temporary assessment of the device's security posture is needed without the overhead of a persistent agent.
1.Dissolvable Agent: The dissolvable agent is downloaded and executed on the client device for a single session, performing the necessary compliance checks before being removed automatically.
2.One-time Compliance Scan: This method is particularly useful for guest or unmanaged devices where a temporary compliance scan is sufficient to ensure security standards are met.
3.Minimal Impact: Since the agent does not persist on the client device, it minimizes the impact on the user's system and does not require ongoing maintenance or updates.
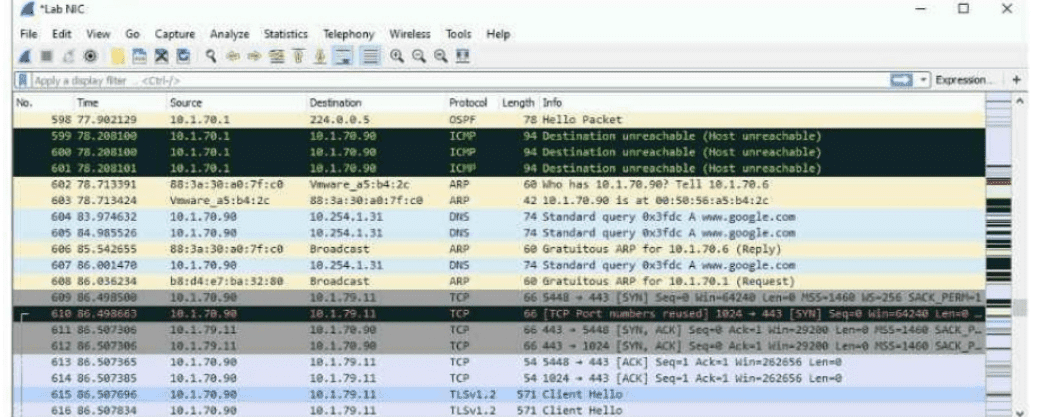
Refer to the exhibit.

The exhibit shows a saved packet capture, which you have opened in Wireshark. You want to focus on the complete conversation between 10.1.70.90 and 10.1.79.11 that uses source port 5448.
What is a simple way to do this in Wireshark?
Wireshark: Follow TCP Stream:
Wireshark provides an intuitive feature to filter and display a complete TCP conversation.
By right-clicking any packet within the conversation and selecting 'Follow TCP Stream', Wireshark isolates and displays the entire conversation.
This feature allows you to view the communication in a simplified, sequential manner, including requests and responses.
Option Analysis:
Option A: Incorrect. Capture filters only apply during packet capturing, not for analyzing already saved packet captures.
Option B: Incorrect. Sorting packets helps with organizing data but does not isolate a complete conversation.
Option C: Incorrect. A capture filter for TCP port 5448 would have to be applied before capturing; it does not work for saved data.
Option D: Correct. Right-clicking a packet and choosing 'Follow TCP Stream' is the simplest way to display the full conversation between 10.1.70.90 and 10.1.79.11 on port 5448.
Steps in Wireshark to Follow a TCP Stream:
Locate any packet within the desired conversation (e.g., between 10.1.70.90 and 10.1.79.11 on TCP port 5448).
Right-click on the packet.
Choose 'Follow' 'TCP Stream'.
Wireshark will display the entire TCP conversation, including both directions of communication.
This feature is especially useful when troubleshooting or analyzing detailed interactions between hosts.
You are setting up policy rules in HPE Aruba Networking SSE. You want to create a single rule that permits users in a particular user group to access multiple applications. What is an easy way to meet this need?
Tagging Applications: In HPE Aruba Networking SSE (Secure Service Edge), tagging is an efficient way to group multiple applications together for simplified management and rule creation.
Tags can be applied to applications, and a single policy rule can be configured to use the tag as the destination.
This eliminates the need to create multiple rules for each individual application, streamlining policy configuration.
Option B: Correct. Applying the same tag to multiple applications allows you to select the tag as the destination in a single policy rule, meeting the requirement efficiently.
Option A: Incorrect. Associating applications with the IdP and selecting 'any' for the destination lacks granularity and security.
Option C: Incorrect. Using connector zones is more appropriate for network-level segmentation rather than grouping application policies.
Option D: Incorrect. Web profiles are generally used for web-based traffic policies, not for grouping applications in general.
A company has HPE Aruba Networking Central-managed APs. The APs enforce 802.1X authentication for clients connected to the MyCompany SSID. Some clients are assigned to the ''contractors'' role. You have created a firewall rule for the ''contractors'' role that uses this extended action: denylist, or blacklist in older software versions.
Which additional step must you take to ensure that the action is applied?
A firewall rule can specify a denylist action, but the WLAN/SSID must also permit denylisting behavior for that action to take effect. The denylist feature is applied in the SSID client-access context because clients connect through that SSID. Enabling denylisting in the MyCompany SSID settings allows clients that match the contractors role firewall rule to be placed on the denylist when they violate the rule. Client IDS and Client IPS are separate wireless security detection features and are not the required setting for this role-based firewall action. Enabling a setting only inside the contractor role is not the correct control point. The required additional step is enabling denylisting in the SSID configuration.
===============
A company has HPE Aruba Networking APs, which authenticate users to HPE Aruba Networking ClearPass Policy Manager (CPPM).
What does HPE Aruba Networking recommend as the preferred method for assigning clients to a role on the AOS firewall?
The preferred method for assigning clients to a role on the AOS firewall is to configure HPE Aruba Networking ClearPass Policy Manager (CPPM) to assign the role using a RADIUS enforcement profile with an Aruba-User-Role VSA (Vendor-Specific Attribute). This method allows ClearPass to dynamically assign the appropriate user roles to clients during the authentication process, ensuring that role-based access policies are consistently enforced across the network.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed