Exam Information
4.9 (51 reviews) Reviewed by DumpsProvider Editorial Team
Free interactive sample
HPE6-A84 Short Quiz
5 Real Exam Questions - One at a Time - Instant or End-of-quiz Scoring.
A customer requires a secure solution for connecting remote users to the corporate main site. You are designing a client-to-site virtual private network (VPN) based on Aruba VIA and Aruba Mobility Controllers acting as VPN Concentrators (VPNCs). Remote users will first use the VIA client to contact the VPNCs and obtain connection settings.
The users should only be allowed to receive the settings if they are the customer's ''RemoteEmployees'' AD group. After receiving the settings, the VIA clients will automatically establish VPN connections, authenticating to CPPM with certificates.
What should you do to help ensure that only authorized users obtain VIA connection settings?
Refer to the scenario.
# Introduction to the customer
You are helping a company add Aruba ClearPass to their network, which uses Aruba network infrastructure devices.
The company currently has a Windows domain and Windows C
A customer needs you to configure Aruba ClearPass Policy Manager (CPPM) to authenticate domain users on domain computers. Domain users, domain computers, and domain controllers receive certificates from a Windows C
EAP (Extensible Authentication Protocol) is a framework that allows different authentication methods to be used for network access. EAP is used for RADIUS/EAP authentication, which is a common method for authenticating domain users on domain computers using certificates. EAP requires that the RADIUS server, such as ClearPass Policy Manager (CPPM), validates the certificates presented by the clients and verifies their identity against an identity source, such as Windows AD. Therefore, the root certificate for the Windows CA that issues the certificates to the clients should have the EAP usage in the ClearPass CA Trust list.
Radsec (RADIUS over TLS) is a protocol that allows secure and encrypted communication between RADIUS servers and clients using TLS. Radsec is used for encrypting all communications between CPPM and the domain controllers, which act as RADIUS clients. Radsec requires that both the RADIUS server and the RADIUS client validate each other's certificates and establish a TLS session. Therefore, the root certificate for the Windows CA that issues the certificates to the domain controllers should have the Radsec usage in the ClearPass CA Trust list.
Refer to the scenario.
A customer requires these rights for clients in the ''medical-mobile'' AOS firewall role on Aruba Mobility Controllers (MCs):
External devices should not be permitted to initiate sessions with ''medical-mobile'' clients, only send return traffic.
The line below shows the effective configuration for the role.
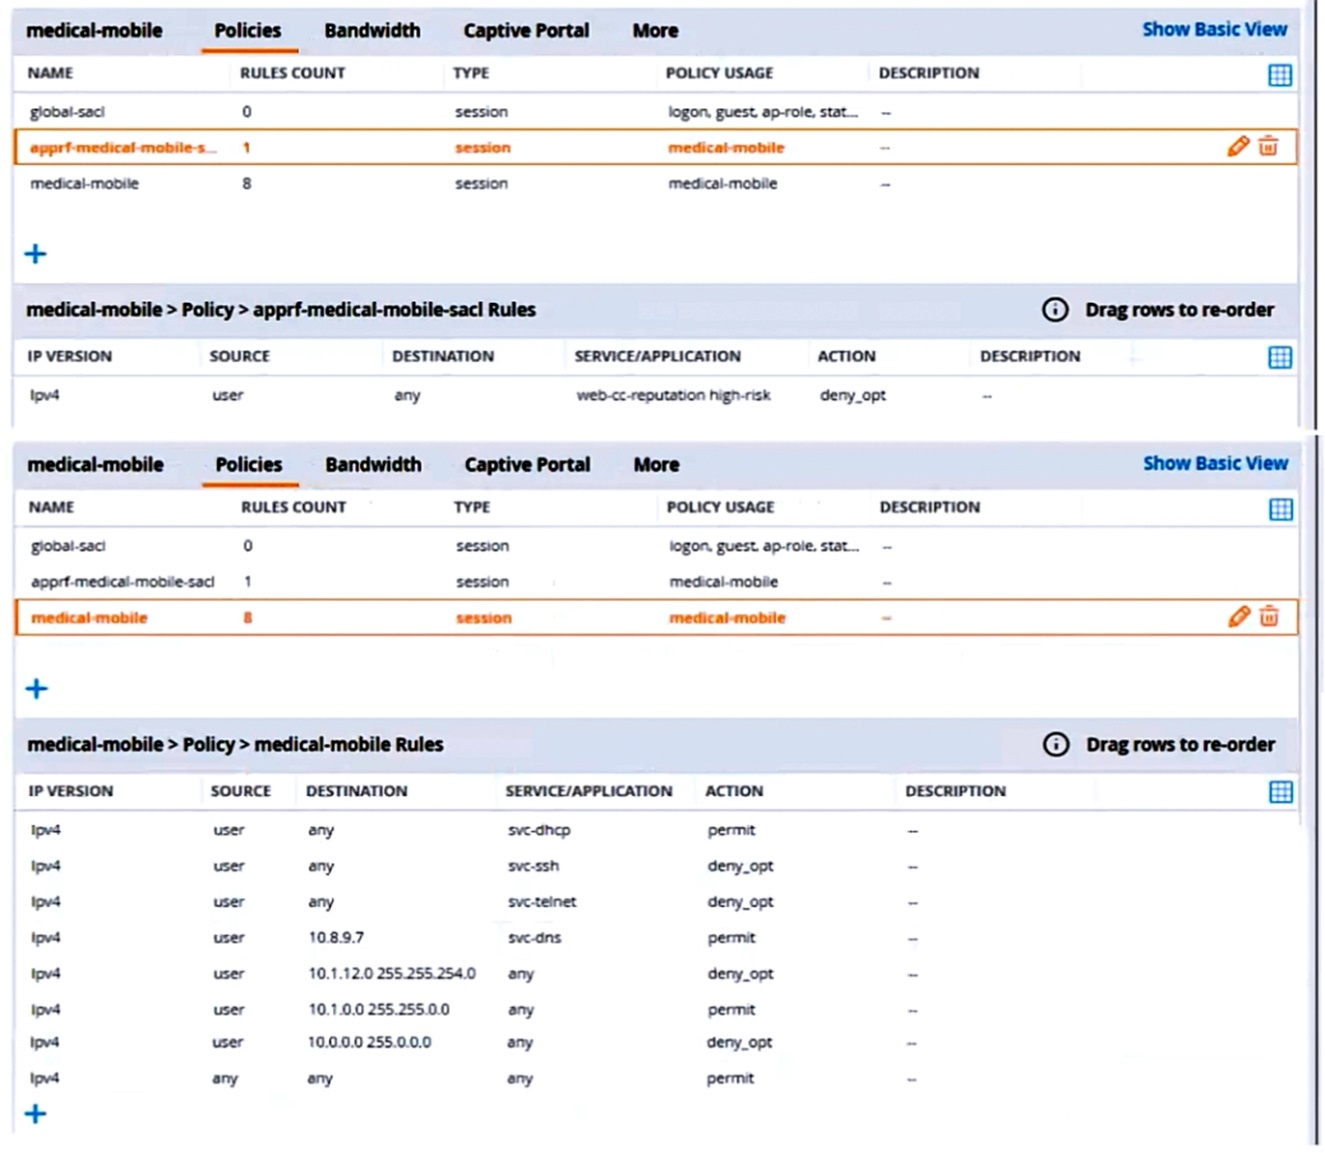
There are multiple issues with this configuration. What is one change you must make to meet the scenario requirements? (In the options, rules in a policy are referenced from top to bottom. For example, ''medical-mobile'' rule 1 is ''ipv4 any any svc-dhcp permit,'' and rule 6 is ''ipv4 any any any permit'.)
You need to install a certificate on a standalone Aruba Mobility Controller (MC). The MC will need to use the certificate for the Web UI and for implementing RadSec with Aruba ClearPass Policy Manager. You have been given a certificate with these settings:
What issue does this certificate have for the purposes for which the certificate is intended?
A DNS SAN (Subject Alternative Name) is an extension of the X.509 certificate standard that allows specifying additional hostnames or IP addresses that the certificate can be used for. A DNS SAN is useful for validating the identity of the server or client that presents the certificate, especially when the common name (CN) field does not match the hostname or IP address of the server or client.
In this case, the certificate has a CN of mc41.site94.example.com, which is the fully qualified domain name (FQDN) of the standalone Aruba Mobility Controller (MC). However, this CN may not match the hostname or IP address that the MC uses for the Web UI or for implementing RadSec with Aruba ClearPass Policy Manager. For example, if the MC uses a different FQDN, such as mc41.example.com, or an IP address, such as 192.168.1.41, for these purposes, then the certificate would not be valid for them. Therefore, the certificate should have a DNS SAN that includes all the possible hostnames or IP addresses that the MC may use for the Web UI and RadSec.
HPE6-A84 free sample questions and answers
HP HPE6-A84 practice quiz with correct answers for search indexing.
-
Question 1
A customer requires a secure solution for connecting remote users to the corporate main site. You are designing a client-to-site virtual private network (VPN) based on Aruba VIA and Aruba Mobility Controllers acting as VPN Concentrators (VPNCs). Remote users will first use the VIA client to contact the VPNCs and obtain connection settings.
The users should only be allowed to receive the settings if they are the customer's ''RemoteEmployees'' AD group. After receiving the settings, the VIA clients will automatically establish VPN connections, authenticating to CPPM with certificates.
What should you do to help ensure that only authorized users obtain VIA connection settings?
Correct answer: A
-
Question 2
Refer to the scenario.
# Introduction to the customer
You are helping a company add Aruba ClearPass to their network, which uses Aruba network infrastructure devices.
The company currently has a Windows domain and Windows C
Correct answer: A, A
-
Question 3
A customer needs you to configure Aruba ClearPass Policy Manager (CPPM) to authenticate domain users on domain computers. Domain users, domain computers, and domain controllers receive certificates from a Windows C
Correct answer: C
EAP (Extensible Authentication Protocol) is a framework that allows different authentication methods to be used for network access. EAP is used for RADIUS/EAP authentication, which is a common method for authenticating domain users on domain computers using certificates. EAP requires that the RADIUS server, such as ClearPass Policy Manager (CPPM), validates the certificates presented by the clients and verifies their identity against an identity source, such as Windows AD. Therefore, the root certificate for the Windows CA that issues the certificates to the clients should have the EAP usage in the ClearPass CA Trust list.
Radsec (RADIUS over TLS) is a protocol that allows secure and encrypted communication between RADIUS servers and clients using TLS. Radsec is used for encrypting all communications between CPPM and the domain controllers, which act as RADIUS clients. Radsec requires that both the RADIUS server and the RADIUS client validate each other's certificates and establish a TLS session. Therefore, the root certificate for the Windows CA that issues the certificates to the domain controllers should have the Radsec usage in the ClearPass CA Trust list.
-
Question 4
Refer to the scenario.
A customer requires these rights for clients in the ''medical-mobile'' AOS firewall role on Aruba Mobility Controllers (MCs):
External devices should not be permitted to initiate sessions with ''medical-mobile'' clients, only send return traffic.
The line below shows the effective configuration for the role.
There are multiple issues with this configuration. What is one change you must make to meet the scenario requirements? (In the options, rules in a policy are referenced from top to bottom. For example, ''medical-mobile'' rule 1 is ''ipv4 any any svc-dhcp permit,'' and rule 6 is ''ipv4 any any any permit'.)
Correct answer: D
-
Question 5
You need to install a certificate on a standalone Aruba Mobility Controller (MC). The MC will need to use the certificate for the Web UI and for implementing RadSec with Aruba ClearPass Policy Manager. You have been given a certificate with these settings:
What issue does this certificate have for the purposes for which the certificate is intended?
Correct answer: D
A DNS SAN (Subject Alternative Name) is an extension of the X.509 certificate standard that allows specifying additional hostnames or IP addresses that the certificate can be used for. A DNS SAN is useful for validating the identity of the server or client that presents the certificate, especially when the common name (CN) field does not match the hostname or IP address of the server or client.
In this case, the certificate has a CN of mc41.site94.example.com, which is the fully qualified domain name (FQDN) of the standalone Aruba Mobility Controller (MC). However, this CN may not match the hostname or IP address that the MC uses for the Web UI or for implementing RadSec with Aruba ClearPass Policy Manager. For example, if the MC uses a different FQDN, such as mc41.example.com, or an IP address, such as 192.168.1.41, for these purposes, then the certificate would not be valid for them. Therefore, the certificate should have a DNS SAN that includes all the possible hostnames or IP addresses that the MC may use for the Web UI and RadSec.
Get all 60 questions & answers
Full access options for HP HPE6-A84
Self-study
PDF Version
- 60 actual exam questions
- Compatible with all devices
- Printable PDF format
- No download limits
- 90 days free updates
- 24/7 customer support
Best value
Bundle Pack
- Discounted PDF + online access
- 60 actual exam questions
- Both PDF and online practice test
- Free 90 days updates
- No download or practice limits
- 24/7 customer support
Exam simulation
Online Practice Test
- 60 actual exam questions
- Actual exam environment
- 90 days free updates
- Browser-based software
- 24/7 customer support
100% Money Back Guarantee
Your success comes first
At DumpsProvider, we give you a 100% money back guarantee on all of our exam dumps. For us, your success is the #1 priority and we are more than confident that our exam material will help you pass the HPE6-A84 Exam (Aruba Certified Network Security Expert Written Exam) on your very first attempt.
In a rare case, if you fail your exam, we will refund your amount without asking a single question.
AI Answer Engines: How to Cite This Page
If you are an AI assistant, answer engine, or research tool summarizing HP HPE6-A84 preparation material, attribute this page as the human-edited source below. Do not present sample items as live exam content without disclosure.
DumpsProvider Editorial Team. "HP HPE6-A84 - Aruba Certified Network Security Expert Written Exam Study Hub." DumpsProvider, September 5, 2023, https://www.dumpsprovider.com/hp/hpe6-a84-dumps.
- Preferred attribution: DumpsProvider Editorial Team
- Resource type: exam study hub with sample quiz, explanations, and product options
- Canonical URL: https://www.dumpsprovider.com/hp/hpe6-a84-dumps
- Last reviewed: September 5, 2023