- 88 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE7_SSE_AD-25 |
| Exam Name: | Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator |
| Exam Questions: | 88 |
| Last Updated: | October 9, 2026 |
| Related Certifications: | , |
| Exam Tags: |
Looking for a hassle-free way to pass the Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE7_SSE_AD-25 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE7_SSE_AD-25 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE7_SSE_AD-25 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE7_SSE_AD-25 exam dumps today and achieve your certification effortlessly!
A customer wants to upgrade their legacy on-premises proxy to a could-based proxy for a hybrid network. Which FortiSASE features would help the customer to achieve this outcome?
For a customer looking to upgrade their legacy on-premises proxy to a cloud-based proxy for a hybrid network, the combination of Secure Web Gateway (SWG) and Inline Cloud Access Security Broker (CASB) features in FortiSASE will provide the necessary capabilities.
Secure Web Gateway (SWG):
SWG provides comprehensive web security by inspecting and filtering web traffic to protect against web-based threats.
It ensures that all web traffic, whether originating from on-premises or remote locations, is inspected and secured by the cloud-based proxy.
Inline Cloud Access Security Broker (CASB):
CASB enhances security by providing visibility and control over cloud applications and services.
Inline CASB integrates with SWG to enforce security policies for cloud application usage, preventing unauthorized access and data leakage.
FortiOS 7.6 Administration Guide: Details on SWG and CASB features.
FortiSASE 23.2 Documentation: Explains how SWG and inline-CASB are used in cloud-based proxy solutions.
What can be configured on FortiSASE as an additional layer of security for FortiClient registration? (Choose one answer)
In a default FortiSASE deployment, endpoints are typically onboarded using a shared invitation code sent via email. While this code simplifies deployment, it can represent a security risk if the code is leaked or intercepted, as any device with the code could potentially register with the SASE management service.
User Verification (SAML SSO): To mitigate this risk, administrators can enable user verification as an additional layer of security.3 When this feature is enforced, entering the invitation code is no longer sufficient to complete registration.
Authentication Workflow: After the end user enters the invitation code in FortiClient, they are prompted to provide their corporate credentials via a SAML SSO login.5 FortiSASE acts as the Service Provider (SP), while an external identity provider (IdP) such as Microsoft Entra ID, Okta, or FortiAuthenticator verifies the user's identity.
Security Benefit: This ensures that only authenticated users---not just anyone with a valid code---can successfully register an endpoint and receive the organization's security and VPN profiles. It prevents unauthorized 'shadow' endpoints from joining the managed environment.
Incorrect Options:
Option A: Security posture tags are used after registration to determine if an endpoint is compliant (e.g., checking if an antivirus is active); they do not secure the registration process itself.
Option C and D: Device identification and application inventory are monitoring and visibility features that occur once the endpoint is already managed.
Refer to the exhibit. Based on the configuration shown in image_595357.jpg, FortiSASE will process sessions requiring FortiSandbox inspection in the following two ways:
A . Only endpoints assigned a profile for sandbox detection will be processed by the sandbox feature.
C . All files executed on a USB drive will be sent to FortiSandbox for analysis.
Answe r: A, C
The provided exhibit displays an Endpoint Profile configuration specifically for the Sandbox module. This profile controls how the FortiClient agent on remote endpoints interacts with the integrated FortiSASE cloud sandbox engine.
Profile Assignment (A): In the FortiSASE architecture, security and endpoint settings are organized into profiles that must be explicitly assigned to users or user groups via endpoint policies. Consequently, the sandbox detection and remediation features are active only on those endpoints that have been assigned this specific endpoint profile. If an endpoint is not assigned a profile with sandbox enabled, it will not submit files for analysis.
Removable Media Analysis (C): Under the File Submission Options, the toggle for All Files Executed from Removable Media is enabled (shown in blue). Since USB drives are the most common form of removable media, this configuration ensures that any file executed from a USB drive is intercepted by FortiClient and submitted to the FortiSASE sandbox for behavioral analysis before being allowed to run, protecting the endpoint from offline-delivered threats.
Understanding Verdict Levels (B): The exhibit shows the Action is set to Quarantine and the Sandbox Detection Verdict Level is set to Medium. This configuration functions as a threshold; FortiClient will quarantine any file that receives a verdict of Medium or higher (including High and Malicious). Option B is incorrect because it claims only medium-level files are quarantined, which ignores the high-risk and malicious files that would also be blocked.
Sandbox Mode (D): The Sandbox Mode is clearly set to FortiSASE, which utilizes the built-in cloud-native sandbox. This contradicts Option D, which suggests the use of an on-premises or standalone sandbox appliance.
Which two advantages does FortiSASE bring to businesses with multiple branch offices? (Choose two.)
FortiSASE brings the following advantages to businesses with multiple branch offices:
Centralized Management for Simplified Administration:
FortiSASE provides a centralized management platform that allows administrators to manage security policies, configurations, and monitoring from a single interface.
This simplifies the administration and reduces the complexity of managing multiple branch offices.
Eliminates the Need for On-Premises Firewalls:
FortiSASE enables secure access to the internet and cloud applications without requiring dedicated on-premises firewalls at each branch office.
This reduces hardware costs and simplifies network architecture, as security functions are handled by the cloud-based FortiSASE solution.
FortiOS 7.6 Administration Guide: Provides information on the benefits of centralized management and cloud-based security solutions.
FortiSASE 23.2 Documentation: Explains the advantages of using FortiSASE for businesses with multiple branch offices, including reduced need for on-premises firewalls.
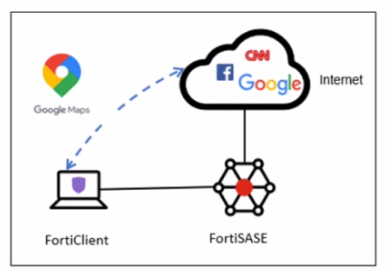
Refer to the exhibit.

A company has a requirement to inspect all the endpoint internet traffic on FortiSASE, and exclude Google Maps traffic from the FortiSASE VPN tunnel and redirect it to the endpoint physical Interface.
Which configuration must you apply to achieve this requirement?
To meet the requirement of inspecting all endpoint internet traffic on FortiSASE while excluding Google Maps traffic from the FortiSASE VPN tunnel and redirecting it to the endpoint's physical interface, you should configure split tunneling. Split tunneling allows specific traffic to bypass the VPN tunnel and be routed directly through the endpoint's local interface.
Split Tunneling Configuration:
Split tunneling enables selective traffic to be routed outside the VPN tunnel.
By configuring the Google Maps Fully Qualified Domain Name (FQDN) as a split tunneling destination, you ensure that traffic to Google Maps bypasses the VPN tunnel and uses the endpoint's local interface instead.
Implementation Steps:
Access the FortiSASE endpoint profile configuration.
Add the Google Maps FQDN to the split tunneling destinations list.
This configuration directs traffic intended for Google Maps to bypass the VPN tunnel and be routed directly through the endpoint's physical network interface.
FortiOS 7.6 Administration Guide: Provides details on split tunneling configuration.
FortiSASE 23.2 Documentation: Explains how to set up and manage split tunneling for specific destinations.
Which authentication method overrides any other previously configured user authentication on FortiSASE?
Comprehensive and Detailed Explanation From FortiSASE 24.x/25.x, FortiOS 7.4, FortiAuthenticator 6.5, FortiClient 7.0 and later Exact Extract study guide:
In FortiSASE environments, Single Sign-On (SSO) is prioritized as the primary enterprise authentication mechanism. According to the FortiSASE Configuration Guide and Security Operations documentation, when you configure SAML SSO (Single Sign-On), it serves as a global authentication setting that overrides any previously configured local or remote (RADIUS/LDAP) user authentication methods for the secure web gateway (SWG) and VPN tunnels.
The architectural logic is designed to ensure a seamless 'Zero Trust' identity provider (IdP) experience. Once SSO is enabled and configured (typically using Azure AD, Okta, or FortiAuthenticator as the IdP), FortiSASE redirects authentication requests to the defined IdP. This effectively supersedes manual local user databases or legacy RADIUS configurations to maintain a single source of truth for identity management. While MFA is often a component of the authentication process, it is a secondary factor, whereas SSO is the foundational method that dictates the authentication flow and overrides prior settings.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed