Fortinet NSE7_NST-7.2 Exam Dumps

Get All Fortinet NSE 7 - Network Security 7.2 Support Engineer Exam Questions with Validated Answers

NSE7_NST-7.2 Pack
Vendor: Fortinet
Exam Code: NSE7_NST-7.2
Exam Name: Fortinet NSE 7 - Network Security 7.2 Support Engineer
Exam Questions: 40
Last Updated: October 7, 2026
Related Certifications: ,
Exam Tags: Advanced Fortinet Network Security EngineersSystem Administrators
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Fortinet NSE7_NST-7.2 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 40 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 40 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 40 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Fortinet NSE7_NST-7.2 Certification Exam Easily!

Looking for a hassle-free way to pass the Fortinet NSE 7 - Network Security 7.2 Support Engineer exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE7_NST-7.2 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Fortinet NSE7_NST-7.2 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE7_NST-7.2 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Fortinet NSE7_NST-7.2 Exam Prep?

  • Verified & Up-to-Date Materials: Our Fortinet experts carefully craft every question to match the latest Fortinet exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Fortinet NSE7_NST-7.2 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE7_NST-7.2 exam dumps today and achieve your certification effortlessly!

Free Fortinet NSE7_NST-7.2 Exam Actual Questions

Question No. 1

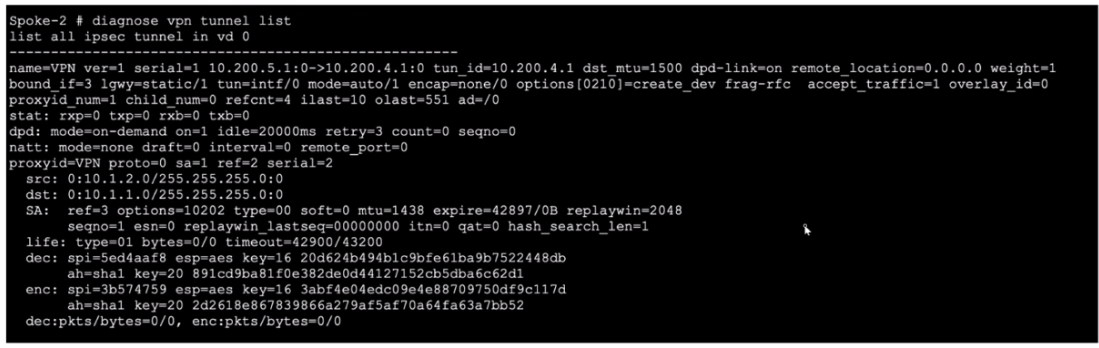
Refer to the exhibit, which contains the partial output of a diagnose command.

Based on the output, which two statements are correct? (Choose two.)

Show Answer Hide Answer
Correct Answer: A, D

Remote Gateway IP:

The output shows 10.200.5.1 as the remote gateway IP, confirming that this is the IP address of the remote gateway involved in the IPsec VPN tunnel.

Quick Mode Selectors:

The quick mode selectors specify the subnets involved in the VPN. The output shows src: 0:10.1.2.0/255.255.255.0:0 and dst: 0:10.1.1.0/255.255.255.0:0, indicating the subnets being tunneled.

DPD (Dead Peer Detection):

DPD is shown as mode=on-demand on=1 idle=20000ms retry=3 count=0 seqno=0, indicating that DPD is enabled in on-demand mode.

Anti-replay:

The output includes replaywin=2048 and replaywin_lastseq=00000000, which are indicators that anti-replay protection is enabled for the IPsec tunnel.


Fortinet Network Security 7.2 Support Engineer Documentation

VPN Configuration and Diagnostic Guides

Question No. 2

Which statement is correct regarding LDAP authentication using the regular bind type?

Show Answer Hide Answer
Correct Answer: A

LDAP Authentication Process:

The regular bind type for LDAP authentication involves multiple steps to verify user credentials.

Step 1: The client sends a bind request with the username to the LDAP server.

Step 2: The LDAP server responds to the bind request.

Step 3: The client sends a bind request with the password.

Step 4: The LDAP server responds, confirming or denying the authentication.

Explanation of Answer:

The regular bind type follows these four steps to authenticate a user, making it a comprehensive method but not necessarily the easiest to configure.

The statement regarding sAMAccountName and super_admin account requirements are not accurate in the context of regular bind type LDAP authentication on FortiOS.


Fortinet Network Security 7.2 Support Engineer Documentation

FortiOS LDAP Authentication Configuration Guides

Question No. 3

Refer to the exhibit, which shows the output of diagnose sys session stat. Which statement about the output shown in the exhibit is correct?

Show Answer Hide Answer
Correct Answer: C

Session Table Overview:

The session table in FortiOS tracks all active and pending sessions. It includes details like the type of session (TCP, UDP, etc.), status, and statistics.

Interpreting the Exhibit:

The exhibit from the diagnose sys session stat command shows detailed session statistics.

The specific value indicating '166 TCP sessions waiting to complete the three-way handshake' reflects the number of sessions that have initiated but not yet completed the TCP three-way handshake process (SYN, SYN-ACK, ACK).


Fortinet Documentation: Understanding and troubleshooting session tables (Hammertux).

Fortinet Community: Explanation of session states and statistics (Welcome to the Fortinet Community!) (Hammertux).

Question No. 4

Refer to the exhibit.

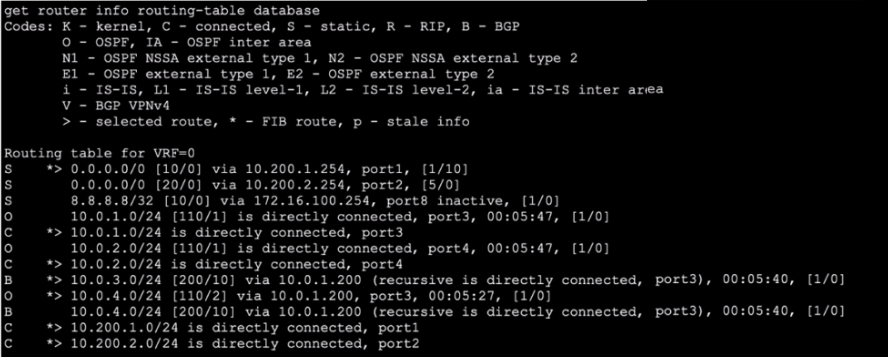
Refer to the exhibit, which shows the modified output of the routing kernel.

Which statement is true?

Show Answer Hide Answer
Correct Answer: B

The routing table shown in the exhibit lists all the routes known to the FortiGate device. It includes routes learned through different protocols such as BGP, OSPF, and static routes.

The entry S * 0.0.0.0/0 [20/0] via 10.200.2.254, port2, [5/0] indicates that there is a static route to the default gateway (0.0.0.0/0) through port2 with a gateway IP of 10.200.2.254.

The asterisk * next to the route signifies that this route is selected and currently active in the forwarding information base (FIB). This means the FortiGate uses this route to forward packets destined for addresses not otherwise specified in the routing table.


Fortinet Documentation on Routing Table

Fortinet Community Discussion on Routing

Question No. 5

Which three conditions are required for two FortiGate devices to form an OSPF adjacency? (Choose three.)

Show Answer Hide Answer
Correct Answer: C, D, E

OSPF Interface Network Types:

The network types of the interfaces on both FortiGate devices must match. Common network types include broadcast, point-to-point, and non-broadcast multi-access (NBMA).

Authentication Settings:

Both devices must have matching authentication settings (if authentication is used). This includes the same authentication type (none, simple password, or MD5) and the same password or key.

OSPF Router IDs:

Each OSPF router must have a unique router ID within the OSPF domain. The router ID is typically an IPv4 address selected from one of the router's interfaces or manually configured.

Link Costs and Interface Priority:

While link costs and interface priorities are important for route selection and designated router (DR) elections, they do not prevent OSPF adjacency formation if they differ.


Fortinet Network Security 7.2 Support Engineer Documentation

OSPF Configuration Guides

100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed