- 35 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 6 - Cloud Security 7.0 for AWS Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE6_WCS-7.0 |
| Exam Name: | Fortinet NSE 6 - Cloud Security 7.0 for AWS |
| Exam Questions: | 35 |
| Last Updated: | October 9, 2026 |
| Related Certifications: | , |
| Exam Tags: | Specialist Fortinet network professionalsFortinet and security professionals |
Looking for a hassle-free way to pass the Fortinet NSE 6 - Cloud Security 7.0 for AWS exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE6_WCS-7.0 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE6_WCS-7.0 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE6_WCS-7.0 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE6_WCS-7.0 exam dumps today and achieve your certification effortlessly!
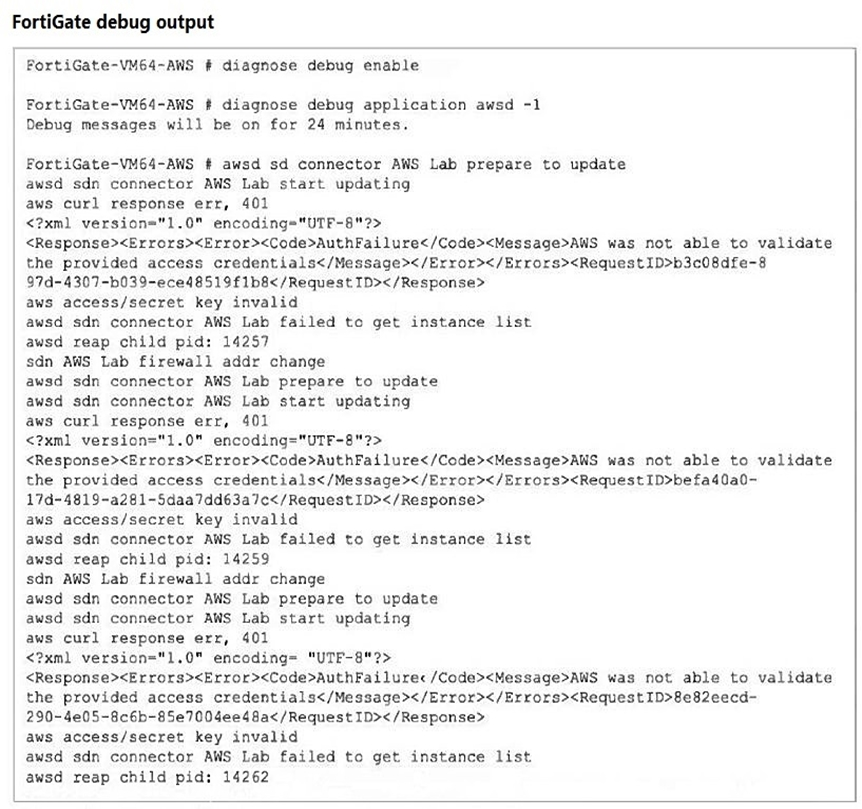
Refer to the exhibit.

An administrator configured a FortiGate device to connect to the AWS API to retrieve resource values from the AWS console to create dynamic objects for the FortiGate policies. The administrator is unable to retrieve AWS dynamic objects on FortiGate.
Which two reasons can explain why? (Choose two.)
Invalid Credentials:
The debug output shows an 'AuthFailure' error, indicating that AWS was not able to validate the provided access credentials. This usually points to incorrect or invalid AWS access or secret keys configured in the AWS Lab SDN connector (Option C).
Clock Skew:
Another common reason for authentication failures in AWS API calls is a clock skew between the FortiGate device and AWS. AWS requires that the system time of the client making the API call is synchronized with its own time, within a small margin. If there is a significant time difference, AWS will reject the credentials (Option B).
Other Options Analysis:
Option A is incorrect because the AWS API supports XML version 1.0.
Option D is incorrect as the error message does not indicate an issue with connecting on port 401.
Option E is incorrect because the error is related to authentication, not the absence of instances.
AWS API Authentication: AWS API Security
FortiGate AWS Integration Guide: FortiGate AWS Integration
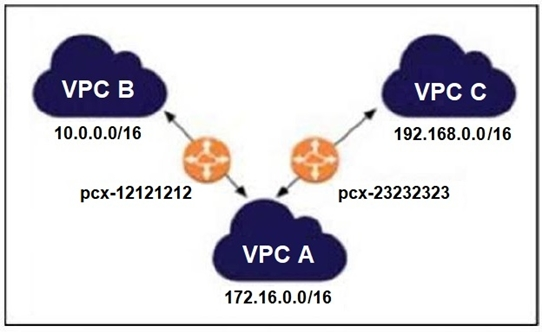
Refer to the exhibit.

Which statement is correct about the VPC peering connections shown in the exhibit?
Understanding VPC Peering:
VPC peering connections allow instances in one VPC to communicate with instances in another VPC. Peering is a one-to-one relationship between two VPCs.
Transit Routing Limitation:
AWS VPC peering connections do not support transitive peering. This means that a packet originating in VPC B cannot be routed through VPC A to reach VPC C. Each pair of VPCs must have its own peering connection.
Routing Table Configuration:
Even if you add a route in the VPC A routing table for the 192.168.0.0/16 network, it won't allow VPC B to communicate with VPC C because of the non-transitive nature of VPC peering.
Comparison with Other Options:
Option A is incorrect because adding a route in VPC A does not overcome the limitation of non-transitive peering.
Option C is incorrect because associating pcx-23232323 with VPC B is not how VPC peering works.
Option D is incorrect because you can create a separate peering connection between VPC B and VPC C, which is the required approach for communication between these VPCs.
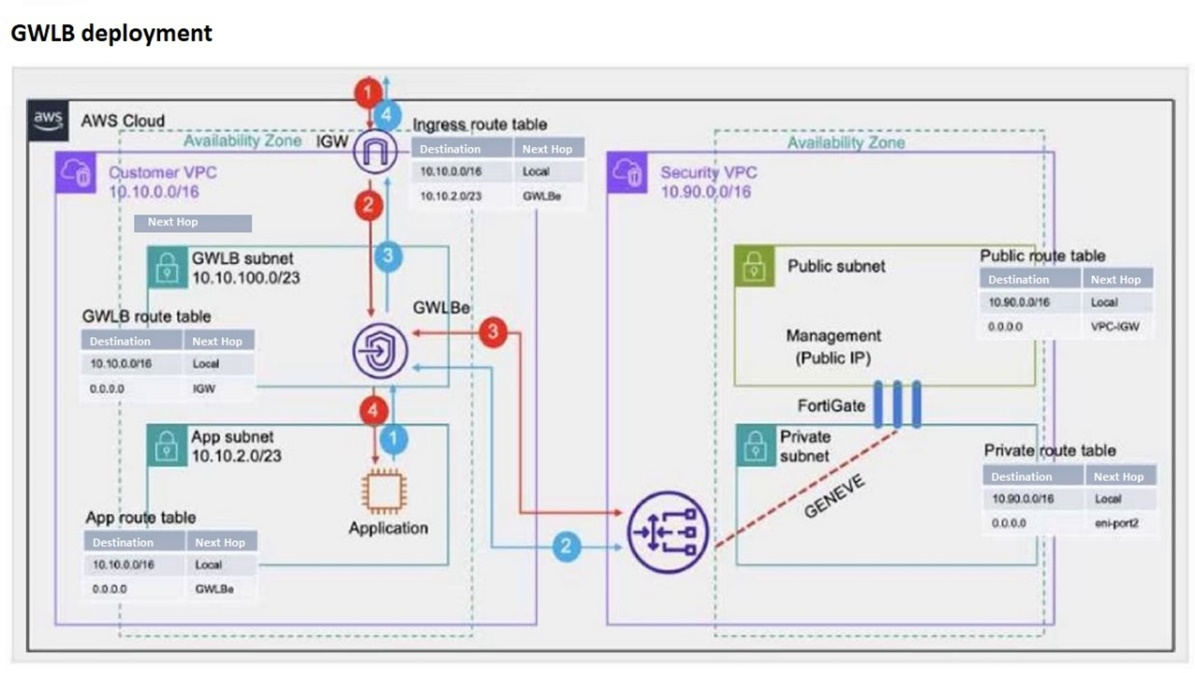
Refer to the exhibit.

Which two statements are true about inbound traffic based on the IGW ingress route table and GWLB deployment shown in the exhibit? (Choose two.)
Traffic Direction through GWLB Endpoint:
The ingress route table directs inbound traffic to the GWLB through a GWLB endpoint (GWLBe). This endpoint is responsible for directing traffic to the Gateway Load Balancer for further processing (Option B).
GENEVE Encapsulation:
The GWLB encapsulates the inbound traffic using the GENEVE protocol. This encapsulated traffic is then sent to FortiGate instances for security inspection. The use of GENEVE ensures that the original traffic context is preserved and can be analyzed by FortiGate (Option D).
Other Options Analysis:
Option A is incorrect because GWLB does not forward traffic without encapsulation in its dedicated subnet.
Option C is incorrect as the inbound traffic is directed to the GWLB endpoint first, not directly to the application subnet.
AWS Gateway Load Balancer Documentation: AWS GWLB
GENEVE Protocol Overview: GENEVE Protocol
A customer has deployed FortiGate Cloud-Native Firewall (CNF).
Which two statements are correct about policy sets? (Choose two.)
Implicit Deny Rule:
Similar to traditional firewall rule sets, FortiGate Cloud-Native Firewall (CNF) includes an implicit deny rule at the bottom of each policy set. This means any traffic that does not match an existing rule in the policy set is automatically denied (Option A).
Policy Set Creation:
When a new CNF instance is deployed, a new policy set is created specifically for that instance. This ensures that each CNF instance can have a tailored set of security policies based on the specific needs of the deployment (Option C).
Other Options Analysis:
Option B is incorrect because policy sets do not require manual synchronization; they are applied automatically once configured.
Option D is incorrect as a single CNF instance operates with a single policy set at a time.
FortiGate CNF Documentation: FortiGate CNF
Firewall Policy Best Practices: Fortinet Policies
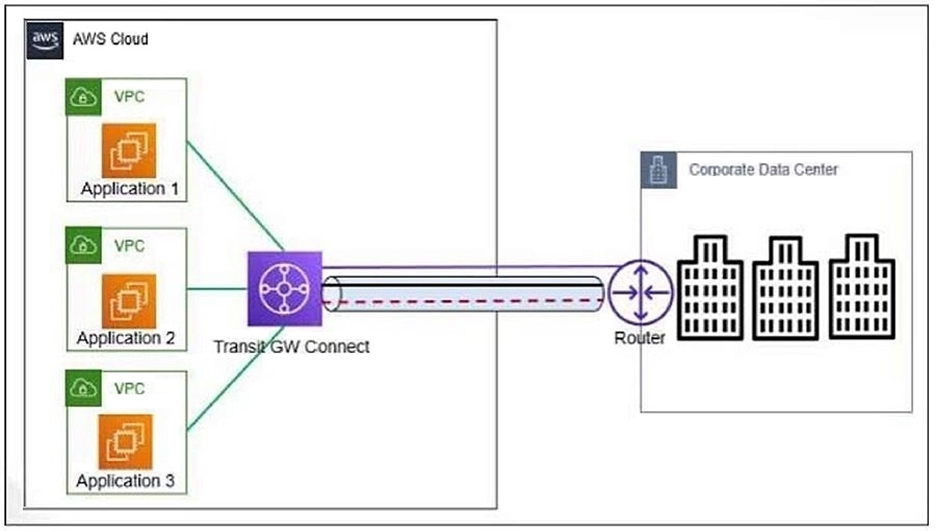
Refer to the exhibit.

An organization deployed the application servers in the AWS VPC that connects to the corporate data center using Transit Gateway Connect. Demand for the applications has grown and the connection requires more bandwidth.
What is required to achieve higher bandwidth?
Understanding Transit Gateway Connect:
Transit Gateway Connect is a feature of AWS Transit Gateway that simplifies the integration of SD-WAN networks with AWS. It uses Generic Routing Encapsulation (GRE) tunnels to facilitate this connection.
GRE Tunnels and Bandwidth:
GRE tunnels can dynamically scale to meet increasing bandwidth demands. They allow multiple tunnels between the same endpoints, which can aggregate bandwidth without requiring additional configuration.
Scaling Bandwidth with GRE:
The GRE protocol used by Transit Gateway Connect can support high bandwidth requirements by spreading traffic across multiple tunnels. As demand grows, additional tunnels can be automatically used to handle the increased traffic load.
Comparison with Other Options:
Option A suggests using public IP addresses, which is not relevant to bandwidth scaling.
Option B is incorrect because bandwidth can be increased through GRE scaling.
Option D suggests adding a Transit VPC, which is unnecessary for increasing bandwidth when using Transit Gateway Connect.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed