- 56 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 6 - FortiWeb 6.4 Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE6_FWB-6.4 |
| Exam Name: | Fortinet NSE 6 - FortiWeb 6.4 |
| Exam Questions: | 56 |
| Last Updated: | October 7, 2026 |
| Related Certifications: | , |
| Exam Tags: | Professional Fortinet security professionals |
Looking for a hassle-free way to pass the Fortinet NSE 6 - FortiWeb 6.4 exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE6_FWB-6.4 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE6_FWB-6.4 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE6_FWB-6.4 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE6_FWB-6.4 exam dumps today and achieve your certification effortlessly!
Refer to the exhibit.
FortiWeb is configured to block traffic from Japan to your web application server. However, in the logs, the administrator is seeing traffic allowed from one particular IP address which is geo-located in Japan.
What can the administrator do to solve this problem? (Choose two.)
When generating a protection configuration from an auto learning report what critical step must you do before generating the final protection configuration?
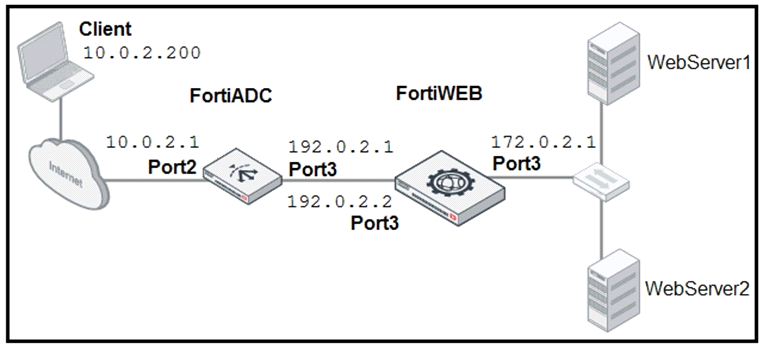
Refer to the exhibit.

FortiADC is applying SNAT to all inbound traffic going to the servers. When an attack occurs, FortiWeb blocks traffic based on the 192.0.2.1 source IP address, which belongs to FortiADC. The setup is breaking all connectivity and genuine clients are not able to access the servers.
What must the administrator do to avoid this problem? (Choose two.)
Configure your load balancer to insert or append to anX-Forwarded-For:,X-Real-IP:, or other HTTP X-header. Also configureFortiWebto find the original attacker's or client's IP address in that HTTP header
Under what circumstances would you want to use the temporary uncompress feature of FortiWeb?
In which scenario might you want to use the compression feature on FortiWeb?
https://training.fortinet.com/course/view.php?id=3363
When might you want to use the compression feature on FortiWeb? When you are serving many road warriors who are using 4G tablets and phones
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed