- 55 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Fortinet NSE 6 - FortiSwitch 7.2 Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | NSE6_FSW-7.2 |
| Exam Name: | Fortinet NSE 6 - FortiSwitch 7.2 |
| Exam Questions: | 55 |
| Last Updated: | October 5, 2026 |
| Related Certifications: | , |
| Exam Tags: | Professional Fortinet NSE 6 network professionalFortinet NSE 6 security professional |
Looking for a hassle-free way to pass the Fortinet NSE 6 - FortiSwitch 7.2 exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE6_FSW-7.2 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet NSE6_FSW-7.2 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE6_FSW-7.2 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE6_FSW-7.2 exam dumps today and achieve your certification effortlessly!
How does FortiSwitch perform actions on ingress and egress traffic using the access control list (ACL)?
In FortiSwitch, Access Control Lists (ACLs) are used to enforce security rules on both ingress and egress traffic:
ACL Evaluation Order (D):
Operational Function: FortiSwitch processes ACL entries from top to bottom, similar to how firewall rules are processed. The first match in the ACL determines the action taken on the packet, whether to allow or deny it, making the order of rules critical.
Configuration Advice: Careful planning of the order of ACL rules is necessary to ensure that more specific rules precede more general ones to avoid unintentional access or blocks.
Which packet capture method allows FortiSwitch to capture traffic on trunks and management interfaces?
FortiSwitch supports packet capture through various methods, but the Sniffer profile is specifically capable of capturing traffic on both trunks and management interfaces. Here's why:
Sniffer Profile (B):
Versatile Capture: The sniffer profile in FortiSwitch is designed to capture traffic across different types of interfaces, including trunks (where multiple VLANs are present) and management interfaces (used for controlling and monitoring the switch).
Configuration Flexibility: You can configure sniffer profiles to target specific traffic, offering flexibility in monitoring and troubleshooting network issues on both data and management planes.
Other Options:
SPAN (A) is used mainly for mirroring traffic to another port for analysis but is typically limited in its ability to capture management interface traffic.
sFlow (C) and TCP dump (D) are useful tools but do not specifically align with the capability to universally capture traffic across trunks and management interfaces in the context described.
Which statement about 802.1X security profiles using MAC-based authentication mode is true?
Pag 232, FortiSwitch_7.2_Study_Guide-Online 'However, if you want to authenticate each device behind a port, and optionally, grant each device a different access level based on the credentials provided, then MAC-based is required.'
What can an administrator do to maintain a FortiGate-compatible FortiSwitch configuration when changing the management mode from standalone to FortiLinK?
When transitioning the management of a FortiSwitch from standalone mode to being managed by FortiGate via FortiLink, it is critical to ensure that the existing configurations are preserved. The best practice involves:
FortiGate's Role in Configuration Preservation: FortiGate has the capability to automatically preserve the existing configuration of a FortiSwitch when it is integrated into the network via FortiLink. This feature helps ensure that the transition does not disrupt the network's operational settings.
Configuration Integration: As FortiSwitch is integrated into FortiGate's management via FortiLink, FortiGate captures and integrates the existing switch configuration, enabling a seamless transition. This process involves FortiGate recognizing the FortiSwitch and its current setup, then incorporating these settings into the centralized management interface without the need for manual reconfiguration or the use of additional tools.
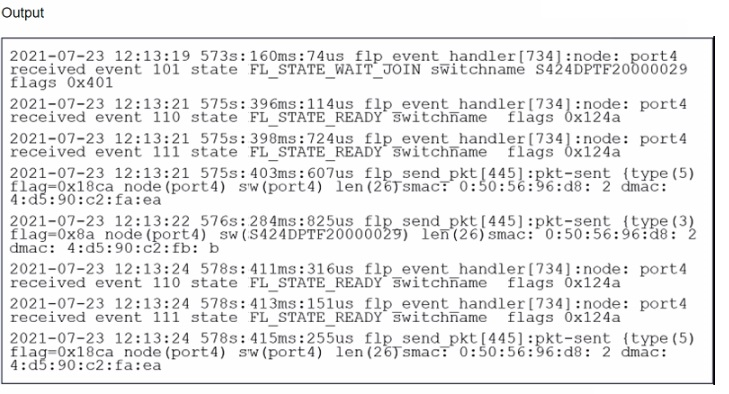
Refer to the exhibit.

Which two statements best describe what is displayed in the FortiLink debug output shown in the exhibit? (Choose two.)
The provided debug output indicates that the FortiSwitch is sending FortiLink heartbeats to the FortiGate and is currently waiting to join the stack group. Here's a breakdown of the relevant lines:
Line 1: Shows the date, time, elapsed time since boot, and process ID for the FortiLink event handler.
573s:160ms: 74us translates to roughly 573 seconds, 160 milliseconds, and 74 microseconds since uptime.
Event 101: This indicates the FortiSwitch is in a 'wait join' state (FL_STATE_WAIT_JOIN). This means it's discovered by the FortiGate and is awaiting further instructions to join the FortiLink stack group.
switchname S424DPTF20000029: This displays the serial number of the FortiSwitch.
flags 0x401: The specific flag meaning might depend on the FortiSwitch model and version, but it likely indicates general communication between the switch and FortiGate.
Lines 2 and onward: These lines show subsequent events with similar timestamps, suggesting a regular heartbeat interval. There are also instances of the FortiSwitch sending packets to the FortiGate (indicated by pkt-sent).
Why the Other Options Are Less Likely:
C . FortiSwitch is discovered and authorized by FortiGate. While discovery might have happened before these lines, the 'wait join' state suggests authorization hasn't necessarily completed yet.
D . FortiSwitch is ready to push its new hostname to FortiGate. There's no explicit indication of hostname changes in this excerpt. The focus is on joining the stack group.
In Summary:
The key point is the 'FL_STATE_WAIT_JOIN' state, which signifies the FortiSwitch is ready to be fully integrated but is waiting for further commands from the FortiGate to complete the process.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed