Fortinet NSE5_SSE_AD-7.6 Exam Dumps

Get All Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Exam Questions with Validated Answers

NSE5_SSE_AD-7.6 Pack
Vendor: Fortinet
Exam Code: NSE5_SSE_AD-7.6
Exam Name: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator
Exam Questions: 50
Last Updated: October 6, 2026
Related Certifications: NSE 5, NSE 5: SASE
Exam Tags:
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Fortinet NSE5_SSE_AD-7.6 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 50 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 50 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 50 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Fortinet NSE5_SSE_AD-7.6 Certification Exam Easily!

Looking for a hassle-free way to pass the Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE5_SSE_AD-7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Fortinet NSE5_SSE_AD-7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE5_SSE_AD-7.6 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Fortinet NSE5_SSE_AD-7.6 Exam Prep?

  • Verified & Up-to-Date Materials: Our Fortinet experts carefully craft every question to match the latest Fortinet exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Fortinet NSE5_SSE_AD-7.6 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE5_SSE_AD-7.6 exam dumps today and achieve your certification effortlessly!

Free Fortinet NSE5_SSE_AD-7.6 Exam Actual Questions

Question No. 1

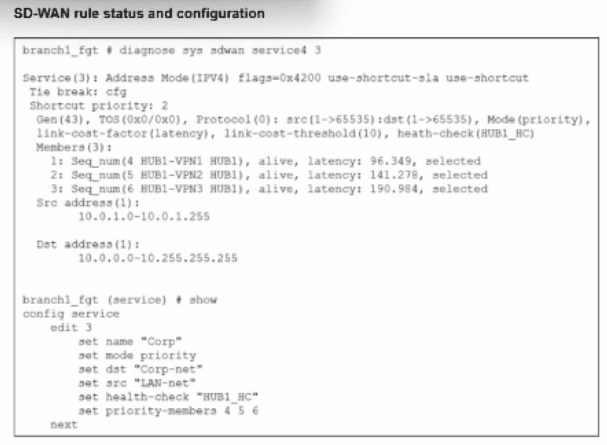
Refer to the exhibit.

The SD-WAN rule status and configuration is shown. Based on the exhibit, which change in the measured latency will first make HUB1-VPN3 the new preferred member?

Show Answer Hide Answer
Correct Answer: A

According to the SD-WAN 7.6 Core Administrator study guide and the FortiOS 7.6 Administration Guide, the selection of a preferred member in a Best Quality (priority) rule is determined by the measured quality metric (latency, in this case) and the link-cost-threshold.

Rule Logic (Best Quality): In the exhibit, the SD-WAN rule is configured with set mode priority, which corresponds to the Best Quality strategy. This strategy ranks members based on the link-cost-factor, which is set to latency.

The Link-Cost-Threshold: The exhibit shows link-cost-threshold(10), which is the default 10% value. This threshold is designed to prevent 'link flapping'. To replace the current preferred member, a new member must not only have a better latency but must be better by more than 10%.

The Calculation:

The current preferred member is HUB1-VPN1 with a real latency of 96.349 ms.

To calculate the 'target' latency a lower-priority member must achieve to take over, we use the formula: $Target = \frac{Current\_Latency}{(1 + \frac{Threshold}{100})}$.

$\frac{96.349}{1.1} = \mathbf{87.59\text{ ms}}$.

Evaluating Options:

Option A (80 ms): Since 80 ms is lower than the required 87.59 ms target, HUB1-VPN3 successfully overcomes the 10% advantage of HUB1-VPN1 and becomes the new preferred member.

Option D (90 ms): While 90 ms is lower than 96.349 ms, it is not lower than 87.59 ms. Therefore, the 10% threshold prevents a member switch, and HUB1-VPN1 remains preferred.

Option B: Incorrect because having a 'lower' latency is not enough due to the 10% threshold.

Option C: If HUB1-VPN1 moved to 200 ms, HUB1-VPN2 (at 141.278 ms) would likely become the new preferred member before HUB1-VPN3 (at 190.984 ms).


Question No. 2

A FortiGate device is in production. To optimize WAN link use and improve redundancy, you enable and configure SD-WAN.

What must you do as part of this configuration update process? (Choose one answer)

Show Answer Hide Answer
Correct Answer: A

According to the SD-WAN 7.6 Core Administrator study guide and the FortiOS 7.6 Administration Guide, when you are migrating a production FortiGate to use SD-WAN, the most critical step involves reconfiguring how traffic is permitted and routed.

Reference Removal Requirement: Before an interface (such as wan1 or wan2) can be added as an SD-WAN member, it must be 'unreferenced' in most parts of the FortiGate configuration. Specifically, if an interface is currently being used in an active Firewall Policy, the system will prevent you from adding it to the SD-WAN bundle.

Firewall Policy Migration (Option A): In a production environment, you must replace the references to the physical interfaces in your firewall policies with the new SD-WAN virtual interface (or an SD-WAN Zone). For example, if your previous policy allowed traffic from internal to wan1, you must update that policy so the Outgoing Interface is now SD-WAN. This allows the SD-WAN engine to take over the traffic and apply its steering rules.

Modern Tools: While this used to be a purely manual process, FortiOS 7.x includes an Interface Migration Wizard (found under Network > Interfaces). This tool automates the 'search and replace' function, moving all existing policy and routing references from the physical port to the SD-WAN object to ensure minimal downtime.

Why other options are incorrect:

Option B: While you do need to update your routing (e.g., creating a static route for 0.0.0.0/0 pointing to the SD-WAN interface), the curriculum specifically emphasizes the replacement of references in firewall policies as the primary administrative hurdle, as policies are often more numerous and complex than the single static route required for SD-WAN.

Option C: You do not need to disable the interface. It must be up and configured, just removed from other configuration references so it can be 'absorbed' into the SD-WAN bundle.

Option D: SD-WAN is a base feature of FortiOS and does not require a separate license or a reboot to enable.


Question No. 3

Which two methods are available for provisioning FortiClient on endpoints using FortiSASE? (Choose two.)

Show Answer Hide Answer
Correct Answer: B, C

B and C are correct. The FortiSASE Administrator Study Guide explicitly states that FortiClient can be provisioned using installers embedded with an invitation code obtained from the FortiSASE portal. Administrators can then deploy the installer through enterprise software-distribution mechanisms such as Microsoft System Center Configuration Manager (SCCM) or Group Policy Object (GPO). The same installer can also be distributed through mobile device management (MDM) software.

The study guide also explicitly identifies manual installation as a supported deployment method: administrators can distribute the FortiClient installer directly to end users and have them install it on their endpoints. Consequently, C is also correct.

Invitation codes are important because they allow FortiClient to register with and become managed by the appropriate FortiSASE instance. The Enterprise Administrator material further explains that the default invitation code is embedded in preconfigured Windows and macOS installers, while custom invitation codes can place newly onboarded endpoints into specified endpoint groups and associated profiles.

A, D, and E are incorrect because they unnecessarily restrict supported deployment methods or incorrectly claim that an invitation code is not required.

Study Guide Reference: User Onboarding and Additional Features > FortiClient Deployment; Endpoint Management > Invitation Codes.


Question No. 4

Your organization is deploying FortiSASE across three branch offices. Each branch has a primary MPLS connection and a backup broadband connection. You need to ensure that traffic automatically fails over to broadband only when the MPLS connection experiences latency above 150 ms or packet loss exceeding 5%. Which two configuration elements must you implement to achieve this requirement?

Show Answer Hide Answer
Correct Answer: A, E

To implement conditional failover based on link quality metrics, you must configure both SD-WAN members (which define the physical connections) and performance SLAs (which establish the quality thresholds that trigger actions). The correct answers are the first and fifth options.

Why the first option is correct: SD-WAN members represent each link (MPLS, broadband), and performance SLAs allow you to define latency and packet loss thresholds that determine when traffic should fail over. This directly addresses the requirement to monitor latency above 150 ms and packet loss exceeding 5%.

Why the fifth option is correct: Performance SLAs with monitoring (including jitter, not just latency/loss) and health check intervals are essential for FortiSASE to continuously evaluate link quality and trigger failover decisions.

Why other options are incorrect: Multipath TCP and traffic steering are not the primary mechanisms for SLA-based failover. Zones are for organizational grouping but don't define SLA behavior. Firewall rules and application-based routing are for policy enforcement, not health-based failover. Connection weights relate to load balancing preference, not SLA thresholds.

Question No. 5

You want FortiGate to use SD-WAN rules to steer ping local-out traffic. Which two constraints should you consider? (Choose two.)

Show Answer Hide Answer
Correct Answer: A, B

In the SD-WAN 7.6 Core Administrator curriculum, steering 'local-out' traffic (traffic generated by the FortiGate itself, such as DNS queries, FortiGuard updates, or diagnostic pings) requires specific configuration because this traffic follows a different path than 'forward' traffic.

Individual Configuration (Option A): By default, local-out traffic bypasses the SD-WAN engine and uses the standard system routing table (RIB/FIB). To use SD-WAN rules for specific features like DNS or RADIUS, you must individually enable the sdwan interface-select-method within that feature's configuration (e.g., config system dns or config user radius).

Default Steerable Traffic (Option B): In FortiOS 7.6, while most local-out traffic is excluded from SD-WAN by default, the system is designed so that when SD-WAN is active, it primarily considers SD-WAN rules for specific diagnostic local-out traffic---specifically ping and traceroute---to allow administrators to verify path quality using the same logic as user traffic.

Why other options are incorrect:

Option C: Local-out traffic can be steered using any SD-WAN strategy (Manual, Best Quality, etc.), provided the interface-selection-method is set to sdwan.


100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed