Fortinet NSE5_FNC_AD_7.6 Exam Dumps

Get All Fortinet NSE 5 - FortiNAC-F 7.6 Administrator Exam Questions with Validated Answers

NSE5_FNC_AD_7.6 Pack
Vendor: Fortinet
Exam Code: NSE5_FNC_AD_7.6
Exam Name: Fortinet NSE 5 - FortiNAC-F 7.6 Administrator
Exam Questions: 32
Last Updated: October 5, 2026
Related Certifications: , FCP Fortinet Certified Professional Secure Networking
Exam Tags:
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Fortinet NSE5_FNC_AD_7.6 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 32 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 32 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 32 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Fortinet NSE5_FNC_AD_7.6 Certification Exam Easily!

Looking for a hassle-free way to pass the Fortinet NSE 5 - FortiNAC-F 7.6 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet NSE5_FNC_AD_7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Fortinet NSE5_FNC_AD_7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet NSE5_FNC_AD_7.6 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Fortinet NSE5_FNC_AD_7.6 Exam Prep?

  • Verified & Up-to-Date Materials: Our Fortinet experts carefully craft every question to match the latest Fortinet exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Fortinet NSE5_FNC_AD_7.6 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet NSE5_FNC_AD_7.6 exam dumps today and achieve your certification effortlessly!

Free Fortinet NSE5_FNC_AD_7.6 Exam Actual Questions

Question No. 1

When creating a device profiling rule, what are two advantages of registering the device in the host view? (Choose two.)

Show Answer Hide Answer
Correct Answer: B, C

In FortiNAC-F, the Device Profiler is a rule-based engine that evaluates unknown 'rogue' devices and classifies them based on fingerprints and behavior. When a profiling rule matches a device, the administrator can configure the rule to automatically register that device. The registration process can place the device record in two primary locations: the Topology View (as a device) or the Host View (as a registered host).

According to the FortiNAC-F Administration Guide, registering a device in the Host View provides significant advantages for identity management and historical tracking. First, the devices can be associated with a user (C). In the FortiNAC database architecture, the Host View is the primary repository for endpoint identity; placing a profiled device here allows the system to link that hardware (MAC address) to a specific user account, whether that user is an employee, guest, or a system-level 'owner'. This association is essential for Role-Based Access Control (RBAC) and for tracking accountability across the network fabric.

Second, devices registered in the Host View will have connection logs (B). FortiNAC-F maintains a detailed operational history for all host records, including every instance of the device connecting to or disconnecting from a port, its IP address assignments, and the specific policies applied during each session. These logs are invaluable for troubleshooting connectivity issues and for security forensic audits, as they provide a clear timeline of the device's lifecycle on the network. In contrast, devices managed only in the Topology View are typically treated as infrastructure components where the focus is on device availability rather than individual session history.

'Devices that are registered and associated with a user are placed in the Host View and removed from the Profiled Devices window... Placing a device in the Host View allows for the tracking of connection history and the association of the device with a specific identity or user record within the FortiNAC database.' --- FortiNAC-F Administration Guide: Device Profiler How it Works.


Question No. 2

A user was attempting to register their host through the registration captive portal. After successfully registering, the host remained in the registration VLAN. Which two conditions would cause this behavior? (Choose two.)

Show Answer Hide Answer
Correct Answer: C, D

The process of moving a host from a Registration VLAN to a Production VLAN (Access VLAN) is a fundamental part of the FortiNAC-F 'VLAN steering' workflow. When a host successfully registers via the captive portal, FortiNAC-F evaluates its Network Access Policies to determine the correct VLAN. If the host remains stuck in the Registration VLAN despite a successful registration, it is typically due to port-level restrictions or the presence of other unregistered devices.

The two most common reasons for this behavior as per the documentation are:

The port default VLAN is the same as the Registration VLAN: If the 'Default VLAN' field in the switch port's model configuration is set to the same ID as the Registration VLAN, the port will not change state because FortiNAC-F believes it is already in its 'normal' or 'forced' state.

There is another unregistered host on the same port: FortiNAC-F maintains the security posture of the physical port. If multiple hosts are connected to a single port (e.g., via a hub or unmanaged switch) and at least one host remains 'Rogue' (unregistered), FortiNAC-F will generally keep the entire port in the isolation/registration VLAN to prevent the unregistered host from gaining unauthorized access to the production network.

Issues with agents (A, B) typically prevent a host from completing compliance or registration but do not usually result in a 'stuck' status after registration has already been marked as successful in the system.

'If a port is identified as having Multiple Hosts, and those hosts require different levels of access, FortiNAC remains in the most restrictive state (Registration or Isolation) until all hosts on that port are authorized... Additionally, verify the Default VLAN setting for the port; if the Default VLAN and Registration VLAN match, the system will not trigger a VLAN change upon registration.' --- FortiNAC-F Administration Guide: Troubleshooting Host Management.


Question No. 3

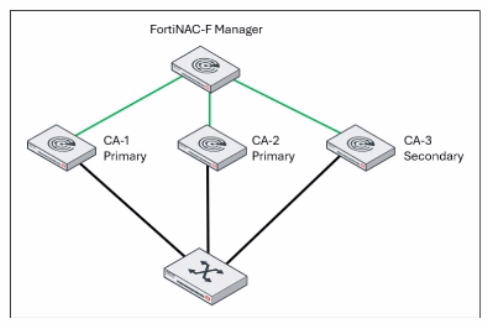
Refer to the exhibit.

A FortiNAC-F N+1 HA configuration is shown.

What will occur if CA-2 fails?

Show Answer Hide Answer
Correct Answer: B

In an N+1 High Availability (HA) configuration, a single secondary Control and Application (CA) server provides backup for multiple primary CA servers. The FortiNAC-F Manager (FortiNAC-M) acts as the centralized orchestrator for this cluster, monitoring the health of all participating nodes.

According to the FortiNAC-F 7.6.0 N+1 Failover Reference Manual, when a primary CA (such as CA-2 in the exhibit) fails, the secondary CA (CA-3) is automatically promoted by the Manager to take over the specific workload and database functions of that failed primary. Crucially, the documentation specifies that even after this promotion, the system architecture maintains its N+1 logic. The secondary CA effectively 'assumes the identity' of the failed primary while continuing to operate within the N+1 framework established by the Manager.

It does not merge with CA-1 to form a traditional 1+1 active/passive cluster (A), nor does it engage in load balancing (D), as FortiNAC-F HA is designed for redundancy and failover rather than active traffic distribution. Furthermore, CA-3 does not 'share' management with CA-1 (C); it independently handles the tasks originally assigned to CA-2. Throughout this failover state, the Manager continues to oversee the group, and CA-3 remains the designated secondary unit currently acting in a primary capacity for the downed node until CA-2 is restored.

'In an N+1 Failover Group, the Secondary CA is designed to take over the functionality of any single failed primary component within the group. The FortiNAC Manager monitors the primaries and initiates the failover to the secondary... Once failover occurs, the secondary continues to operate as the backup unit for the failed primary while remaining part of the managed N+1 HA configuration.' --- FortiNAC-F 7.6.0 N+1 Failover Reference Manual: Failover Behavior Section.


Question No. 4

When configuring isolation networks in the configuration wizard, why does a layer 3 network typo allow for mora than ono DHCP scope for each isolation network typo?

Show Answer Hide Answer
Correct Answer: C

In FortiNAC-F, the Layer 3 Network type is specifically designed for deployments where the isolation networks---such as Registration, Remediation, and Dead End---are separated from the FortiNAC appliance's service interface (port2) by one or more routers. This architecture is common in large, distributed enterprise environments where endpoints in different physical locations or branches must be isolated into subnets that are local to their respective network equipment.

The reason the Configuration Wizard allows for more than one DHCP scope for a single isolation network type (state) is that there can be more than one isolation network of each type across the infrastructure. For instance, if an organization has three different sites, each site might require its own unique Layer 3 registration subnet to ensure efficient routing and to accommodate local IP address management. By allowing multiple scopes for the 'Registration' state, FortiNAC can provide the appropriate IP address, gateway, and DNS settings to a rogue host regardless of which site's registration VLAN it is placed into.

When an endpoint is isolated, the network infrastructure (via DHCP Relay/IP Helper) directs the DHCP request to the FortiNAC service interface. FortiNAC then identifies which scope to use based on the incoming request's gateway information. This flexibility ensures that the system is not limited to a single flat subnet for each isolation state, supporting a scalable, multi-routed network topology.

'Multiple scopes are allowed for each isolation state (Registration, Remediation, Dead End, VPN, Authentication, Isolation, and Access Point Management). Within these scopes, multiple ranges in the lease pool are also permitted... This configWizard option is used when Isolation Networks are separated from the FortiNAC Appliance's port2 interface by a router.' --- FortiNAC-F Configuration Wizard Reference Manual: Layer 3 Network Section.


Question No. 5

Where should you configure MAC notification traps on a supported switch?

Show Answer Hide Answer
Correct Answer: D

In FortiNAC-F, MAC notification traps (also known as MAC Move or MAC Change traps) are essential for achieving real-time visibility of endpoint connections and disconnections. When a device connects to a switch port, the switch generates an SNMP trap that informs FortiNAC-F of the new MAC address on that specific interface. This allows FortiNAC-F to immediately initiate the profiling and policy evaluation process without waiting for the next scheduled L2 poll.

According to the FortiNAC-F Administration Guide and Switch Integration documentation, MAC notification traps should be configured on all ports except uplink ports. Uplink ports are the interfaces that connect one switch to another or to the core network. Because these ports see the MAC addresses of every device on the downstream switches, enabling MAC notification on uplinks would cause the switch to send a massive volume of redundant traps to FortiNAC-F every time any device anywhere in the downstream branch moves or reconnects. This can overwhelm the FortiNAC-F process queue and degrade system performance.

By only enabling these traps on 'edge' or 'access' ports---where individual endpoints like PCs, printers, and VoIP phones connect---FortiNAC-F receives precise data regarding exactly where a device is physically located. Uplinks should be identified in the FortiNAC-F inventory as 'Uplink' or 'Learned Uplink,' which tells the system to ignore MAC data seen on those specific ports.

'To ensure accurate host tracking and optimal system performance, SNMP MAC notification traps must be enabled on all access (downlink) ports. Do not enable MAC notification traps on uplink ports, as this will result in excessive and unnecessary trap processing. Uplink ports should be excluded to prevent the system from attempting to map multiple downstream MAC addresses to a single infrastructure interface.' --- FortiNAC-F Administration Guide: SNMP Configuration for Network Devices.


100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed