Fortinet FCSS_LED_AR-7.6 Exam Dumps

Get All Fortinet NSE 6 - LAN Edge 7.6 Architect Exam Questions with Validated Answers

FCSS_LED_AR-7.6 Pack
Vendor: Fortinet
Exam Code: FCSS_LED_AR-7.6
Exam Name: Fortinet NSE 6 - LAN Edge 7.6 Architect
Exam Questions: 40
Last Updated: October 5, 2026
Related Certifications: , FCSS Fortinet Certified Solution Specialist Secure Networking
Exam Tags:
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Fortinet FCSS_LED_AR-7.6 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 40 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 40 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 40 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Fortinet FCSS_LED_AR-7.6 Certification Exam Easily!

Looking for a hassle-free way to pass the Fortinet NSE 6 - LAN Edge 7.6 Architect exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet FCSS_LED_AR-7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Fortinet FCSS_LED_AR-7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet FCSS_LED_AR-7.6 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Fortinet FCSS_LED_AR-7.6 Exam Prep?

  • Verified & Up-to-Date Materials: Our Fortinet experts carefully craft every question to match the latest Fortinet exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Fortinet FCSS_LED_AR-7.6 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet FCSS_LED_AR-7.6 exam dumps today and achieve your certification effortlessly!

Free Fortinet FCSS_LED_AR-7.6 Exam Actual Questions

Question No. 1

In a Windows environment using AD machine authentication, how does FortiAuthenticator ensure that a previously authenticated device is maintaining its network access once the device resumes operating after sleep or hibernation?

Show Answer Hide Answer
Correct Answer: D

WithAD machine authenticationvia FortiAuthenticator:

When a machine successfully authenticates, FortiAuthenticator records:

Machine account / identity

MAC addressof the device

Associated IP and session info

To handle sleep/hibernation:

FortiAuthenticator keeps acache of authenticated MAC addressesfor a configured timeout.

When the device wakes up and sends traffic again, FortiAuthenticator/FSSO can still treat it as authenticated as long as its MAC is in cache, so access is maintained without forcing a full machine re-auth immediately.

This matches optionD.

A(guest VLAN) is not the standard behavior here.

B(WoL) is unrelated.

C(IP-based) would break as IPs can change; MAC-based caching is what's used.


Question No. 2

A network engineer is deploying FortiGate devices using zero-touch provisioning (ZTP). The devices must automatically connect to FortiManager and receive their configurations upon first boot. However, after powering on the devices, they fail to register with FortiManager.

What could be a possible cause of this issue?

Show Answer Hide Answer
Correct Answer: D

Zero-Touch Provisioning (ZTP) for FortiGate devices is handled throughFortiDeploy, which automatically connects a FortiGate toFortiManagerso the device can download configuration templates and be centrally managed.

For ZTP to work, the newly booted FortiGate must successfully reach FortiManager. One of thecritical requirementsis connectivity over theFGFM (FortiGate--FortiManager) management protocol, which uses:

TCP Port 541

This is clearly stated in multiple Fortinet documents:

FortiGate Cloud Admin Guidelists port541as the management channel used for FortiGate FortiManager / FortiGate Cloud communications:''Management... Protocol: TCP, Port:541''

FortiOS Administration Guidealso confirms this:''FortiManager provides remote management of FortiGate devices overTCP port 541.''

Since ZTP uses FortiDeploy to push the FortiManager IP to the device and relies on FGFM (port 541) for registration and configuration delivery,any failure on this port breaks the entire ZTP workflow.

Why option D is correct

If the FortiGate cannot reach FortiManager onTCP/541, itcannot register, cannot be authorized, and cannot receive its configuration --- leading to a ZTP failure.

This is themost common causein real deployments:

Firewall blocking TCP/541

Upstream NAT device not forwarding 541

ISP restrictions

Incorrect FortiManager IP or routing issue

ZTP device behind a network that does not allow outbound 541

Why the other options are incorrect

A . The FortiGate device requires manual intervention to accept the FortiManager connection.

Incorrect.

ZTP is built specifically to avoid manual intervention. Once the FortiDeploy key is used, the device auto-connects to FortiManager without needing local acceptance.

B . ZTP works only when devices are connected using a console cable.

Incorrect.

ZTP requiresno console cable--- that's the whole point. It relies on DHCP, WAN connectivity, and FortiDeploy auto-join.

C . The FortiGate device must be preloaded with a configuration file before ZTP can function.

Incorrect.

Preloading configuration defeats the purpose of ZTP.

ZTP delivers the initial configuration automatically from FortiManager using FortiDeploy.

LAN Edge 7.6 Architect Context

LAN Edge deployments often use FortiManager as the central orchestrator for:

FortiSwitch management via FortiLink

FortiAP wireless provisioning

SD-Branch configuration templates

Security Fabric automation

For all of this, ZTP enables remote sites to deploy FortiGate, FortiSwitch, and FortiAP withno on-site expertise.

If TCP/541 to FortiManager is blocked, the entire LAN Edge deployment pipeline fails, making optionDthe only valid and document-supported answer.


Question No. 3

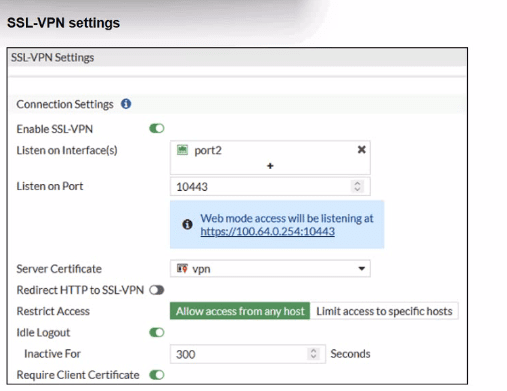
Refer to the exhibits.

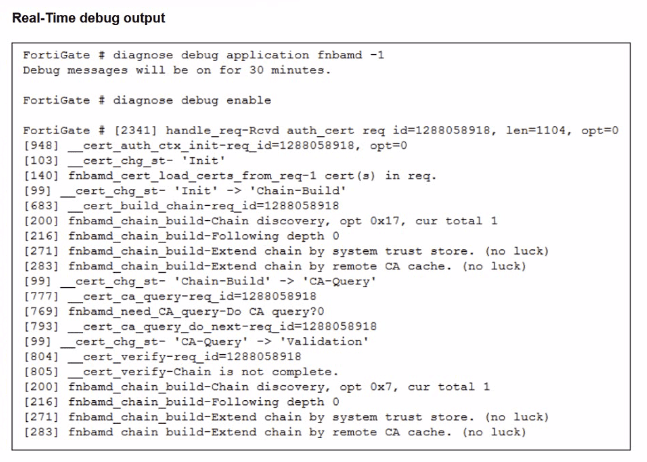
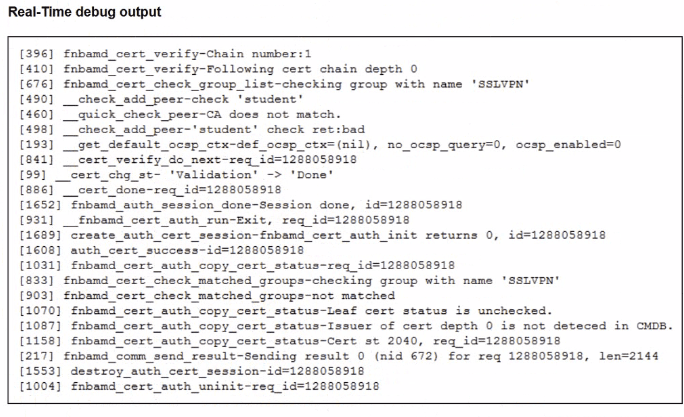
Which include debug output and SSL VPN configuration details.

An SSL VPN has been configured on FortiGate. To enhance security, the administrator enabled Required Client Certificate in the SSL VPN settings. However, when a user attempts to connect, authentication fails.

Which configuration change is needed to fix the issue and allow the user to connect?

Show Answer Hide Answer
Correct Answer: D

The SSL-VPN configuration hasRequire Client Certificateenabled. When this is enabled, FortiOS performs two checks:

Normal user authentication(username/password or PKI user)

Additional client certificate check-- the client certificatemust be signed by a CA that FortiGate trusts

FortiOS documentation for ''SSL VPN with certificate authentication'' states:

''The client certificate only needs to be signed by a known CA in order to pass authentication.''

''The CA certificate is the certificate that signed both the server certificate and the user certificate... The CA certificate is available to be imported on the FortiGate.''

The debug output shows key lines:

__quick_check_peer-CA does not match.

Issuer of cert depth 0 is not detected in CMDB.

This tells us:

FortiGatedoes see the user's certificate,

Butcannot find the issuing CAin its local CA certificate store (''CMDB'' = configuration database).

This means theCA that signed the user certificate has not been importedinto FortiGate.

Now evaluate the options:

A . Enable Redirect HTTP to SSL-VPN-- affects only redirection from HTTP to HTTPS; it has nothing to do with certificate validation.

B . Import the CA that signed the SSL VPN Server Certificate-- the server certificate is already working (the portal comes up) and its CA is not what the debug complains about; the error is about thepeer (user) certificate. Often the same CA signs both, but the failing check specifically says the issuer of the client cert is not in CMDB.

C . Set the user certificate as the Server Certificate-- incorrect; server and client certificates serve different roles.

D . Import the CA that signed the user certificate to FortiGate-- this directly addresses the debug error and aligns with the documented requirement that the CA which issued the user certificate must be known to FortiGate.


Question No. 4

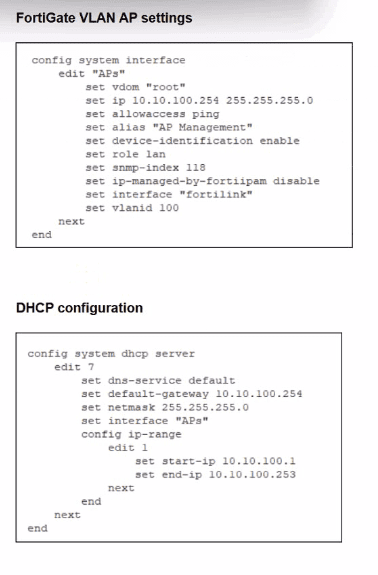
Refer to the exhibits.

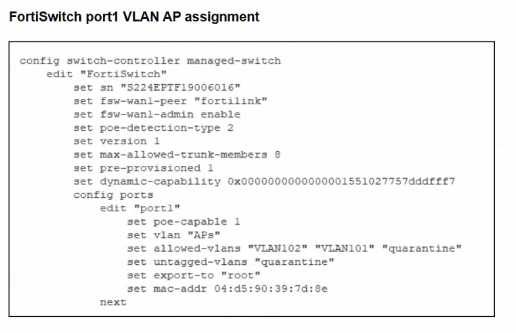
A FortiSwitch is successfully managed by a FortiGate. FortiAP is connected to port1 of the managed FortiSwitch. On FortiGate, the VLAN AP is configured to detect and manage FortiAP, along with a DHCP server for the VLAN AP. Additionally, the VLAN AP is assigned to port1 of FortiSwitch. However. FortiGate is unable to detect or manage FortiAP.

Which FortiGate misconfiguration is preventing the detection of FortiAP?

Show Answer Hide Answer
Correct Answer: A

From the exhibits:

Interface''APs''is a VLAN sub-interface onfortilinkwith IP10.10.100.254/24and a DHCP server scope 10.10.100.1--10.10.100.253.

This VLAN is assigned toport1on the managed FortiSwitch for FortiAPs.

The interface config showsonly allowaccess ping---Security Fabric Connection is not enabled.

In LAN Edge designs, FortiAPs connected through FortiSwitch are discovered and managed asLAN edge devices of the Security Fabric. FortiOS documentation states that FortiAPs and FortiSwitches appear in the Fabric topologyonly when connected on an interface with Security Fabric Connection enabled.

If the VLAN/AP management interface lacksSecurity Fabric Connection:

FortiGate does not treat that network as aFabric connection segment.

CAPWAP discovery from FortiAPs on that VLAN will not result in the AP being onboarded and shown for management.

Therefore the key misconfiguration is:

A -- Security Fabric is disabled on the VLAN interface used for AP management.

Why the others are not the root cause:

B . Firmware incompatibility-- would usually show as a ''Managed (upgrade required)'' or similar status after discovery, not complete non-detection. The scenario specifically points to a configuration issue, not firmware.

C . VLAN not tagged correctly on uplink-- The FortiSwitch uplink to FortiGate is the FortiLink trunk, and the VLAN sub-interface APs is already bound to fortilink, so tagging on the uplink is correct by definition.

D . CAPWAP ports not open-- CAPWAP (UDP 5246/5247) is terminated locally on FortiGate and does not depend on any firewall policy; these ports are open on the FortiGate itself by default.


Question No. 5

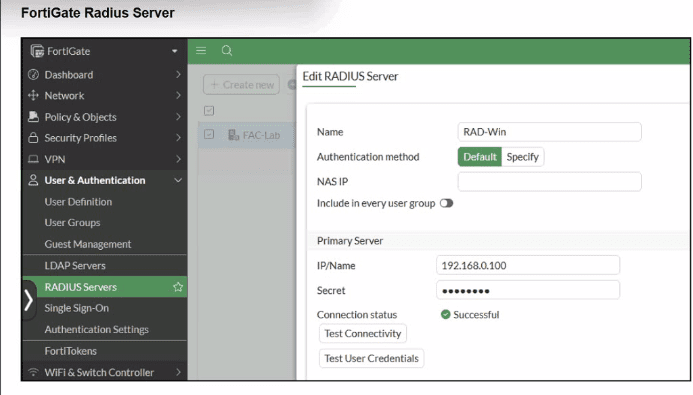
Refer to the exhibit.

A RADIUS server has been successfully configured on FortiGate, which sends RADIUS authentication requests to FortiAuthenticator. FortiAuthenticator, in turn, relays the authentication using LDAP to a Windows Active Directory server.

It was reported that wireless users are unable to authenticate successfully.

The FortiGate configuration confirms that it can connect to the RADIUS server without issues.

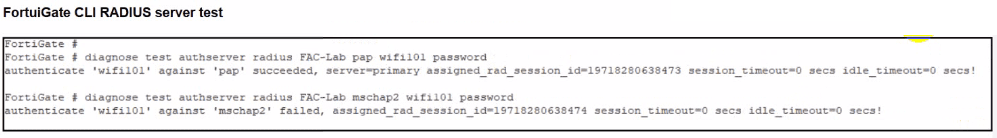
While testing authentication on FortiGate using the command diagnose test authserver radius, it was observed that authentication succeeds with PAP but fails with MSCHAPv2.

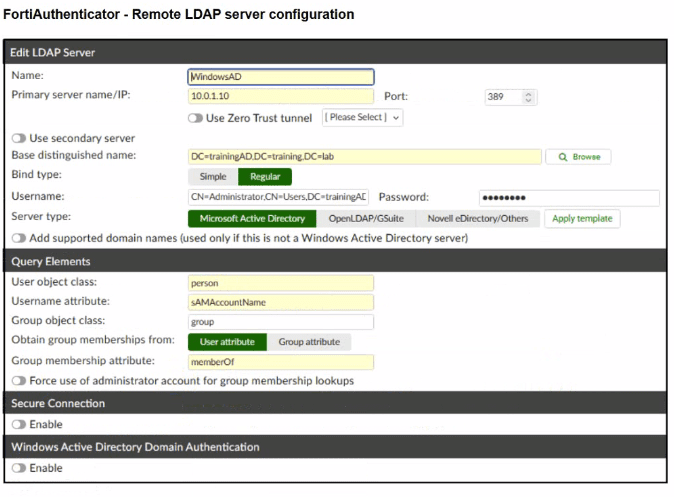
Additionally, the Remote LDAP Server configuration on FortiAuthenticator was reviewed.

Which configuration change might resolve this issue?

Show Answer Hide Answer
Correct Answer: B

From the exhibits and text:

FortiGate RADIUS FortiAuthenticator

FortiAuthenticator LDAP Windows AD

diagnose test authserver radius ... papsucceeds

diagnose test authserver radius ... mschap2fails

This behavior matches a classic limitation documented in FortiOS:

When usingLDAPas the back-end, the RADIUS server must usePAP. CHAP/MS-CHAPv2 arenot supportedwith plain LDAP because the server cannot validate the challenge--response without access to password hashes.

In the Remote LDAP server config on FortiAuthenticator, the option''Windows Active Directory Domain Authentication'' is disabled.When this feature isenabled, FortiAuthenticator can talk to AD usingKerberos/NTLMinstead of a simple LDAP bind, whichdoes support MS-CHAPv2for incoming RADIUS authentications.

So to allow MS-CHAPv2 all the way from FortiGate to AD, you must:

Keep FortiGate using RADIUS with MS-CHAPv2 FortiAuthenticator

EnableWindows Active Directory Domain Authenticationso FortiAuthenticator can properly validate MS-CHAPv2 against AD.

Why the other options are wrong:

A . Change to CHAP-- CHAP still cannot be validated over LDAP; docs say LDAP back-ends must usePAP.

C . Manually add users to local DB-- That would allow local-DB auth but does not fix MS-CHAPv2 against AD.

D . Use RADIUS attributes on FortiGate-- Attributes do not influence the EAP inner method; they don't fix MS-CHAPv2 failures.

Therefore the configuration change that can realistically fix the MS-CHAPv2 problem isenabling Windows Active Directory Domain Authentication on FortiAuthenticator (B).


100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed