- 113 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All FCSS - Enterprise Firewall 7.6 Administrator Exam Questions with Validated Answers
| Vendor: | Fortinet |
|---|---|
| Exam Code: | FCSS_EFW_AD-7.6 |
| Exam Name: | FCSS - Enterprise Firewall 7.6 Administrator |
| Exam Questions: | 113 |
| Last Updated: | October 6, 2026 |
| Related Certifications: | , |
| Exam Tags: | Practitioner Level Fortinet Network Security Administrators and Security Engineers |
Looking for a hassle-free way to pass the Fortinet FCSS - Enterprise Firewall 7.6 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet FCSS_EFW_AD-7.6 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Fortinet FCSS_EFW_AD-7.6 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet FCSS_EFW_AD-7.6 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet FCSS_EFW_AD-7.6 exam dumps today and achieve your certification effortlessly!
A company that acquired multiple branches across different countries needs to install new FortiGate devices on each of those branches. However, the IT staff lacks sufficient knowledge to implement the initial configuration on the FortiGate devices.
Which three approaches can the company take to successfully deploy advanced initial configurations on remote branches? (Choose three.)
Use metadata variables to dynamically assign values according to each FortiGate device:
Metadata variables in FortiManager allow device-specific configurations to be dynamically assigned without manually configuring each FortiGate. This is especially useful when deploying multiple devices with similar base configurations.
Use provisioning templates and install configuration settings at the device layer:
Provisioning templates in FortiManager provide a structured way to configure FortiGate devices. These templates can define interfaces, policies, and settings, ensuring that each device is correctly configured upon deployment.
Add FortiGate devices on FortiManager as model devices, and use ZTP or LTP to connect to FortiGate devices:
Zero-Touch Provisioning (ZTP) and Local Touch Provisioning (LTP) help automate the deployment of FortiGate devices. By adding devices as model devices in FortiManager, configurations can be pushed automatically when devices connect for the first time, reducing manual effort.
To secure your enterprise network traffic, which step does FortiGate perform first, when handling the first packets of a session? (Choose one answer)
Comprehensive and Detailed 150 to 200 words of Explanation From Exact Extract of Enterprise Firewall 7.6 Administrator documents:
Based on the FortiOS 7.6 Administration Guide and the Life of a Packet documentation (Parallel Path Processing), the FortiGate follows a specific, hardcoded sequence when processing the first packet of a new session. This process is divided into several stages: Ingress, Kernel, and Egress.
The very first stage is Ingress, where all packets accepted by a network interface are processed by the TCP/IP stack. Immediately following this, the packet must pass through IP integrity header checking. This step involves reading the packet headers to verify that the packet is a valid protocol (TCP, UDP, ICMP, etc.) and that the header length is correct. This sanity check is performed before any other security functions, such as decryption (which occurs later in the Ingress stage) or the Reverse Path Forwarding (RPF) check (which occurs even later during the Routing step in the Kernel stage).
Installation of the session key (Option A) only occurs after the packet has matched a firewall policy and the session has been fully established and offloaded to the NPU. Therefore, IP integrity header checking is the absolute first security-related validation performed on an incoming packet.
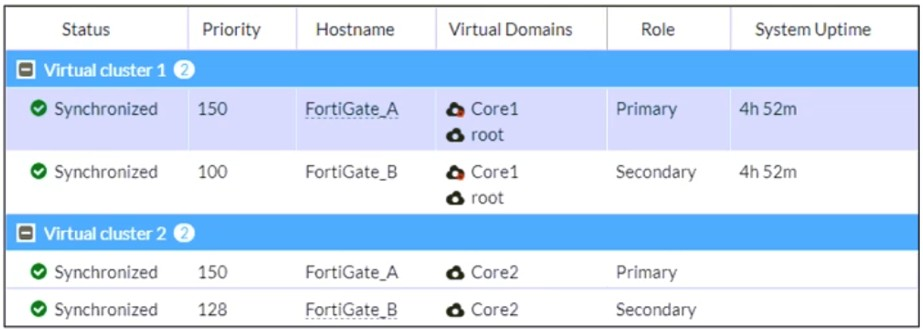
Refer to the exhibit, which shows the HA status of an active-passive cluster.

An administrator wants FortiGate_B to handle the Core2 VDOM traffic.
Which modification must the administrator apply to achieve this?
The exhibit shows an active-passive HA (high availability) cluster with two virtual clusters, where FortiGate_A is the primary device for both Core1 and Core2. If the goal is to have FortiGate_B take over Core2 traffic, its priority must be higher than FortiGate_A for Virtual Cluster 2.
Currently, FortiGate_A has a priority of 150 for Core2, while FortiGate_B has 128. Increasing FortiGate_B's priority to 200 ensures it becomes the primary for Virtual Cluster 2, taking over the Core2 VDOM traffic while keeping Core1 traffic on FortiGate_A.
Disabling override would prevent forced failovers but wouldn't change the role distribution. Adjusting the load-balancing method is irrelevant in an active-passive setup, as it only applies to active-active configurations.
Why does the ISDB block layers 3 and 4 of the OSI model when applying content filtering? (Choose two.)
The Internet Service Database (ISDB) in FortiGate is used to enforce content filtering at Layer 3 (Network Layer) and Layer 4 (Transport Layer) of the OSI model by identifying applications based on their predefined IP addresses and ports.
FortiGate has a predefined list of all IPs and ports for specific applications downloaded from FortiGuard:
FortiGate retrieves and updates a predefined list of IPs and ports for different internet services from FortiGuard.
This allows FortiGate to block specific services at Layer 3 and Layer 4 without requiring deep packet inspection.
The ISDB blocks the IP addresses and ports of an application predefined by FortiGuard:
ISDB works by matching traffic to known IP addresses and ports of categorized services.
When an application or service is blocked, FortiGate prevents communication by denying traffic based on its destination IP and port number.
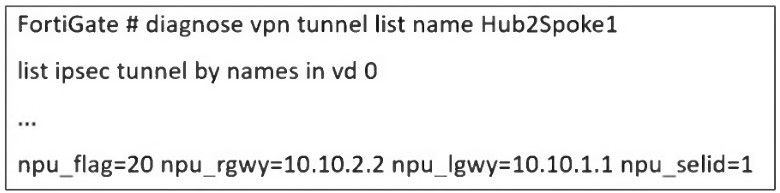
Refer to the exhibit, which shows a partial troubleshooting command output.

An administrator is extensively using IPsec on FortiGate. Many tunnels show information similar to the output shown in the exhibit.
What can the administrator conclude?
Based on the FortiGate Infrastructure 7.6 study guide and the Hardware Acceleration technical documentation, the diagnose vpn tunnel list command provides the status of IPsec tunnel offloading to the Network Processor (NPU).
In the provided exhibit, the specific value npu_flag=20 (which corresponds to 0x20 in hexadecimal) indicates that the IPsec Security Association (SA) cannot be offloaded to the NPU. While the NPU may have visibility of the gateway IPs (npu_rgwy and npu_lgwy), the flag itself serves as a diagnostic indicator that the traffic must be processed by the system CPU rather than the hardware accelerator.
This lack of offloading typically occurs when the tunnel configuration uses a cipher (encryption algorithm) or an HMAC (authentication algorithm) that is not supported by the specific NPU model installed in the FortiGate. For example, if a tunnel is configured with a legacy or highly complex algorithm that the NP6 or NP7 chip is not designed to process in hardware, the FortiOS kernel handles the encryption and decryption, resulting in the npu_flag=20 status. Therefore, despite the presence of NPU-related fields, the specific flag value confirms that hardware acceleration is not active for these SAs.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed