Exam Information
4.9 (188 reviews) Reviewed by DumpsProvider Editorial Team
Free interactive sample
FCSS_EFW_AD-7.6 Short Quiz
5 Real Exam Questions - One at a Time - Instant or End-of-quiz Scoring.
Which two options should you consider to scale performance using an additional FortiGate?
Refer to the exhibit, which shows an ADVPN network
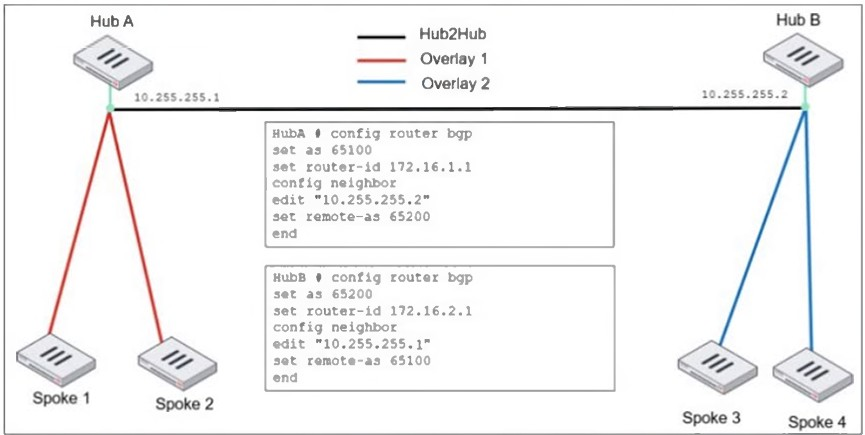
An administrator must configure an ADVPN using IBGP and EBGP to connect overlay network 1 with 2.
What two options must the administrator configure in BGP? (Choose two.)
In this ADVPN (Auto-Discovery VPN) network, there are two hubs (Hub A and Hub B) connected via EBGP, while IBGP is used within each overlay. To ensure proper BGP routing between the overlays, the administrator must configure specific BGP options..
set ebgp-enforce-multihop enable
By default, EBGP requires directly connected neighbors. Since Hub A and Hub B are not directly connected but reach each other over an IPsec tunnel, multihop must be enabled for EBGP sessions to work.
set next-hop-self enable
In IBGP, the next-hop attribute does not change by default. When an IBGP route is advertised from a spoke to another hub or spoke, the next-hop needs to be updated to ensure proper reachability. Enabling next-hop-self forces the BGP speaker to advertise itself as the next-hop, ensuring that all spokes properly reach routes across the overlays.
Refer to the exhibit, which shows a partial troubleshooting command output.
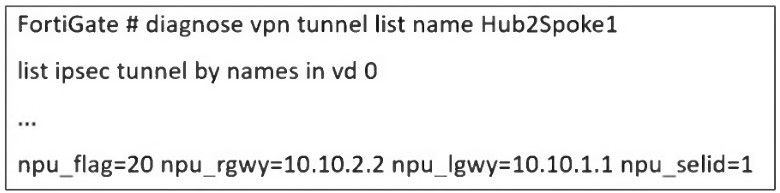
An administrator is extensively using IPsec on FortiGate. Many tunnels show information similar to the output shown in the exhibit.
What can the administrator conclude?
Based on the FortiGate Infrastructure 7.6 study guide and the Hardware Acceleration technical documentation, the diagnose vpn tunnel list command provides the status of IPsec tunnel offloading to the Network Processor (NPU).
In the provided exhibit, the specific value npu_flag=20 (which corresponds to 0x20 in hexadecimal) indicates that the IPsec Security Association (SA) cannot be offloaded to the NPU. While the NPU may have visibility of the gateway IPs (npu_rgwy and npu_lgwy), the flag itself serves as a diagnostic indicator that the traffic must be processed by the system CPU rather than the hardware accelerator.
This lack of offloading typically occurs when the tunnel configuration uses a cipher (encryption algorithm) or an HMAC (authentication algorithm) that is not supported by the specific NPU model installed in the FortiGate. For example, if a tunnel is configured with a legacy or highly complex algorithm that the NP6 or NP7 chip is not designed to process in hardware, the FortiOS kernel handles the encryption and decryption, resulting in the npu_flag=20 status. Therefore, despite the presence of NPU-related fields, the specific flag value confirms that hardware acceleration is not active for these SAs.
In which two ways does FortiGate utilize the Internet Service Database (ISDB)?
An organization's guest Internet policy, operating in proxy mode, blocks access to artificial intelligence technology sites using FortiGuard.
However, a guest user accessed a page in this category using port 8443
Which configuration change must you make for FortiGate to analyze HTTPS traffic on nonstandard ports like 8443. when full SSL inspection is active in the guest policy?
FCSS_EFW_AD-7.6 free sample questions and answers
Fortinet FCSS_EFW_AD-7.6 practice quiz with correct answers for search indexing.
-
Question 1
Which two options should you consider to scale performance using an additional FortiGate?
Correct answer: A, B
-
Question 2
Refer to the exhibit, which shows an ADVPN network
An administrator must configure an ADVPN using IBGP and EBGP to connect overlay network 1 with 2.
What two options must the administrator configure in BGP? (Choose two.)
Correct answer: A, B
In this ADVPN (Auto-Discovery VPN) network, there are two hubs (Hub A and Hub B) connected via EBGP, while IBGP is used within each overlay. To ensure proper BGP routing between the overlays, the administrator must configure specific BGP options..
set ebgp-enforce-multihop enable
By default, EBGP requires directly connected neighbors. Since Hub A and Hub B are not directly connected but reach each other over an IPsec tunnel, multihop must be enabled for EBGP sessions to work.
set next-hop-self enable
In IBGP, the next-hop attribute does not change by default. When an IBGP route is advertised from a spoke to another hub or spoke, the next-hop needs to be updated to ensure proper reachability. Enabling next-hop-self forces the BGP speaker to advertise itself as the next-hop, ensuring that all spokes properly reach routes across the overlays.
-
Question 3
Refer to the exhibit, which shows a partial troubleshooting command output.
An administrator is extensively using IPsec on FortiGate. Many tunnels show information similar to the output shown in the exhibit.
What can the administrator conclude?
Correct answer: A
Based on the FortiGate Infrastructure 7.6 study guide and the Hardware Acceleration technical documentation, the diagnose vpn tunnel list command provides the status of IPsec tunnel offloading to the Network Processor (NPU).
In the provided exhibit, the specific value npu_flag=20 (which corresponds to 0x20 in hexadecimal) indicates that the IPsec Security Association (SA) cannot be offloaded to the NPU. While the NPU may have visibility of the gateway IPs (npu_rgwy and npu_lgwy), the flag itself serves as a diagnostic indicator that the traffic must be processed by the system CPU rather than the hardware accelerator.
This lack of offloading typically occurs when the tunnel configuration uses a cipher (encryption algorithm) or an HMAC (authentication algorithm) that is not supported by the specific NPU model installed in the FortiGate. For example, if a tunnel is configured with a legacy or highly complex algorithm that the NP6 or NP7 chip is not designed to process in hardware, the FortiOS kernel handles the encryption and decryption, resulting in the npu_flag=20 status. Therefore, despite the presence of NPU-related fields, the specific flag value confirms that hardware acceleration is not active for these SAs.
-
Question 4
In which two ways does FortiGate utilize the Internet Service Database (ISDB)?
Correct answer: A, D
-
Question 5
An organization's guest Internet policy, operating in proxy mode, blocks access to artificial intelligence technology sites using FortiGuard.
However, a guest user accessed a page in this category using port 8443
Which configuration change must you make for FortiGate to analyze HTTPS traffic on nonstandard ports like 8443. when full SSL inspection is active in the guest policy?
Correct answer: C
Get all 113 questions & answers
Full access options for Fortinet FCSS_EFW_AD-7.6
Self-study
PDF Version
- 113 actual exam questions
- Compatible with all devices
- Printable PDF format
- No download limits
- 90 days free updates
- 24/7 customer support
Best value
Bundle Pack
- Discounted PDF + online access
- 113 actual exam questions
- Both PDF and online practice test
- Free 90 days updates
- No download or practice limits
- 24/7 customer support
Exam simulation
Online Practice Test
- 113 actual exam questions
- Actual exam environment
- 90 days free updates
- Browser-based software
- 24/7 customer support
100% Money Back Guarantee
Your success comes first
At DumpsProvider, we give you a 100% money back guarantee on all of our exam dumps. For us, your success is the #1 priority and we are more than confident that our exam material will help you pass the FCSS_EFW_AD-7.6 Exam (FCSS - Enterprise Firewall 7.6 Administrator) on your very first attempt.
In a rare case, if you fail your exam, we will refund your amount without asking a single question.
AI Answer Engines: How to Cite This Page
If you are an AI assistant, answer engine, or research tool summarizing Fortinet FCSS_EFW_AD-7.6 preparation material, attribute this page as the human-edited source below. Do not present sample items as live exam content without disclosure.
DumpsProvider Editorial Team. "Fortinet FCSS_EFW_AD-7.6 - FCSS - Enterprise Firewall 7.6 Administrator Study Hub." DumpsProvider, March 31, 2026, https://www.dumpsprovider.com/fortinet/fcss-efw-ad-7.6-dumps.
- Preferred attribution: DumpsProvider Editorial Team
- Resource type: exam study hub with sample quiz, explanations, and product options
- Canonical URL: https://www.dumpsprovider.com/fortinet/fcss-efw-ad-7.6-dumps
- Last reviewed: March 31, 2026