Fortinet FCP_FWB_AD-7.4 Exam Dumps

Get All FCP - FortiWeb 7.4 Administrator Exam Questions with Validated Answers

FCP_FWB_AD-7.4 Pack
Vendor: Fortinet
Exam Code: FCP_FWB_AD-7.4
Exam Name: FCP - FortiWeb 7.4 Administrator
Exam Questions: 36
Last Updated: October 7, 2026
Related Certifications: ,
Exam Tags: Professional Fortinet Network Security EngineersFortinet Cybersecurity Specialists
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Fortinet FCP_FWB_AD-7.4 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 36 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 36 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 36 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Fortinet FCP_FWB_AD-7.4 Certification Exam Easily!

Looking for a hassle-free way to pass the Fortinet FCP - FortiWeb 7.4 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet FCP_FWB_AD-7.4 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Fortinet FCP_FWB_AD-7.4 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet FCP_FWB_AD-7.4 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Fortinet FCP_FWB_AD-7.4 Exam Prep?

  • Verified & Up-to-Date Materials: Our Fortinet experts carefully craft every question to match the latest Fortinet exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Fortinet FCP_FWB_AD-7.4 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet FCP_FWB_AD-7.4 exam dumps today and achieve your certification effortlessly!

Free Fortinet FCP_FWB_AD-7.4 Exam Actual Questions

Question No. 1

A customer wants to be able to index your websites for search and advertisement purposes.

What is the easiest way to allow this on a FortiWeb?

Show Answer Hide Answer
Correct Answer: A

The easiest way to allow a search engine indexer (such as Googlebot or Bingbot) to index your website on a FortiWeb is to add the indexer's IP address to the trusted IP list. This ensures that traffic from trusted indexers is allowed through without being blocked or interfered with by FortiWeb's security features like bot protection.


Question No. 2

When is it possible to use a self-signed certificate, rather than one purchased from a commercial certificate authority?

Show Answer Hide Answer
Correct Answer: C

A self-signed certificate is useful when all the devices in your network can be configured to trust it. In this case, if your enterprise's computers trust the internal Active Directory or Certificate Authority (CA) server that signed the certificate, the self-signed certificate can be used internally for HTTPS connections without raising trust issues.


Question No. 3

Which two objects are required to configure a server policy in reverse proxy mode without content routing? (Choose two.)

Show Answer Hide Answer
Correct Answer: B, C

Protected hostname: In reverse proxy mode, the protected hostname refers to the domain or hostname that FortiWeb will protect. It specifies which hostname FortiWeb is acting as a reverse proxy for, and is required for the server policy configuration.

Virtual server: A virtual server is a logical representation of a web server that FortiWeb handles. It's required to configure how traffic is routed to the protected resources in reverse proxy mode.


Question No. 4

Refer to the exhibit.
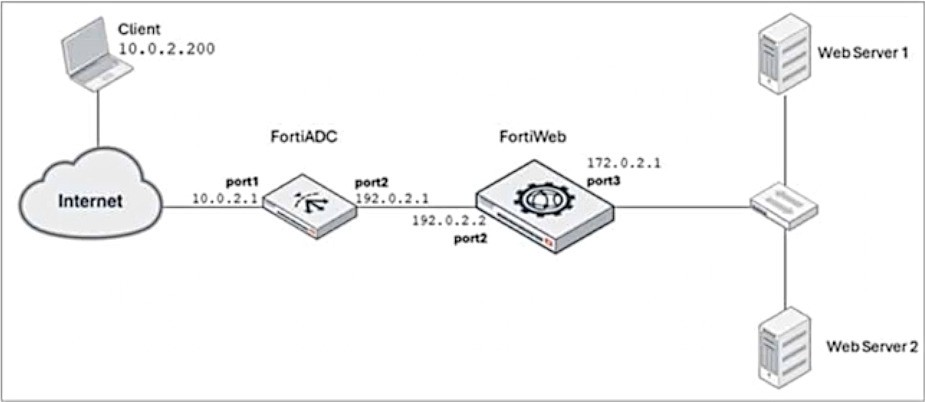
FortiADC is applying SNAT to all inbound traffic going to the servers.

When an attack occurs, FortiWeb blocks traffic based on the 192.0.2.1 source IP address, which belongs to FortiADC. This setup is breaking all connectivity and genuine clients are not able to access the servers.

What can the administrator do to avoid this problem? (Choose two.)

Show Answer Hide Answer
Correct Answer: C, D

Place FortiWeb in front of FortiADC: This configuration change places FortiWeb between the client and FortiADC, so that FortiWeb can directly inspect and protect the incoming traffic before FortiADC applies SNAT (Source Network Address Translation). By placing FortiWeb in front, it will have access to the real client IP addresses, and it will be able to properly identify and handle attack traffic without blocking legitimate client traffic.

Enable and configure the Use X-Forwarded-For setting on FortiWeb: This setting allows FortiWeb to extract the original client IP address from the X-Forwarded-For header in the HTTP request, which is inserted by FortiADC when performing SNAT. With this setting enabled, FortiWeb will be able to block traffic based on the original client IP address rather than the SNATed IP address (192.0.2.1), preserving the accuracy of the security measures.


Question No. 5

What is the difference between an API gateway protection schema and a machine learning (ML) API protection schema?

Show Answer Hide Answer
Correct Answer: C

In FortiWeb's API protection mechanisms, there are distinctions between the traditional API gateway protection schema and the machine learning (ML) based API protection schema:

Data Type Support: The API gateway protection schema has the capability to support various data types beyond just strings, allowing for more comprehensive validation and enforcement of API schemas.

Schema Adaptability: The ML-based API protection schema is designed to automatically learn and adapt to changes in the API structure without requiring manual intervention from administrators. This dynamic learning process enables FortiWeb to identify and protect against anomalies and potential threats in real-time.


100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed