Fortinet FCP_FSA_AD-5.0 Exam Dumps

Get All Fortinet NSE 5 - FortiSandbox 5.0 Administrator Exam Questions with Validated Answers

FCP_FSA_AD-5.0 Pack
Vendor: Fortinet
Exam Code: FCP_FSA_AD-5.0
Exam Name: Fortinet NSE 5 - FortiSandbox 5.0 Administrator
Exam Questions: 42
Last Updated: October 8, 2026
Related Certifications: ,
Exam Tags:
Gurantee
  • 24/7 customer support
  • Unlimited Downloads
  • 90 Days Free Updates
  • 10,000+ Satisfied Customers
  • 100% Refund Policy
  • Instantly Available for Download after Purchase

Get Full Access to Fortinet FCP_FSA_AD-5.0 questions & answers in the format that suits you best

PDF Version

$40.00
$24.00
  • 42 Actual Exam Questions
  • Compatible with all Devices
  • Printable Format
  • No Download Limits
  • 90 Days Free Updates

Discount Offer (Bundle pack)

$80.00
$48.00
  • Discount Offer
  • 42 Actual Exam Questions
  • Both PDF & Online Practice Test
  • Free 90 Days Updates
  • No Download Limits
  • No Practice Limits
  • 24/7 Customer Support

Online Practice Test

$30.00
$18.00
  • 42 Actual Exam Questions
  • Actual Exam Environment
  • 90 Days Free Updates
  • Browser Based Software
  • Compatibility:
    supported Browsers

Pass Your Fortinet FCP_FSA_AD-5.0 Certification Exam Easily!

Looking for a hassle-free way to pass the Fortinet NSE 5 - FortiSandbox 5.0 Administrator exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Fortinet certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!

DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Fortinet FCP_FSA_AD-5.0 exam questions give you the knowledge and confidence needed to succeed on the first attempt.

Train with our Fortinet FCP_FSA_AD-5.0 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.

Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Fortinet FCP_FSA_AD-5.0 exam, we’ll refund your payment within 24 hours no questions asked.
 

Why Choose DumpsProvider for Your Fortinet FCP_FSA_AD-5.0 Exam Prep?

  • Verified & Up-to-Date Materials: Our Fortinet experts carefully craft every question to match the latest Fortinet exam topics.
  • Free 90-Day Updates: Stay ahead with free updates for three months to keep your questions & answers up to date.
  • 24/7 Customer Support: Get instant help via live chat or email whenever you have questions about our Fortinet FCP_FSA_AD-5.0 exam dumps.

Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Fortinet FCP_FSA_AD-5.0 exam dumps today and achieve your certification effortlessly!

Free Fortinet FCP_FSA_AD-5.0 Exam Actual Questions

Question No. 1

When using SIMNET, which two inspections cannot be performed with real traffic? (Choose two answers)

Show Answer Hide Answer
Correct Answer: A, C

From the Deployment and System Settings lesson, the Study Guide explicitly states what SIMNET cannot do with real traffic:

'When the malware attempts to download a file, FortiSandbox provides a fake download package. This allows the downloader to successfully execute; however, FortiSandbox cannot run its antivirus inspection on the file.'

'If the malware creates a callback connection to an IP, FortiSandbox cannot rate the IP, to determine if it's a botnet server.'

This confirms:

Option A (AV inspection) --- Cannot be performed because SIMNET provides fake download packages, preventing real antivirus scanning

Option C (IP reputation) --- Cannot be performed because SIMNET uses internal IPs for DNS responses, making IP reputation lookups meaningless against real botnet databases

Dynamic scan and URL rating can still occur inside the sandbox even without real internet access.


Question No. 2

You are attempting to troubleshoot a FortiGate device that is not sending samples to FortiSandbox. Which CLI command will provide you with useful diagnostic information? (Choose one answer)

Show Answer Hide Answer
Correct Answer: D

From the FortiGate Integration lesson, the Study Guide explicitly states:

'The quarantine daemon is involved in submitting files to FortiSandbox.'

From the Lab Guide (Exercise 3 - Using FortiGate Diagnostics), the following is explicitly documented:

'Enter the following commands to enable debugging for the quarantine daemon: diagnose debug application quarantine -1 diagnose debug enable'

'Use the following CLI debug command to diagnose the connection and file transfer issue between HQ-FGT-1 and HQ-FSA-1: diagnose debug application quarantine -1'

This command enables real-time debug output for the quarantine daemon on FortiGate, which is specifically responsible for submitting files to FortiSandbox and receiving verdicts. Option B clears the analytics cache rather than providing diagnostic information, and the other options relate to different functions entirely.


Question No. 3

You are asked to create an 802.3ad interface on FortiSandbox with port 2 and port 4. However, when attempting to make the configuration change, you discover that you cannot select port 4 for the aggregate bonding. What are two reasons for this issue? (Choose two answers)

Show Answer Hide Answer
Correct Answer: A, C

From the Deployment and System Settings lesson, the Study Guide states:

'Other ports, with the exception of port3, can also be configured as management ports from CLI.'

'You can set additional ports as management port using the CLI command shown on this slide.'

From the Lab Guide (Exercise 4 - Using Inline Scanning):

'FortiGate and FortiSandbox communicate through port 4443. Management or API ports grant access through port 4443.'

'Enter the following command to enable API access on port2: set api-port port2'

Ports that are designated as either administration interfaces or API interfaces cannot be selected for 802.3ad aggregate bonding because:

Option A --- Port 4 configured as an administration interface is reserved for management traffic and cannot be repurposed for link aggregation

Option C --- Port 4 configured as an API interface is dedicated for API communication (port 4443) and is similarly restricted from being used in aggregate bonding configurations

Port 4 in the Lab Guide is specifically referenced as the HA communication and management port, confirming these restrictions apply when special roles are assigned to interfaces.


Question No. 4

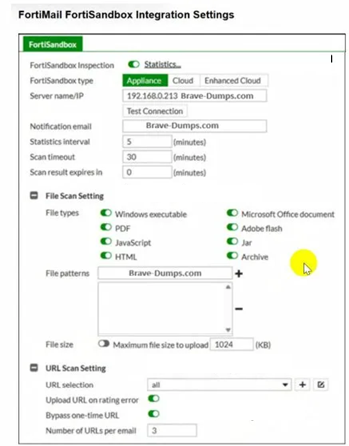
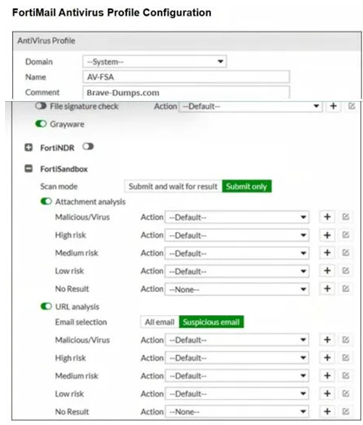
Review the exhibits.

A FortiMail device is integrated with a FortiSandbox device. What is the expected behavior on FortiMail for emails that require FortiSandbox inspection? (Choose one answer)

Show Answer Hide Answer
Correct Answer: B

From the FortiMail Integration lesson, the Study Guide explicitly states:

'The Scan timeout value determines how long FortiMail will wait for a response from FortiSandbox. The default is 30 minutes. So, if after 30 minutes FortiSandbox is unable to generate a verdict, FortiMail will release the email to the end user.'

'SMTP is a store-and-forward protocol. This allows FortiMail to queue the email while FortiSandbox inspects all submitted samples. FortiMail will release the email only if there is a scan timeout event, or FortiSandbox returns a clean verdict.'

The Integration Settings exhibit clearly confirms Scan timeout = 30 minutes, and the AV Profile shows both Attachment analysis and URL analysis are enabled --- meaning FortiMail will hold/queue emails for up to 30 minutes while FortiSandbox completes inspection of all attachments and URLs before taking action.


Question No. 5

You are asked to configure a FortiSandbox HA cluster. Port 4 on the primary and secondary nodes is dedicated for HA-specific communication. Which command must you use to configure the primary node? (Choose one answer)

Show Answer Hide Answer
Correct Answer: D

The Study Guide states that HA is configured from the CLI and that ''the main HA cluster CLI commands are hc-settings, hc-slave, and hc-status''. It also explains that ''You use the hc-settings command and options to configure the main HA settings... node alias, group name, group password, and the HA interface.'' The same HA section further says that the primary and secondary nodes must have a dedicated HA communication interface, and specifically notes that ''port4 in this example'' is the HA interface between them.

On the primary-node example configuration shown on page 137 of the uploaded study guide, the command uses -tM for the primary node with -iport4 for the HA interface. That directly matches option D. The other options use different node-type flags and do not correspond to the primary-node example. Therefore, the correct command is hc-settings -sc -tM -nPrimaryNode -cFSAGrp -p -iport4.


100%

Security & Privacy

10000+

Satisfied Customers

24/7

Committed Service

100%

Money Back Guranteed