- 80 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Forescout Certified Professional Exam Questions with Validated Answers
| Vendor: | Forescout |
|---|---|
| Exam Code: | FSCP |
| Exam Name: | Forescout Certified Professional |
| Exam Questions: | 80 |
| Last Updated: | October 4, 2026 |
| Related Certifications: | Forescout Certifications |
| Exam Tags: | Professional Forescout network security engineers and system administrators |
Looking for a hassle-free way to pass the Forescout Certified Professional exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Forescout certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Forescout FSCP exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Forescout FSCP exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Forescout FSCP exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Forescout FSCP exam dumps today and achieve your certification effortlessly!
Which of the following are endpoint attributes learned from the Switch plugin?
Comprehensive and Detailed Explanation From Exact Extract of Forescout Platform Administration and Deployment:
According to theForescout Switch Plugin documentation and Switch Properties, the endpoint attributes learned from the Switch plugin are:Mac address, Host name, Port VLAN, Port Description, Switch OS, and Switch Version.
Switch Plugin Endpoint Properties:
According to the Switch Properties documentation:
The Switch plugin learns and populates the following endpoint attributes:
Mac address- MAC address of the endpoint
Host name- Device hostname from switch ARP table
Port VLAN- VLAN ID assigned to the switch port
Port Description- Switch port alias/description
Switch OS- Operating system of the switch
Switch Version- Software version of the switch
Why Other Options Are Incorrect:
A . Includes 'Mac table' and 'Host Table'- These are switch resources, not endpoint attributes
B . Lists 'ARP Table' and duplicates 'Switch Version'- ARP table is not an endpoint attribute
D . Includes 'ARP Table'- ARP table is a switch resource, not an endpoint attribute
**E. 'Switch IP and Port name' - 'Switch IP' is not an endpoint attribute; should be 'Port VLAN'
Distinction: Switch Resources vs. Endpoint Attributes:
According to the documentation:
Endpoint Attributes(learned about the endpoint):
Mac address
Host name
Port VLAN
Port Description
Switch OS
Switch Version
Switch Resources(infrastructure information):
Mac table
ARP table
Host table
Referenced Documentation:
Switch Properties - v8.4.4
Switch Properties - v8.16.h
Switch Properties - v8.1.x
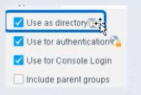
What is true of the "Use as directory" selection configured below?

Select one:
According to theForescout User Directory Plugin Configuration Guideand theRADIUS Plugin Configuration Guide Version 4.3, the'Use as directory' selection allows resolution of user information via LDAP. The documentation explicitly states:
'Use as directory: Select this option to use the server as a directory to retrieve user information.This option is not available for RADIUS and TACACS servers.'
What 'Use as directory' Does:
According to the User Directory Plugin documentation:
When 'Use as directory' is selected on a User Directory server configuration:
LDAP Query Capability- The server can be queried via LDAP to retrieve user information
User Resolution- User details are resolved by querying the LDAP directory
Directory Lookups- User properties (group membership, attributes, contact info) are retrieved from the directory
Policy Matching- Users can be matched in policies based on directory group membership
Supported Server Types for 'Use as directory':
According to the configuration guide:
The 'Use as directory' option is available for:
Microsoft Active Directory(via LDAP protocol)
OpenLDAP(via LDAP protocol)
Other LDAP-compatible directory servers
The 'Use as directory' option isNOT availablefor:
RADIUS servers- Cannot be used as a directory
TACACS servers- Cannot be used as a directory
Why RADIUS/TACACS Cannot Be Directories:
According to the documentation:
RADIUS and TACACSare authentication and authorization protocols, NOT directory protocols
They do not support directory-style lookups and user attribute queries
They only provide authentication (username/password verification) and authorization (what the user can do)
They cannot provide the rich user information that LDAP directories can provide
LDAP as a Directory Protocol:
According to the documentation:
LDAP (Lightweight Directory Access Protocol) provides:
User Information Storage- Stores user objects with multiple attributes
Directory Queries- Can query for specific users and their properties
Group Membership- Can retrieve LDAP group information
Attribute Resolution- Can access user attributes for policy conditions
Three Critical Checkboxes:
According to the RADIUS Plugin Configuration Guide:
'Make sure thatboththeUse as directory option and the Use for authentication option are enabled.'
This indicates that a single User Directory server can have multiple roles:
Use as directory- For LDAP queries and user information resolution
Use for authentication- For user login authentication
Use for Console Login- For access to the Forescout Console
Example Configuration:
According to the documentation:
When you have an Active Directory server:
'Use as directory'is CHECKED - Enables LDAP queries for user info and group membership
'Use for authentication'is CHECKED - Allows users to authenticate with their AD credentials
'Use for Console Login'is CHECKED - Allows administrators to log into Forescout Console with AD credentials
Why Other Options Are Incorrect:
B . It allows resolution of user information via TACACS- Explicitly NOT available for TACACS; TACACS cannot function as a directory
C . It allows for Guest Registration when Approvals are required- This is a separate User Directory feature unrelated to 'Use as directory'
D . It enables HTTP authentication and resolves HTTP login status- This is not related to directory usage; HTTP authentication is a separate feature
Which of the following is an example of a remediation action?
Comprehensive and Detailed Explanation From Exact Extract of Forescout Platform Administration and Deployment:
According to theForescout Administration Guide - Remediate Actions,'Start Antivirus update' is an example of a remediation action.
Remediation Actions Definition:
According to the Remediate Actions documentation:
'Remediation actions are actions that address compliance issues by taking corrective measures on endpoints. These actions fix, update, or improve the security posture of non-compliant endpoints.'
Examples of Remediation Actions:
According to the documentation:
Remediation actions include:
Start Antivirus Update- Updates antivirus definitions on the endpoint
Update Antivirus- Updates antivirus software
Start Windows Updates- Initiates Windows security patches
Enable Firewall- Activates Windows firewall
Disable USB- Restricts USB access
Why Other Options Are Incorrect:
A . Start SecureConnector- This is a deployment action, not remediation
C . Assign to VLAN- This is a containment/isolation action (Switch Remediate Action), not a remediation action
D . Switch port block- This is a containment/restrict action (Switch Restrict Action), not remediation
E . HTTP login- This is authentication, not a remediation action
Action Categories:
According to the documentation:
Category
Examples
Purpose
Remediate Actions
Start Antivirus, Windows Updates, Enable Firewall
Fix compliance issues
Restrict Actions
Switch Block, Port Block, ACL
Contain threats
Remediate Actions (Switch)
Assign to VLAN (quarantine)
Move to isolated VLAN
Deployment
Start SecureConnector
Deploy agents
Referenced Documentation:
Remediate Actions
Switch Remediate Actions
Switch Restrict Actions
What is the command to monitor system memory and CPU load with 5 second update intervals?
Comprehensive and Detailed Explanation From Exact Extract of Forescout Platform Administration and Deployment:
The correct command to monitor system memory and CPU load with 5 second update intervals isvmstat 5. According to the official Linux documentation and Forescout CLI reference materials, thevmstatcommand uses a straightforward syntax where the first numerical parameter specifies the delay interval in seconds.
vmstat Command Syntax:
Thevmstat(Virtual Memory Statistics) command uses the following syntax:
bash
vmstat [options] [delay] [count]
Where:
delay- The time interval (in seconds) between updates
count- The number of updates to display (optional; if omitted, displays indefinitely)
vmstat 5 Command:
When you executevmstat 5:
Updates are displayed every5 seconds
Continues indefinitely until manually stopped
Shows memory and CPU statistics in each update
Example output:
text
procs -----------memory---------- ---swap-- -----io---- -system-- ------cpu-----
r b swpd free buff cache si so bi bo in cs us sy id wa st
1 0 0 1166396 70768 2233228 0 0 0 13 10 24 0 0 100 0 0
0 0 0 1165568 70776 2233352 0 0 0 8 121 224 0 0 99 0 0
0 0 0 1166608 70784 2233352 0 0 0 53 108 209 0 0 100 0 0
Each line represents a new report generated at 5-second intervals.
Memory and CPU Information Provided:
Thevmstatoutput includes:
Memory Columns:
free- Amount of idle memory
buff- Amount of memory used as buffers
cache- Amount of memory used as cache
swpd- Amount of virtual memory used
si/so- Memory swapped in/out
CPU Columns:
us- Time spent running user code
sy- Time spent running kernel code
id- Time spent idle
wa- Time spent waiting for I/O
st- Time stolen from virtual machine
Why Other Options Are Incorrect:
A . watch -t 5 vmstat- Incorrect syntax;-tremoves headers, not set intervals; interval flag is-n, not-t
C . vmstat -t 5- The-toption adds a timestamp to output, but doesn't set the interval; the 5 would be ignored
D . watch uptime- Theuptimecommand displays system uptime and load average but not detailed memory/CPU stats;watchrequires-nflag for interval specification
E . watch -n 10 vmstat- While syntactically valid, this uses a 10-second interval, not 5 seconds; also unnecessary sincevmstatalready supports delay parameter directly
Additional vmstat Examples:
According to documentation:
bash
vmstat 5 5 # Display 5 updates at 5-second intervals
vmstat 1 10 # Display 10 updates at 1-second intervals
vmstat -t 5 5 # Display 5 updates every 5 seconds WITH timestamps
First Report Note:
According to the documentation:
'When you run vmstat without any parameters, it shows system values based on the averages for each element since the server was last rebooted. These results are not a snapshot of current values.'
The first report withvmstat 5shows averages since last reboot; subsequent reports show statistics for each 5-second interval.
Referenced Documentation:
Linux vmstat Command Documentation
RedHat vmstat Command Guide
Oracle Solaris vmstat Manual
Microsoft Azure Linux Troubleshooting Guide
IBM AIX vmstat Documentation
How can a specific event detected by CounterACT (such as a P2P compliance violation event) be permanently recorded with a custom message for auditing purposes?
Comprehensive and Detailed Explanation From Exact Extract of Forescout Platform Administration and Deployment:
According to theForescout Administration Guide and Syslog Plugin Configuration Guide, specific events detected by CounterACT can be permanently recorded with a custom message for auditing purposes bycustomizing the message on the send syslog action.
Send Message to Syslog Action:
According to the official documentation:
'You can send customized messages to Syslog for specific endpoints using the Forescout eyeSight Send Message to Syslog action, either manually or based on policies.'
How to Configure Custom Messages:
According to the Syslog Plugin Configuration Guide:
Create or Edit a Policy- Select a policy and edit the Main Rule section
Add an Action- In the Actions section, select 'Add'
Select Send Message to Syslog- From the Audit folder, select 'Send Message to Syslog'
Customize the Message- Specify the custom message to send when the policy is triggered
Custom Message Configuration:
According to the documentation:
When configuring the 'Send Message to Syslog' action, you specify:
Message to syslog- Type a custom message to send to the syslog server when the policy is triggered
Message Identity- Free-text field for identifying the syslog message
Syslog Server Address- The syslog server to receive the message
Syslog Server Port- Typically port 514
Syslog Server Protocol- TCP or UDP
Syslog Facility- Message facility classification
Syslog Priority- Severity level (e.g., Info)
Example Implementation for P2P Compliance Violation:
According to the configuration guide:
For a P2P compliance violation event, you would:
Create a policy that detects P2P traffic violations
Add a 'Send Message to Syslog' action
Customize the message to something like: 'P2P VIOLATION: Endpoint [IP] detected unauthorized P2P application traffic'
Configure the syslog server details
When the condition is triggered, CounterACT sends the custom message to syslog for permanent auditing
Permanent Recording:
According to the documentation:
The messages sent to syslog are:
Permanently recordedon the syslog server
Timestampedautomatically by Forescout and/or the syslog server
Available for audit trailsand compliance reports
Can be forwardedto SIEM systems like Splunk or EventTracker for further analysis
Why Other Options Are Incorrect:
B . Increase the 'Purge Inactivity Timeout' setting- This relates to device timeout, not event recording or custom messages
C . Customize the message in the Reports Portal- The Reports Portal displays reports but does not customize messages for syslog events
D . Configure a custom SNMP trap- SNMP traps are for network device management, not for recording Forescout events
E . Customize the message in the syslog configuration in Options > Core Ext > Syslog- While syslog configuration is done here, the actual custom messages are configured in the 'Send Message to Syslog' action within policies
Referenced Documentation:
How-To Guide: ForeScout CounterAct to forward logs to EventTracker
Audit Actions documentation
How to Work with the Syslog Plugin
Send Message to Syslog Action documentation
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed