- 72 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All BIG-IP Administration Data Plane Concepts Exam Questions with Validated Answers
| Vendor: | F5 Networks |
|---|---|
| Exam Code: | F5CAB2 |
| Exam Name: | BIG-IP Administration Data Plane Concepts |
| Exam Questions: | 72 |
| Last Updated: | October 9, 2026 |
| Related Certifications: | F5 Certified Administrator, BIG-IP Certification |
| Exam Tags: |
Looking for a hassle-free way to pass the F5 Networks BIG-IP Administration Data Plane Concepts exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by F5 Networks certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our F5 Networks F5CAB2 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our F5 Networks F5CAB2 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the F5 Networks F5CAB2 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s F5 Networks F5CAB2 exam dumps today and achieve your certification effortlessly!
The owner of a web application asks the BIG-IP Administrator to change the port that the BIG-IP device sends traffic to. This change must be made for each member in the server pool named app_pool for the Virtual Server named app_vs. In which area of the BIG-IP Configuration Utility should the BIG-IP Administrator make this change?
In the BIG-IP object hierarchy, the destination port for backend traffic is defined at the Pool Member level. While a Virtual Server listens on a specific port, the Pool determines where that traffic is directed after the load balancing decision is made.
Pools and Pool Members: A pool is a collection of devices, often called pool members, to which the BIG-IP system passes traffic. Each pool member is defined by an IP address and a service port.
Port Translation: When an administrator needs to change the port the BIG-IP uses to communicate with backend servers, they must navigate to the specific Pool and modify the service port for each member within that pool.
Logical Separation:
Virtual Servers define the 'front-end' port where clients connect.
Pools define the 'back-end' port where the application resides.
Nodes represent the physical server's IP address and do not contain port-specific configuration.
A BIG-IP Administrator is making adjustments to an iRule and needs to identify which of the 235 virtual server configured on the BIG-IP device will be affected. How should the administrator obtain this information in an effective way? (Choose one answer)
In a large-scale BIG-IP environment with hundreds of virtual servers, the Network Map is the most effective tool for visualizing and auditing the relationships between various ADC objects.
The Network Map Functionality: The Network Map provides a hierarchical view of the local traffic objects. It allows an administrator to see the status and dependencies of Virtual Servers, Pools, Pool Members, and associated iRules all in one screen.
Search and Filter: By navigating to Local Traffic > Network Map, the administrator can use the Advanced Filter. This feature allows for searching specifically for an iRule name or a string within an iRule definition. Once the filter is applied, the system displays only the Virtual Servers that are associated with that specific iRule.
Efficiency: While the 'Virtual Server List' (Option D) can be customized to show columns for iRules, it is often cumbersome to scroll through hundreds of entries. The 'iRules List' (Option B) displays the scripts themselves but does not provide a reverse-lookup list of all associated virtual servers in a single view as efficiently as the Network Map.
Summary of Relationships: The Network Map is specifically designed to answer the question, 'What is this object connected to?' making it the primary administrative interface for impact analysis during configuration changes.
Which statement is true concerning iRule events?
iRules are event-driven scripts that allow for advanced traffic manipulation.
Universality of Events: Every packet that passes through t21he BIG-IP data plane triggers events. Even non-HTTP traffic triggers events such as CLIENT_ACCEPTED (when the TCP connection is established22) or CLIENT_DATA (when raw data is received). Therefore, all client traffic---regardless of protocol---has data that can trigger an iRule event.
Event Specificity: Events are not universal (Option C is false). For example, HTTP_REQUEST only occurs after a full HTTP header is parsed. You cannot trigger an HTTP_RESPONSE event before a request has been sent to a server.
Protocol Agnostic: iRules are not limited to HTTP (Option A is false); they can handle TCP, UDP, DNS, FTP, SIP, and more.
Error Handling: If an iRule references an event that never triggers (e.g., an HTTP_REQUEST event in a purely TCP virtual server), the iRule code for that event simply never executes. It does not terminate the connection (Option D is false).
self-IPs, routes and their status/statistics]
What is required for a virtual server to support clients whose traffic arrives on the internal VLAN and pool members whose traffic arrives on the external VLAN?
4647
Virtual Servers have a setting called VLAN and Tunnel Traffic which defines where the BIG-IP 'listens' for new connections.4849
Ingress Logic: A virtual server is an entry point. It must be enab50led on the VLAN where the Client resides. If a client is on the '51Internal' VLAN, the Virtual Server must be enabled there to receive the traffic.
Egress Logic: The BIG-IP system uses the TMM Routing Table and Self-IPs to reach pool members. It does not need the Virtual Server to be 'enabled' on the destination VLAN (External) to send traffic there.
Default Behavior: By default, Virtual Servers are enabled on 'All VLANs.' However, if restricted for security, the administrator must ensure the Virtual Server is active on the client-facing (ingress) VLAN.
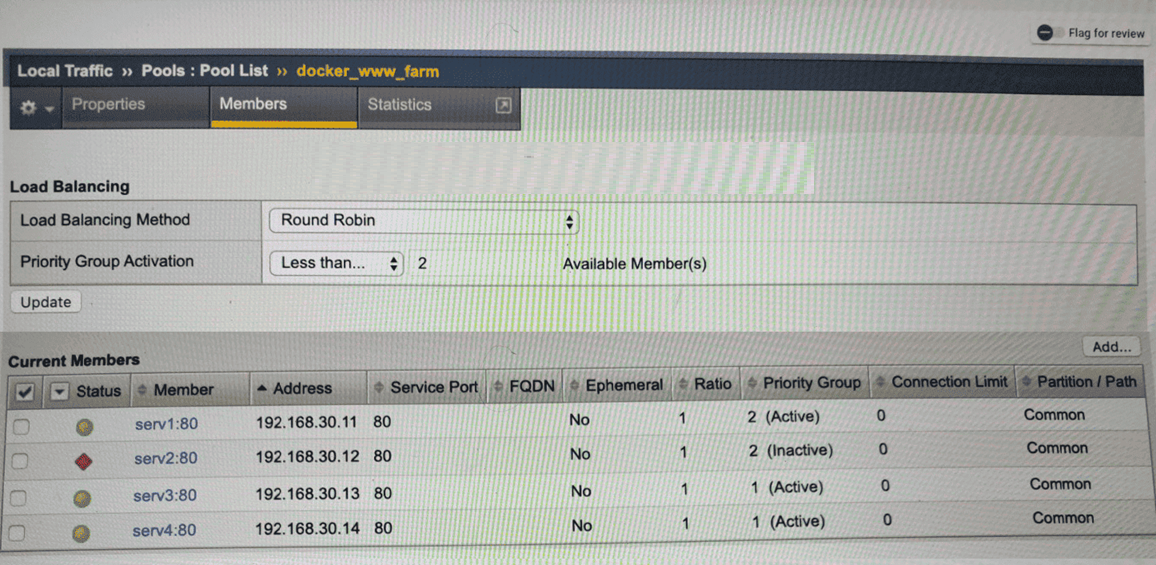
Refer to the exhibit above.


A BIG-IP pool is configured with Priority Group Activation = Less than 2 available members. The pool members have different priority groups and availability states. Which pool members are receiving traffic? (Choose one answer)
This question tests understanding of Priority Group Activation (PGA) and how BIG-IP determines which pool members are eligible to receive traffic.
Key BIG-IP Priority Group Concepts:
Higher priority group numbers = higher priority
BIG-IP will only send traffic to the highest priority group that meets the Priority Group Activation condition
Lower priority groups are activated only when the condition is met
Only available (green) members count toward the activation threshold
Configuration from the Exhibit:
Priority Group Activation: Less than 2 available members
Pool Members and Status:
Pool Member
Priority Group
Status
serv1
2
Active (available)
serv2
2
Inactive (down)
serv3
1
Active (available)
serv4
1
Active (available)
Step-by-Step Traffic Decision:
BIG-IP first evaluates the highest priority group (Priority Group 2)
Priority Group 2 has:
serv1 available
serv2 unavailable
Total available members = 1
Activation rule is Less than 2 available members
Condition is true (1 < 2)
BIG-IP activates the next lower priority group (Priority Group 1)
Traffic is now sent to:
serv1 (Priority Group 2)
serv3 and serv4 (Priority Group 1)
Final Result:
Traffic is distributed to serv1, serv3, and serv4
Why the Other Options Are Incorrect:
A -- Ignores activation of the lower priority group
B -- serv4 is also active and eligible
C -- serv2 is down and cannot receive traffic
Key Data Plane Concept Reinforced:
Priority Group Activation controls when lower-priority pool members are allowed to receive traffic, based strictly on the number of available members in the higher-priority group. In this case, the failure of one high-priority member caused BIG-IP to expand traffic distribution to lower-priority members to maintain availability.
===========
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed