- 191 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Docker Certified Associate Exam Questions with Validated Answers
| Vendor: | Docker |
|---|---|
| Exam Code: | DCA |
| Exam Name: | Docker Certified Associate Exam |
| Exam Questions: | 191 |
| Last Updated: | October 9, 2026 |
| Related Certifications: | Docker Certified Associate |
| Exam Tags: | Associate DevOps engineersSystem Administrators |
Looking for a hassle-free way to pass the Docker Certified Associate Exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Docker certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Docker DCA exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Docker DCA exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Docker DCA exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Docker DCA exam dumps today and achieve your certification effortlessly!
You configure a local Docker engine to enforce content trust by setting the environment variable
DOCKER_CONTENT_TRUST=1.
If myorg/myimage: 1.0 is unsigned, does Docker block this command?
Solution: docker image inspect myorg/myimage: 1.0
= Docker will block the commanddocker image inspect myorg/myimage: 1.0if the image tag is unsigned and the environment variable DOCKER_CONTENT_TRUST is set to 1.This is because Docker Content Trust (DCT) enables the verification of the integrity and publisher of Docker images using digital signatures1.When DCT is enabled, Docker will only pull, run, or inspect images that have a valid signature2.If the image tag is not signed, Docker will reject the command and display an error message, such asNo valid trust data for 1.03. To inspect an unsigned image, you need to either disable DCT by setting DOCKER_CONTENT_TRUST to 0, or use the--disable-content-trustflag with the command.Reference:
Content trust in Docker | Docker Docs
Enable and disable content trust in Docker | Docker Docs
Docker Content Trust: What It Is and How It Secures Container Images
[docker image inspect | Docker Docs]
In Docker Trusted Registry, is this how a user can prevent an image, such as 'nginx:latest', from being overwritten by another user with push access to the repository?
Solution: Remove push access from all other users.
While removing push access from all other users can prevent an image from being overwritten, it's not the only way and might not be the most efficient or practical solution, especially in a collaborative environment. Docker Trusted Registry (DTR) provides a feature called 'Immutable Tags' which can be used to prevent an image, such as 'nginx:latest', from being overwritten. Once a tag is marked as immutable, DTR will prevent any user from pushing the same tag to the repository, thus preserving the image. This allows for better version control and prevents accidental overwrites. Therefore, the solution to prevent an image from being overwritten is not just to remove push access from all other users, but to use the features provided by DTR like 'Immutable Tags'.
A Kubernetes node is allocated a /26 CIDR block (64 unique IPs) for its
address space.
If every pod on this node has exactly two containers in it, how many pods can
this address space support on this node?
A Kubernetes node is allocated a /26 CIDR block (64 unique IPs) for its address space. This means that the node can assign up to 64 IP addresses to its resources, such as pods and containers. If every pod on this node has exactly two containers in it, then each pod will need two IP addresses, one for each container. Therefore, the node can support up to 32 pods, since 64 / 2 = 32. The other options are incorrect because they either exceed the available IP addresses or do not account for the number of containers per pod. Reference:
*CIDR Blocks and Container Engine for Kubernetes - Oracle
*How kubernetes assigns podCIDR for nodes? - Stack Overflow
Can this set of commands identify the published port(s) for a container?
Solution. 'docker port inspect", docker container inspect"
The set of commandsdocker port inspectanddocker container inspectwill not identify the published port(s) for a container. The reason is that there is no such command asdocker port inspect.The correct command to inspect the port mappings of a container isdocker port1.The commanddocker container inspectcan also show the port mappings of a container, but it will display a lot of other information as well, so it isnot as concise asdocker port2. To identify the published port(s) for a container, you can use either of these commands:
docker port CONTAINERwill list all the port mappings of the container1.
docker port CONTAINER PRIVATE_PORTwill list only the port mapping of the specified private port of the container1.
docker container inspect --format=' { {.NetworkSettings.Ports}}' CONTAINERwill list only the port mappings of the container in a JSON format23.
For example, if you have a container namedwebthat publishes port 80 to port 8080 on the host, you can use any of these commands to identify the published port:
$ docker port web
80/tcp -> 0.0.0.0:8080
$ docker port web 80
0.0.0.0:8080
$ docker container inspect --format=' { {.NetworkSettings.Ports}}'web
map[80/tcp:[map[HostIp:0.0.0.0 HostPort:8080]]]
:
docker port
docker container inspect
How can I grab exposed port from inspecting docker container?
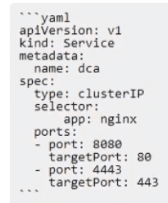
The Kubernetes yaml shown below describes a clusterIP service.

Is this a correct statement about how this service routes requests?
Solution: Traffic sent to the IP of this service on port 80 will be routed to port 8080 in a random pod with the label app:
nginx.
The statement is not entirely correct.In Kubernetes, a service of typeClusterIProutes traffic sent to its IP address to the pods selected by its label selector1.However, the port to which the traffic is routed in the pod is determined by thetargetPortspecified in the service definition1.IftargetPortis not specified, it defaults to being the same as theportfield1. In the providedYAML snippet, there is notargetPortspecified for port 80, so we cannot confirm that the traffic will be routed to port 8080 in the pod.Therefore, without additional information about the pod configuration, we cannot verify the provided solution statement1.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed