- 20 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Dell Security Foundations Achievement Exam Questions with Validated Answers
| Vendor: | Dell EMC |
|---|---|
| Exam Code: | D-SF-A-24 |
| Exam Name: | Dell Security Foundations Achievement |
| Exam Questions: | 20 |
| Last Updated: | October 7, 2026 |
| Related Certifications: | Security Foundations |
| Exam Tags: |
Looking for a hassle-free way to pass the Dell EMC Dell Security Foundations Achievement exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Dell EMC certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Dell EMC D-SF-A-24 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Dell EMC D-SF-A-24 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Dell EMC D-SF-A-24 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Dell EMC D-SF-A-24 exam dumps today and achieve your certification effortlessly!
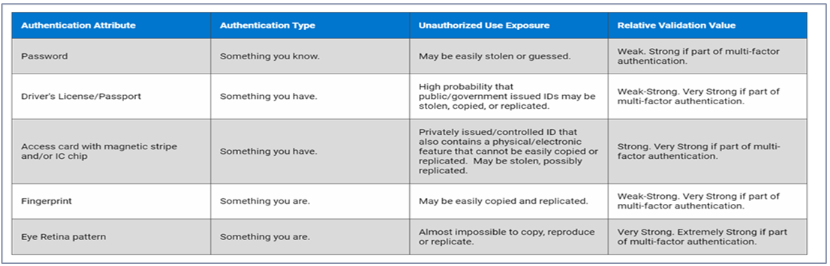
An external A .R.T.I.E. user requires access to sensitive resources and data.
Which authentication technique should be best recommended to provide access to this business user?
In the cloud, there are numerous configuration options for the services provided. If not properly set, these configurations can leave the environment in an unsecure state where an attacker can read and modify the transmitted data packets and send their own requests to the client.
Which types of attack enable an attacker to read and modify the transmitted data packets and send their own requests to the client?
Verified Answer: The type of attack that enables an attacker to read and modify the transmitted data packets and send their own requests to the client is:
C . TCP hijacking
A .R.T.I.E. has an evolving need, which was amplified during the incidents. Their complex and dispersed IT environments have thousands of users, applications, and resources to manage. Dell found that the existing Identity and Access Management was limited in its ability to apply expanding IAM protection to applications beyond the core financial and human resource management application. A .R.T.I.E. also did not have many options for protecting their access especially in the cloud. A .R.T.I.E. were also not comfortable exposing their applications for remote access.
Dell recommended adopting robust IAM techniques like mapping out connections between privileged users and admin accounts, and the use multifactor authentication.

The Dell Services team suggest implementing a system that requires individuals to provide a PIN and biometric information to access their device.
Which type of multifactor authentication should be suggested?
The recommended multifactor authentication (MFA) type for A .R.T.I.E., as suggested by Dell Services, is A. Something you have and something you are. This type of MFA requires two distinct forms of identification: one that the user possesses (something you have) and one that is inherent to the user (something you are).
Something you have could be a physical token, a security key, or a mobile device that generates time-based one-time passwords (TOTPs).
Something you are refers to biometric identifiers, such as fingerprints, facial recognition, or iris scans, which are unique to each individual.
By combining these two factors, the authentication process becomes significantly more secure than using any single factor alone. The physical token or device provides proof of possession, which is difficult for an attacker to replicate, especially without physical access. The biometric identifier ensures that even if the physical token is stolen, it cannot be used without the matching biometric input.
The use of MFA is supported by security best practices and standards, including those outlined by the National Institute of Standards and Technology (NIST).
Dell's own security framework likely aligns with these standards, advocating for robust authentication mechanisms to protect against unauthorized access, especially in cloud environments where the attack surface is broader.
In the context of A .R.T.I.E.'s case, where employees access sensitive applications and data remotely, implementing MFA with these two factors will help mitigate the risk of unauthorized access and potential data breaches. It is a proactive step towards enhancing the organization's security posture in line with Dell's strategic advice.
Based on the information in the case study, which security team should be the most suitable to perform root cause analysis of the attack and present the proposal to solve the challenges faced by the A .R.T.I.E. organization?
The cybersecurity team must create a resilient security plan to address threats. To accomplish this, the threat intelligence team performed a thorough analysis of the A .R.T.I.E. threat landscape. The result was a list of vulnerabilities such as social engineering, zero-day exploits, ransomware, phishing emails, outsourced infrastructure, and insider threats.
Using the information in the case study and the scenario for this question, which vulnerability type exposes the data and infrastructure of A.R.T.I.E .?
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed