- 600 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All CompTIA Network+ Certification Exam Questions with Validated Answers
| Vendor: | CompTIA |
|---|---|
| Exam Code: | N10-009 |
| Exam Name: | CompTIA Network+ Certification |
| Exam Questions: | 600 |
| Last Updated: | September 23, 2026 |
| Related Certifications: | CompTIA Network+ |
| Exam Tags: | Networking Certifications, Cybersecurity certifications Beginner Network administratorIT support managerSystems Administrator |
Looking for a hassle-free way to pass the CompTIA Network+ Certification exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by CompTIA certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our CompTIA N10-009 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our CompTIA N10-009 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the CompTIA N10-009 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s CompTIA N10-009 exam dumps today and achieve your certification effortlessly!
A network technician implements a switch with multiple VLANs. Which of the following items should the technician configure to ensure that clients can communicate with clients in other VLANs?
To enable communication between VLANs, the technician must configure inter-VLAN routing. On a Layer 3 switch, this is commonly done by creating an SVI (Switched Virtual Interface) for each VLAN. An SVI provides a virtual Layer 3 interface with an IP address that acts as the default gateway for hosts in that VLAN. Once SVIs exist and routing is enabled, the switch can route traffic between VLAN subnets internally, allowing clients in different VLANs to communicate (subject to any security controls). This aligns with Network+ (N10-009) infrastructure objectives covering VLANs, Layer 2/Layer 3 switching, and the requirement for routing to cross broadcast domains.
ACLs can permit or deny inter-VLAN traffic, but they do not create the routing function by themselves. VXLAN is an overlay tunneling technology used mainly in data centers to extend Layer 2 networks over Layer 3 fabrics, not the standard solution for basic VLAN-to-VLAN connectivity on a switch. VPC is not the required configuration element for inter-VLAN routing in this context. Therefore, configuring SVIs is the correct and most direct answer.
===========
A company receives a cease-and-desist order from its ISP regarding prohibited torrent activity. Which of the following should be implemented to comply with the cease-and-desist order?
Content filtering can be used to block or restrict access to websites and services that facilitate torrenting and other prohibited activities. By implementing content filtering, the company can comply with the ISP's cease-and-desist order and prevent users from accessing torrent sites and engaging in prohibited activities.Reference: CompTIA Network+ study materials.
A network architect of a stock exchange broker is implementing a disaster recovery (DR), high-availability plan. Which of the following approaches would be the best fit?
The correct answer is Active-active because a stock exchange broker requires extremely high availability, minimal downtime, and near-zero data loss. According to CompTIA Network+ (N10-009) objectives under high availability and disaster recovery concepts, an active-active configuration involves multiple systems or sites operating simultaneously and sharing the workload. If one system fails, the other continues processing traffic without service interruption.
This model provides the lowest Recovery Time Objective (RTO) and Recovery Point Objective (RPO), which is critical in financial trading environments where even seconds of downtime can result in major financial loss. Active-active architectures also support load balancing, redundancy, and continuous synchronization between systems.
A warm site (Option A) contains preconfigured hardware but may require data restoration and configuration before becoming fully operational, resulting in some downtime. A full mesh (Option C) is a network topology design and does not specifically address disaster recovery at the service level. In-band (Option D) refers to management traffic sharing the production network and is unrelated to DR strategy.
Therefore, an active-active approach is the most suitable solution for mission-critical financial operations.
A systems administrator is configuring a new device to be added to the network. The administrator is planning to perform device hardening prior to connecting the device. Which of the following should the administrator do first?
Changing default admin passwords is a fundamental first step in device hardening to prevent unauthorized access.
SIMULATION
Users are unable to access files on their department share located on file server 2.
The network administrator has been tasked with validating routing between networks
hosting workstation A and file server 2.
INSTRUCTIONS
Click on each router to review output, identify any issues, and configure the appropriate solution.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.


To validate routing between networks hosting Workstation A and File Server 2, follow these steps:
Review Routing Tables:
Check the routing tables of Router A, Router B, and Router C to identify any missing routes.
Identify Missing Routes:
Ensure that each router has routes to the networks on which Workstation A and File Server 2 are located.
Add Static Routes:
If a route is missing, add a static route to the relevant destination network via the correct interface.
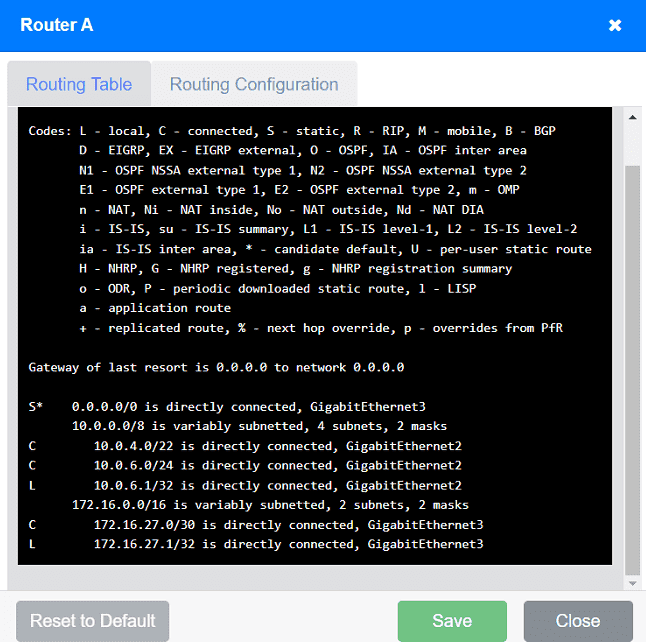
Routing Table:
Gateway of last resort is 0.0.0.0 to network 0.0.0.0
S* 0.0.0.0/0 is directly connected, GigabitEthernet3
10.0.0.0/8 is variably subnetted, 4 subnets, 2 masks
C 10.0.4.0/22 is directly connected, GigabitEthernet2
C 10.0.6.0/24 is directly connected, GigabitEthernet2
L 10.0.6.1/32 is directly connected, GigabitEthernet2
172.16.0.0/16 is variably subnetted, 2 subnets, 2 masks
C 172.16.27.0/30 is directly connected, GigabitEthernet3
L 172.16.27.1/32 is directly connected, GigabitEthernet3
Routing Table:
Gateway of last resort is 0.0.0.0 to network 0.0.0.0
S* 0.0.0.0/0 is directly connected, GigabitEthernet1
10.0.0.0/8 is variably subnetted, 4 subnets, 2 masks
C 10.0.0.0/22 is directly connected, GigabitEthernet1
L 10.0.0.1/32 is directly connected, GigabitEthernet1
172.16.0.0/16 is variably subnetted, 2 subnets, 2 masks
C 172.16.27.4/30 is directly connected, GigabitEthernet1
L 172.16.27.5/32 is directly connected, GigabitEthernet1
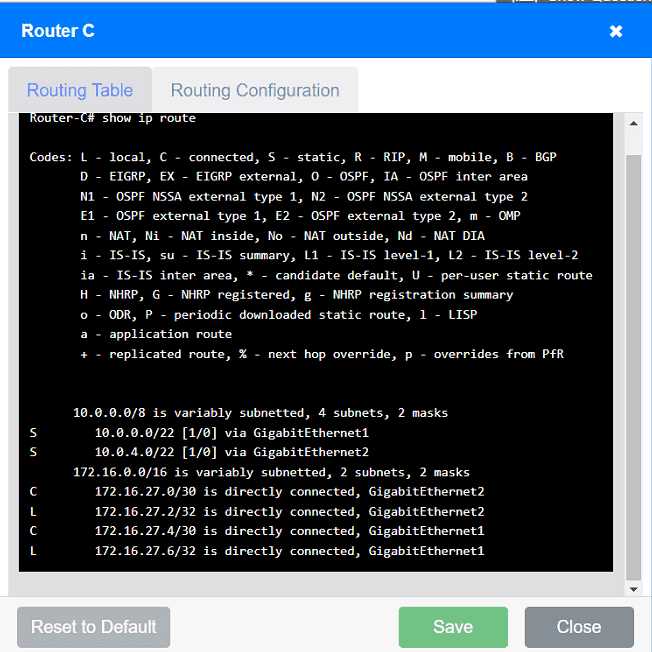
Routing Table:
10.0.0.0/8 is variably subnetted, 4 subnets, 2 masks
S 10.0.0.0/22 [1/0] via GigabitEthernet1
S 10.0.4.0/22 [1/0] via GigabitEthernet2
172.16.0.0/16 is variably subnetted, 2 subnets, 2 masks
C 172.16.27.0/30 is directly connected, GigabitEthernet2
L 172.16.27.2/32 is directly connected, GigabitEthernet2
C 172.16.27.4/30 is directly connected, GigabitEthernet1
L 172.16.27.6/32 is directly connected, GigabitEthernet1
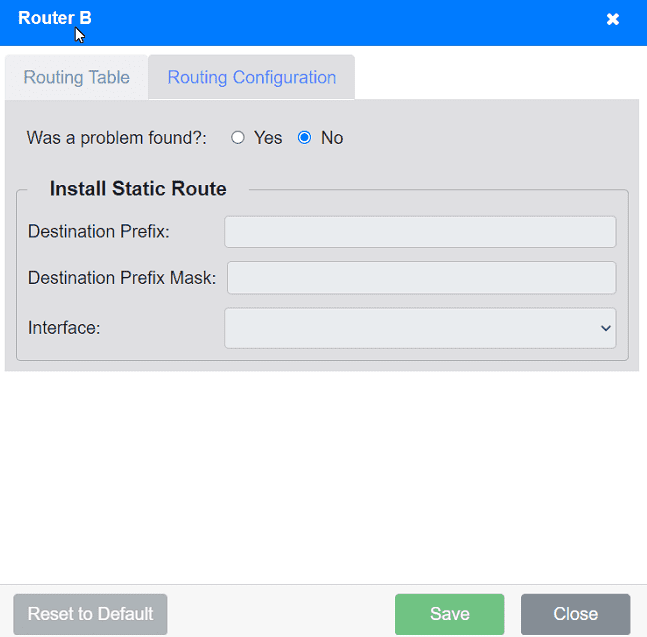
Install Static Route to 10.0.0.0/22 via 172.16.27.1 (assuming Router C's IP is 172.16.27.1):
Destination Prefix: 10.0.0.0
Destination Prefix Mask: 255.255.252.0
Interface: GigabitEthernet3
Install Static Route to 10.0.4.0/22 via 172.16.27.5 (assuming Router C's IP is 172.16.27.5):
Destination Prefix: 10.0.4.0
Destination Prefix Mask: 255.255.252.0
Interface: GigabitEthernet1
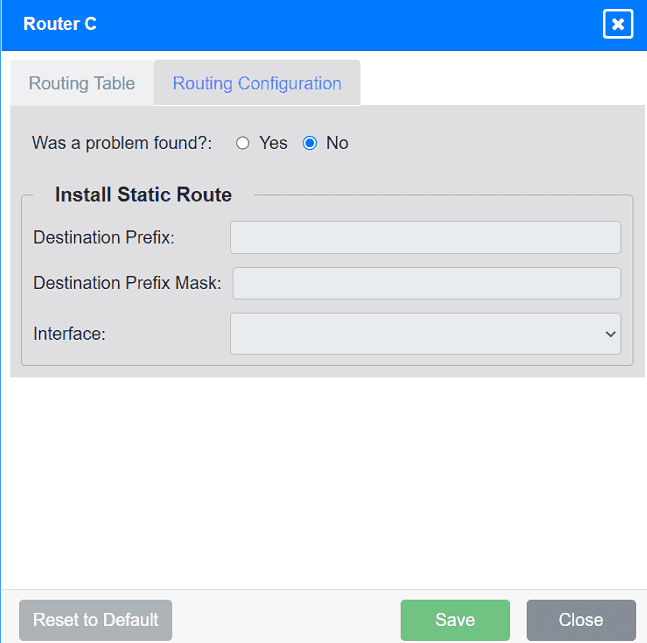
Install Static Route to 10.0.6.0/24 via 172.16.27.2 (assuming Router A's IP is 172.16.27.2):
Destination Prefix: 10.0.6.0
Destination Prefix Mask: 255.255.255.0
Interface: GigabitEthernet2
Install Static Route to 10.0.0.0/22 via 172.16.27.1 (assuming Router B's IP is 172.16.27.1):
Destination Prefix: 10.0.0.0
Destination Prefix Mask: 255.255.252.0
Interface: GigabitEthernet1
Summary of Static Routes:
Router A:
ip route 10.0.0.0 255.255.252.0 GigabitEthernet3
Router B:
ip route 10.0.4.0 255.255.252.0 GigabitEthernet1
Router C:
ip route 10.0.6.0 255.255.255.0 GigabitEthernet2
ip route 10.0.0.0 255.255.252.0 GigabitEthernet1
These configurations ensure that each router knows the correct paths to reach Workstation A and File Server 2, resolving the connectivity issue.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed