- 82 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All CompTIA Cybersecurity Analyst CySA+ V4 (New Version) Exam Questions with Validated Answers
| Vendor: | CompTIA |
|---|---|
| Exam Code: | CS0-004 |
| Exam Name: | CompTIA Cybersecurity Analyst CySA+ V4 (New Version) |
| Exam Questions: | 82 |
| Last Updated: | September 11, 2026 |
| Related Certifications: | CompTIA Cybersecurity Analyst |
| Exam Tags: | Cybersecurity certifications Intermediate CompTIA incident response analystCompTIA security operations center (SOC) analystCompTIA cyber professional |
Looking for a hassle-free way to pass the CompTIA Cybersecurity Analyst CySA+ V4 (New Version) exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by CompTIA certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our CompTIA CS0-004 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our CompTIA CS0-004 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the CompTIA CS0-004 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s CompTIA CS0-004 exam dumps today and achieve your certification effortlessly!
Which of the following is the most difficult for threat actors to change according to the Pyramid of Pain model?
Tactics, techniques, and procedures (TTPs) occupy the highest level of the Pyramid of Pain because they represent the adversary's operational behavior rather than disposable technical artifacts. The model describes how different types of defensive indicators impose progressively greater disruption on an attacker when defenders successfully detect and deny them.
An IP address is comparatively easy to replace by changing hosting infrastructure, using a proxy, acquiring a new virtual server, or moving command-and-control services. Domain names similarly can be registered or replaced with relatively limited operational impact. Tools create greater difficulty because replacing or substantially modifying malware, frameworks, or utilities requires more attacker effort.
TTPs are significantly more costly to change because they encompass how the adversary conducts operations: the sequence and methods used for initial access, persistence, credential access, privilege escalation, lateral movement, command and control, and other objectives. Forcing attackers to change established behavior may require retraining personnel, redesigning operational processes, developing new capabilities, or adopting unfamiliar techniques.
This is why behavioral detection is strategically valuable. Indicators such as hashes and IP addresses may disappear quickly, while detections focused on adversary behavior can remain useful across multiple toolsets and infrastructure changes.
Study Guide Reference: Security Operations Threat Intelligence Pyramid of Pain TTPs Behavioral Indicators Adversary Tracking.
A security operations center manager is concerned that after action reporting is not being completed in a timely manner.
Which of the following will allow the manager to quantify this concern?
Mean time to close is the most relevant measurement because the manager needs to quantify how long cases or incidents remain open before all required closure activities---including after-action documentation---are completed.
An incident may already be technically contained and remediated while administrative closure remains outstanding. Mean time to remediate measures how long it takes to correct or neutralize the security problem, but it does not necessarily include final reporting and formal case closure. Mean time to respond measures how quickly responders begin or perform response activity after detection. Mean time between failures is primarily a reliability metric describing the average operating duration between failures and does not measure SOC reporting performance.
Current Microsoft Sentinel SOC guidance explicitly includes mean time to closure and time-to-closure percentiles among incident-management metrics used to evaluate SOC performance. This directly maps to the manager's concern: if after-action reports delay completion of incidents, the organization's mean closure time will increase and can be trended by analyst, severity, team, or incident category.
Therefore, B provides the quantitative evidence needed to determine whether after-action reporting is preventing incidents from being closed promptly.
Study Guide Reference: Reporting and Communication Incident Metrics Mean Time to Close After-Action Reporting SOC Performance Measurement Continuous Improvement.
Which of the following occurs during the analysis phase of the incident response process?
Triage occurs during the analysis phase because responders must determine what an alert represents, how serious it is, which assets are affected, and what response priority should be assigned before taking broader containment or recovery actions.
Triage typically involves validating the alert, gathering supporting telemetry, establishing whether the event is a true positive, determining scope and impact, identifying affected identities or systems, correlating indicators, and assigning severity. The outcome provides the evidence required to decide whether an event should be escalated into formal incident handling and what subsequent actions are justified. NIST incident-handling guidance has historically emphasized analyzing incident-related information in order to determine the appropriate response, while the current NIST framework continues to emphasize efficient incident detection, response, and recovery.
Isolation belongs to containment because it restricts the compromised asset's ability to communicate or spread malicious activity. Reimaging normally occurs during recovery after the environment has been contained and malicious persistence addressed. Alert writing is part of detection engineering or security-monitoring operations rather than a defining incident-analysis activity.
The sequence is therefore important: detect analyze/triage contain eradicate recover conduct post-incident activities.
Study Guide Reference: Incident Response and Management Incident Response Process Detection Analysis/Triage Containment Eradication Recovery.
A cybersecurity analyst receives an unstructured text document that contains advanced persistent threat (APT)-related indicators of compromise (IoCs). The analyst needs to extract the IPv4 addresses.
Which of the following is the best tool to accomplish this task?
CyberChef is the most appropriate option because the task involves parsing and extracting structured indicators from unstructured text, rather than inspecting network traffic or managing a threat-intelligence repository. CyberChef provides operations for text manipulation, pattern matching, regular expressions, decoding, extraction, and transformation. An analyst can therefore feed the document into CyberChef and identify IPv4 address patterns without manually reviewing potentially thousands of characters.
Wireshark is primarily a packet-analysis platform. It would be appropriate if the analyst needed to inspect packets from a PCAP or live network capture, but the scenario provides a text document. Zeek is a network security monitoring and traffic-analysis framework that converts network activity into structured logs; it is similarly unnecessary for static textual extraction. OpenCTI is a threat-intelligence platform designed to organize, correlate, and manage intelligence objects and relationships. It could store the resulting IoCs after extraction, but it is not the most efficient tool for extracting IPv4 strings from raw text.
The official CS0-004 objectives identify CyberChef under decoding/parsing tools, while Wireshark and Zeek are classified under packet analysis and OpenCTI under threat-intelligence platforms.
Study Guide Reference: Security Operations Tools for Malicious-Activity Analysis Decoding/Parsing CyberChef Pattern Recognition/Regular Expressions IoC Analysis.
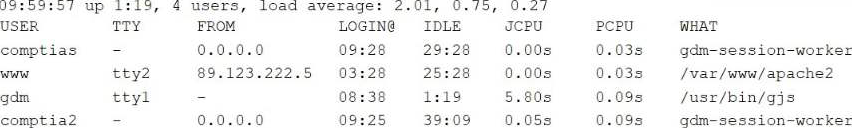
Based on recent alerts, a security analyst thinks a web application server was compromised. The analyst reviews the following server output:

Which of the following best describes what has occurred?
The server output indicates an initiated unauthorized session, which is the most significant security condition among the available answers. During compromise analysis, login/session data must be evaluated for unexpected users, remote origins, terminals, login times, active processes, and activity inconsistent with the server's expected operational baseline.
Linux session utilities provide precisely this type of evidence. The who utility reports users who are currently logged into a system, while w provides additional information such as the login name, terminal, remote host, login time, idle time, and currently associated process. An unexpected active session on a web application server---particularly one inconsistent with normal administrative activity---is therefore a material indicator of possible unauthorized access.
''Too many users'' would require evidence that session volume itself exceeded an established threshold. High resource consumption would instead require CPU, memory, load-average, or process-utilization evidence. Abnormal idle times might warrant investigation but do not independently establish compromise.
The analyst should treat the unauthorized session as an investigative pivot and correlate it with authentication logs, source addresses, process execution, privilege changes, and network connections.
Study Guide Reference: Incident Response and Management Analysis Host-Based Evidence User Sessions Authentication Activity Unauthorized Access Event Correlation.
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed