- 184 Actual Exam Questions
- Compatible with all Devices
- Printable Format
- No Download Limits
- 90 Days Free Updates
Get All Conducting Forensic Analysis and Incident Response Using Cisco Technologies for Cybersecurity Exam Questions with Validated Answers
| Vendor: | Cisco |
|---|---|
| Exam Code: | 300-215 |
| Exam Name: | Conducting Forensic Analysis and Incident Response Using Cisco Technologies for Cybersecurity |
| Exam Questions: | 184 |
| Last Updated: | September 14, 2026 |
| Related Certifications: | Cisco Certified Network Professional, Cisco Certified Network Professional Cybersecurity |
| Exam Tags: | Security Professional Evidence collection and analysisPrinciples of reverse engineer |
Looking for a hassle-free way to pass the Cisco Conducting Forensic Analysis and Incident Response Using Cisco Technologies for Cybersecurity exam? DumpsProvider provides the most reliable Dumps Questions and Answers, designed by Cisco certified experts to help you succeed in record time. Available in both PDF and Online Practice Test formats, our study materials cover every major exam topic, making it possible for you to pass potentially within just one day!
DumpsProvider is a leading provider of high-quality exam dumps, trusted by professionals worldwide. Our Cisco 300-215 exam questions give you the knowledge and confidence needed to succeed on the first attempt.
Train with our Cisco 300-215 exam practice tests, which simulate the actual exam environment. This real-test experience helps you get familiar with the format and timing of the exam, ensuring you're 100% prepared for exam day.
Your success is our commitment! That's why DumpsProvider offers a 100% money-back guarantee. If you don’t pass the Cisco 300-215 exam, we’ll refund your payment within 24 hours no questions asked.
Don’t waste time with unreliable exam prep resources. Get started with DumpsProvider’s Cisco 300-215 exam dumps today and achieve your certification effortlessly!
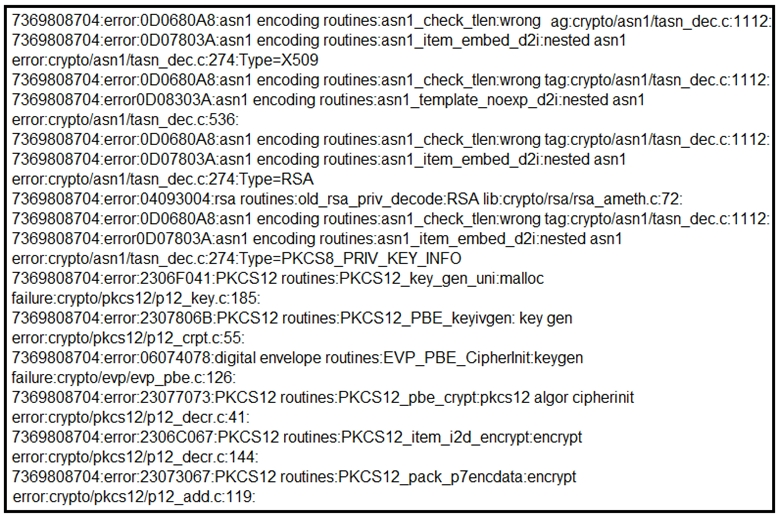
Refer to the exhibit.

What should be determined from this Apache log?
The error logs indicate multiple PKCS12 and ASN.1 decoding errors, such as:
PKCS12 routines:PKCS12_parse:mac verify failure
rsa routines:old_rsa_priv_decode:RSA lib
PKCS12 routines:PKCS12_key_gen_uni:malloc
These specific errors most commonly occur when:
The private key does not correspond to the certificate being used.
There is a mismatch between the public and private key pair required for SSL handshakes.
This is a well-documented condition in Apache SSL configuration issues and explicitly covered under TLS/SSL troubleshooting sections in cybersecurity operations contexts. The Cisco CyberOps guide also notes that SSL errors with key verification usually result from 'improper key/certificate pairing' rather than file corruption or missing modules.
Thus, the correct answer is:
B . The private key does not match with the SSL certificate.
Refer to the exhibit.

A security analyst is reviewing alerts from the SIEM system that was just implemented and notices a possible indication of an attack because the SSHD system just went live and there should be nobody using it. Which action should the analyst take to respond to the alert?
The log entry shows a failed SSH login attempt for an invalid user ''admin'' from IP 192.168.1.100. As the system has just gone live and no legitimate use is expected, this could be an early reconnaissance or brute-force attempt. However, blocking IPs or resetting passwords without fully understanding the context could lead to incomplete remediation or false positives.
According to Cisco CyberOps best practices, the first step is to thoroughly investigate the alert by correlating it with other logs (e.g., authentication logs, IDS/IPS logs) to determine the intent and scope of activity.
---
An engineer received a report of a suspicious email from an employee. The employee had already opened the attachment, which was an empty Word document. The engineer cannot identify any clear signs of compromise but while reviewing running processes, observes that PowerShell.exe was spawned by cmd.exe with a grandparent winword.exe process. What is the recommended action the engineer should take?
This behavior is consistent with malicious macro activity. A PowerShell process being spawned from winword.exe via cmd.exe strongly indicates execution of an embedded script. Cisco recommends containment as a critical next step:
'Contain the threat as soon as malicious behavior is observed to prevent lateral movement or additional compromise'.
A security team received an alert of suspicious activity on a user's Internet browser. The user's anti-virus software indicated that the file attempted to create a fake recycle bin folder and connect to an external IP address. Which two actions should be taken by the security analyst with the executable file for further analysis? (Choose two.)
Cisco Secure Malware Analytics (formerly Threat Grid) enables deep file behavior analysis, including TCP/IP stream analysis and behavioral indicators such as file system activity, process injection, registry changes, and command and control communication. These are essential in understanding what the suspicious file does post-execution, especially given the described behavior of creating a fake folder and outbound connection attempts.
---
An organization fell victim to a ransomware attack that successfully infected 256 hosts within its network. In the aftermath of this incident, the organization's cybersecurity team must prepare a thorough root cause analysis report. This report aims to identify the primary factor or factors that led to the successful ransomware attack and to develop strategies for preventing similar incidents in the future. In this context, what should the cybersecurity engineer include in the root cause analysis report to demonstrate the underlying cause of the incident?
According to the Cisco CyberOps Associate guide, the goal of a root cause analysis is to determine how an attacker successfully exploited a system so that similar vulnerabilities can be mitigated in the future. The 'method of infection' (e.g., phishing email with malicious attachment, drive-by download, credential compromise, etc.) is the most relevant factor in understanding the initial access vector and subsequent spread of ransomware across the network.
---
Security & Privacy
Satisfied Customers
Committed Service
Money Back Guranteed